mirror of
https://github.com/coder/coder.git
synced 2026-09-22 05:05:20 +08:00
fe4a73f8ab1b784e8af6f197c20122d7993270bc
15604
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 dylanhuff-at-coderandNick Vigilante |
fe4a73f8ab |
docs: note user secret target uniqueness and delivery boundary (#27532)
Two gaps in the user secrets guide, both independent of any pending secrets work. ## Changes **Target uniqueness (`Update a secret`, `File secrets`).** The guide teaches `coder secret update api-key --file ""` but never states that env names and file paths are unique per user, so the conflict you get when setting a target back has no explanation in the docs. The `File secrets` paragraph also read as though duplicate file paths are tolerated with a warning; an identical path is rejected outright, while two *different* paths resolving to the same location are both accepted and produce the agent warning. Both indexes are partial (`WHERE env_name != ''` / `WHERE file_path != ''`), so a cleared target really is released for another secret to claim — now stated. **Delivery boundary (`How your secrets reach a workspace`).** Coder controls where a secret is delivered, not whether it is still valid. Nothing done in Coder revokes a credential a workspace already received, so an exposed credential is rotated at its source. This applies to deletion as much as to clearing a target. No new headings, no changes to the existing tables or callouts. > This PR was generated by Coder Agents on behalf of @dylanhuff-at-coder. --------- Co-authored-by: Nick Vigilante <nickvigilante@users.noreply.github.com> |
||
|
Rowan SmithandAtif Ali
|
f44e8c12d6 |
fix: support adding multiline secrets via the UI (#27253)
**Summary**

Root cause (confirmed by reading SecretDialog.tsx): the Value field on
the User Secrets "Add secret"/"Edit secret" dialog was rendered as
<Input type="text">, a single-line HTML control, so pasting a multiline
kubeconfig/PEM/YAML got visually collapsed and the newlines were lost
before the value ever reached the form state or the API request.

Fix applied in
site/src/pages/UserSettingsPage/SecretsPage/SecretDialog.tsx:

* Swapped the Value field's <Input> for the same <Textarea> component
already used for the Description field (which correctly preserves
multiline text).
* Added rows={4} so the box is usable for multiline content, and
font-mono for readability of config-like values.
* Kept the "mask typed value" obscuring behavior but switched
-webkit-text-security:circle to :disc (Chromium's supported keyword for
<textarea>; circle is input-specific and silently no-ops on textareas).
* Removed the now-unused Input import.
* All existing onFocus/onChange/onBlur masking/saved-value logic was
preserved as-is; FormHelpers types already supported
HTMLTextAreaElement, so no type changes were needed.

Test fix in
site/src/pages/UserSettingsPage/SecretsPage/SecretsPageView.stories.tsx:
the EditSecretClearValue story's toBeVisible() assertion on the helper
text was racing the render/layout commit (this test already used a
waitFor for an analogous transient-visibility check on the neighboring
Clear button). The taller textarea shifted that timing enough to expose
the race consistently when run as part of the full suite. Wrapped the
assertion in waitFor(...) to match the existing pattern.

*Created with the help of Mux and Sonnet, tested by a human*

Working with a secret file like this:
```
➜  Downloads cat ~/.kube/config
apiVersion: v1
clusters:
  - cluster:
        certificate-authority-data: LS0tLS1CRUdJTiBDRVJUSUZJQ0FURS0tLS0tCk1JSUJkakNDQVIyZ0F3SUJBZ0lCQURBS0JnZ3Foa2pPUFFRREFqQWpNU0V3SHdZRFZRUUREQmhyTTNNdGMyVnkKZG1WeUxXTmhRREUzTWpBNU16VTFOelV3SGhjTk1qUXdOekUwTURVek9UTTFXaGNOTXpRd056RXlNRFV6T1RNMQpXakFqTVNFd0h3WURWUVFEREJock0zTXRjMlZ5ZG1WeUxXTmhRREUzTWpBNU16VTFOelV3V1RBVEJnY3Foa2pPClBRSUJCZ2dxaGtqT1BRTUJCd05DQUFTK1JRaUlLa0RVV0tKR0Y0ZFdnbWZSVTA1Wjg1ellQSWt6aWlHUXdBZ1gKMXdyQThhNVRRbzVuYlJmeWxRQXZtZDB1SE04a05GTmZIYXJwc3lxZkZyS0dvMEl3UURBT0JnTlZIUThCQWY4RQpCQU1DQXFRd0R3WURWUjBUQVFIL0JBVXdBd0VCL3pBZEJnTlZIUTRFRmdRVTBmUHdjMWpnd1BraFN2Q0cwbjQ1CnZTV09ES1V3Q2dZSUtvWkl6ajBFQXdJRFJ3QXdSQUlnQ3RCRm5KR0VJVVRSZ1RRaXZFSWJIODVwQnlMdmx1RjMKQ2ZTRFhDc3hlaWtDSUF4a0JKWnJ2eUUzQzNWRWdVT0t2d2VzVUN4cFBOendpbkg5Qkd4TXJuTk4KLS0tLS1FTkQgQ0VSVElGSUNBVEUtLS0tLQo=
        server: https://192.168.50.23:6443
    name: k3s-3-pi
```

Created via the UI in 2.35.1:
```
coder_dev=> select * from user_secrets;
-[ RECORD 1 ]+-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------
id           | 12853b89-a56b-408a-a9b0-11591ed04898
user_id      | 2702b6f3-b094-47ee-975e-47dc7887dbed
name         | kubeconfig
description  |
value        | apiVersion: v1 clusters:   - cluster:         certificate-authority-data: LS0tLS1CRUdJTiBDRVJUSUZJQ0FURS0tLS0tCk1JSUJkakNDQVIyZ0F3SUJBZ0lCQURBS0JnZ3Foa2pPUFFRREFqQWpNU0V3SHdZRFZRUUREQmhyTTNNdGMyVnkKZG1WeUxXTmhRREUzTWpBNU16VTFOelV3SGhjTk1qUXdOekUwTURVek9UTTFXaGNOTXpRd056RXlNRFV6T1RNMQpXakFqTVNFd0h3WURWUVFEREJock0zTXRjMlZ5ZG1WeUxXTmhRREUzTWpBNU16VTFOelV3V1RBVEJnY3Foa2pPClBRSUJCZ2dxaGtqT1BRTUJCd05DQUFTK1JRaUlLa0RVV0tKR0Y0ZFdnbWZSVTA1Wjg1ellQSWt6aWlHUXdBZ1gKMXdyQThhNVRRbzVuYlJmeWxRQXZtZDB1SE04a05GTmZIYXJwc3lxZkZyS0dvMEl3UURBT0JnTlZIUThCQWY4RQpCQU1DQXFRd0R3WURWUjBUQVFIL0JBVXdBd0VCL3pBZEJnTlZIUTRFRmdRVTBmUHdjMWpnd1BraFN2Q0cwbjQ1CnZTV09ES1V3Q2dZSUtvWkl6ajBFQXdJRFJ3QXdSQUlnQ3RCRm5KR0VJVVRSZ1RRaXZFSWJIODVwQnlMdmx1RjMKQ2ZTRFhDc3hlaWtDSUF4a0JKWnJ2eUUzQzNWRWdVT0t2d2VzVUN4cFBOendpbkg5Qkd4TXJuTk4KLS0tLS1FTkQgQ0VSVElGSUNBVEUtLS0tLQo=         server: https://192.168.50.23:6443     name: k3s-3-pi
env_name     |
file_path    | ~/.kube/config
created_at   | 2026-07-15 15:55:07.438234+10
updated_at   | 2026-07-15 15:55:07.438234+10
value_key_id |
```

Post change:
```
coder=# select * from user_secrets ;
-[ RECORD 1 ]+-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------
id           | 7c4858bc-ee87-45f0-b85d-0e9b1474d69c
user_id      | 0f0a590b-0358-4a24-bb25-ccc936bcc8d6
name         | kubeconfig
description  |
value        | apiVersion: v1                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                          +
             | clusters:                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                               +
             |   - cluster:                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                            +
             |         certificate-authority-data: LS0tLS1CRUdJTiBDRVJUSUZJQ0FURS0tLS0tCk1JSUJkakNDQVIyZ0F3SUJBZ0lCQURBS0JnZ3Foa2pPUFFRREFqQWpNU0V3SHdZRFZRUUREQmhyTTNNdGMyVnkKZG1WeUxXTmhRREUzTWpBNU16VTFOelV3SGhjTk1qUXdOekUwTURVek9UTTFXaGNOTXpRd056RXlNRFV6T1RNMQpXakFqTVNFd0h3WURWUVFEREJock0zTXRjMlZ5ZG1WeUxXTmhRREUzTWpBNU16VTFOelV3V1RBVEJnY3Foa2pPClBRSUJCZ2dxaGtqT1BRTUJCd05DQUFTK1JRaUlLa0RVV0tKR0Y0ZFdnbWZSVTA1Wjg1ellQSWt6aWlHUXdBZ1gKMXdyQThhNVRRbzVuYlJmeWxRQXZtZDB1SE04a05GTmZIYXJwc3lxZkZyS0dvMEl3UURBT0JnTlZIUThCQWY4RQpCQU1DQXFRd0R3WURWUjBUQVFIL0JBVXdBd0VCL3pBZEJnTlZIUTRFRmdRVTBmUHdjMWpnd1BraFN2Q0cwbjQ1CnZTV09ES1V3Q2dZSUtvWkl6ajBFQXdJRFJ3QXdSQUlnQ3RCRm5KR0VJVVRSZ1RRaXZFSWJIODVwQnlMdmx1RjMKQ2ZTRFhDc3hlaWtDSUF4a0JKWnJ2eUUzQzNWRWdVT0t2d2VzVUN4cFBOendpbkg5Qkd4TXJuTk4KLS0tLS1FTkQgQ0VSVElGSUNBVEUtLS0tLQo=+
             |         server: https://192.168.50.23:6443                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              +
             |     name: k3s-3-pi
env_name     |
file_path    | ~/.kube/config
created_at   | 2026-07-15 15:49:08.772126+10
updated_at   | 2026-07-15 15:53:39.375332+10
value_key_id |
```

And displayed correct in the Coder workspace:
<img width="508" height="238" alt="image"
src="https://github.com/user-attachments/assets/a0e9208e-cb73-4636-94e4-a67dcb510da4"
/>


Add secret UI is now a multiline input box:
<img width="534" height="839" alt="image"
src="https://github.com/user-attachments/assets/6e2a89a3-bef2-40c0-852e-0c9ac8e2f0cd"
/>

Co-authored-by: Atif Ali <atif@coder.com>
|
||
|
Ben Potter
|
8a4adeec32 |
fix(agent): detect IPv6-bound listening ports (#27765)
Closes https://github.com/coder/coder/issues/15675 Dev servers that bind to the IPv6 wildcard address (Next.js, Node's default `http.Server`, Go's `net.Listen` on wildcard addresses, and others) never showed up in the dashboard Ports panel, even though they were listening and reachable. The agent's port scanner only called `netstat.TCPSocks`, which reads `/proc/net/tcp` (IPv4 only); an `[::]` dual-stack socket lives exclusively in `/proc/net/tcp6`, so the panel reported "No open ports were detected." Also scan `netstat.TCP6Socks` and merge the results into the existing dedupe loop. The IPv6 scan failure is non-fatal so hosts with IPv6 disabled (missing `/proc/net/tcp6`, Windows with the v6 stack off) keep their IPv4 results instead of the Ports panel 500ing. Both captures below: `python3 -m http.server 5123 --bind ::` running in the same workspace, built from main vs this branch ([full recordings](https://github.com/coder/coder/tree/recordings/recordings/ipv6-listening-ports)). ## Before 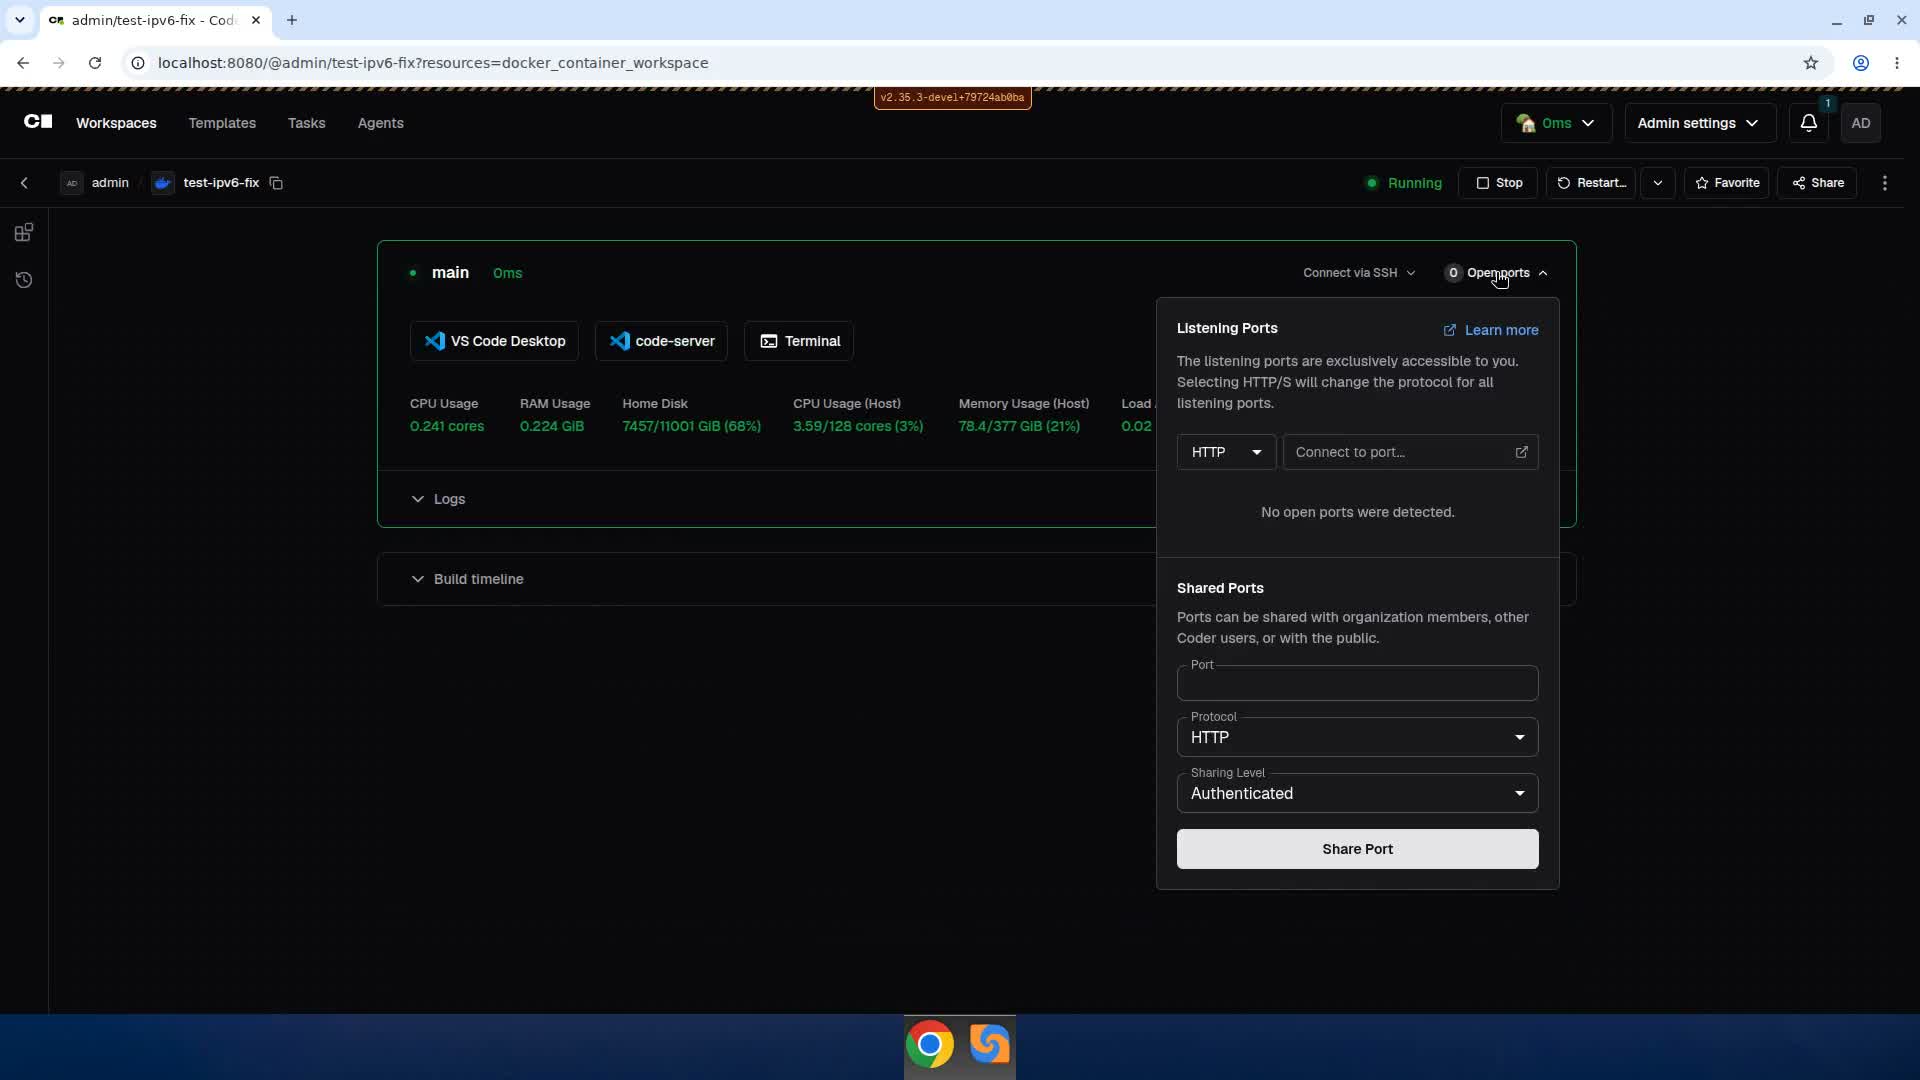 ## After  <details> <summary>Debugging and decision log</summary> - Reproduced on a dogfood workspace: `next-server` listening on `*:3000` per `ss -tlnp`, `curl` returning 200, but `GET /api/v2/workspaceagents/{agent}/listening-ports` returning `{"ports": []}`. Port 3000 (hex `0BB8`) present in `/proc/net/tcp6`, absent from `/proc/net/tcp`. - Confirmed `agent/ports_supported.go` only calls `netstat.TCPSocks`; the library's `TCP6Socks` (parses `/proc/net/tcp6` on Linux, `GetTcp6Table2` on Windows) was never referenced. - Control test: an IPv4-bound (`0.0.0.0`) listener was detected correctly, isolating the bug to the missing IPv6 scan. - Made the IPv6 scan failure non-fatal after review: returning an error would break the entire ports endpoint (HTTP 500 on every poll) on IPv6-disabled hosts, a regression from the current behavior of "IPv4 ports only." Silent fallback matches the spirit of `ports_unsupported.go`, which returns an empty list rather than erroring. - The fix lives in the OS-backed `osListeningPortsGetter` behind the `ListeningPortsGetter` interface from #20842, so the fake used by coderd tests is unaffected. - Dedupe by port in the existing `seen` map covers dual-stack sockets that appear in both tables on Windows. - `TestOSListeningPortsGetter_IPv6` listens on `[::]:0` and asserts detection; it skips when the host can't bind IPv6. Verified it fails against the pre-fix code. </details> > 🤖 This PR was opened by [Coder Agents](https://coder.com/docs/ai-coder/agents) on behalf of @bpmct. |
||
|
Nick Vigilante
|
71c7e92084 |
ci: broaden linkspector Stack Overflow ignore for weekly docs check (#27799)
## Problem The weekly docs link check ([`weekly-docs`](https://github.com/coder/coder/blob/main/.github/workflows/weekly-docs.yaml) -> [linkspector](https://github.com/UmbrellaDocs/linkspector)) is failing. - **Failing run:** https://github.com/coder/coder/actions/runs/30805217850/job/91691078170 - **Broken link:** `https://stackoverflow.com/a/55570286` in `docs/admin/users/idp-sync.md` (line 576), reported `Status: 403`. Stack Overflow returns `403` to the GitHub runner IPs (bot detection), so a valid link is flagged as broken. This is the same false-positive mode already handled for `npmjs.com`, `merriam-webster.com`, `splunk.com`, etc. in `.github/.linkspector.yml`. ## Fix / why a bare `stackoverflow.com` pattern linkspector matches `ignorePatterns` as regex substrings against each URL. The config already ignored `stackoverflow.com/questions`, but the failing URL is an **answer** link (`/a/...`) that the `/questions` pattern does not cover, and it has no `www.` prefix, so a `www.stackoverflow.com` entry would not match it either. Broadening to a bare `stackoverflow.com`: - fixes the failing `/a/55570286` link; - keeps the existing `/questions/...` link in `docs/about/contributing/frontend.md` covered (so the now-redundant `stackoverflow.com/questions` line is removed); - also covers any `www.` variant. ## Validation - Confirmed the `stackoverflow.com` regex matches `/a/`, `/questions/`, and `www.` variants; config parses; `typos` clean. - The `weekly-docs` `pull_request` trigger is path-filtered to `docs/**`, so this `.github/`-only change does not auto-run linkspector here. Validated end-to-end via a manual `workflow_dispatch` on this branch, which passed: https://github.com/coder/coder/actions/runs/30829301773 <details> <summary>Unrelated failing check: <code>Pixel / Review</code> (visual regression)</summary> `Pixel / Review` reports failed visual tests ([build 6916](https://pixel.coder.com/@coder/coder/builds/6916)). This PR only edits `.github/.linkspector.yml` (link-checker config) and changes no UI, components, or rendered output, so these are pre-existing visual-baseline diffs / flakes unrelated to this change. All path-relevant required checks (`fmt`, `gen`, `lint`, `changes`, `title`, `Storybook`, `Flake Check`) pass. </details> Linear: [DOCS-606](https://linear.app/codercom/issue/DOCS-606/fix-weekly-docs-link-check-allowlist-stack-overflow-in-linkspector) > This PR was created with AI assistance (Coder Agents). |
||
|
|
ba4779fc87 |
docs: lead with env vars in admin docs and add configuration reference (#26824)
## What & why Admin/setup docs lead with `coder server --flag` examples, but most operators configure Coder through `CODER_*` environment variables (system service, container, or Helm chart). There is no single page mapping a setting to its env var, CLI flag, YAML key, and default, so searching the docs for an env var name such as `CODER_PG_CONNECTION_URL` returns nothing. This adds a generated configuration reference and begins shifting admin docs to lead with the environment-variable form. ## Changes - **Generated configuration reference** (`docs/admin/setup/configuration-reference.md`): a searchable, per-setting list of every visible deployment option. Each option is a heading (grouped and nested by serpent group) followed by its description and the environment variable, CLI flag, YAML key, and default that apply to it. Generated from `codersdk.DeploymentValues` so it stays in sync. - **Generator + `make gen` wiring** (`scripts/configdocgen/`): new binary plus a Makefile target and `GEN_FILES` entry, mirroring the existing `clidocgen` / `auditdocgen` pattern. Output is host-independent (same env normalization as `clidocgen`). - **Demo conversion** (`docs/admin/users/github-auth.md`): inverted to lead with the `/etc/coder.d/coder.env` env-var form; the CLI-flag form becomes a closing note that links to the reference. H2 slugs preserved. - **Style guide** (`.claude/docs/DOCS_STYLE_GUIDE.md`): documents the env-var-first convention for admin/setup docs. - **Navigation**: manifest entry under Administration → Setup, plus a TIP callout on the setup index. ## Risk Docs + gen pipeline only; no runtime change. The page is regenerated by `make gen`; the `gen` and `check-docs` CI checks pass. ## Follow-up Several other admin pages still lead with flag walls. Recommend sweeping them incrementally in separate PRs rather than expanding scope here. <details> <summary>Implementation notes (provenance, conflict resolution, verification)</summary> - Continues prior work by @aslilac and @bpmct from the `kayla/docs-env-vars-first` branch. Both original commits are cherry-picked here with authorship preserved. - Rebased onto current `main`. Resolved two `Makefile` conflicts where `main` had since added the `feature-stages.md` gen target at the same locations; kept both targets (union) in `GEN_FILES`, `gen/mark-fresh`, and the recipe block. - The original branch's checked-in page predated recent `codersdk.DeploymentValues` changes, so it was **regenerated** against current `main` (adds `CODER_SCIM_USE_LEGACY`, the `Networking / Cluster` section with `CODER_CLUSTER_HOST`, `CODER_BOUNDARY_LOG_RETENTION`, and the AI Gateway description rename). The `gen` CI check enforces this stays current. - Fixed flag-link anchors for short-form flags (`--config`, `--log-filter`): the generator derives the anchor from `FlagShorthand` to match `clidocgen`'s heading (e.g. `#-l---log-filter`). - `linkspector` ignores the AWS Bedrock base URL that appears as an illustrative `<region>` placeholder in an option description, consistent with the existing `openai.com` ignore patterns. </details> <details> <summary>Configuration reference layout (2026-07-08 update)</summary> Reworked the reference from a wide table into a nested, per-setting list so it fits without horizontal scrolling and stops repeating the group name in every heading: - **List, not table.** Each option renders as a heading, its description, and a bullet list of only the configuration methods that apply to it (non-applicable methods are omitted instead of shown as `-`). - **Nested sections.** Sections nest by the serpent group hierarchy, so `Email / Email Authentication` becomes `Email` (h2) with an `Email authentication` (h3) subsection instead of a redundant flat title. - **Shorter, sentence-case headings.** The redundant group prefix is stripped from each option name and the remainder is lowercased to sentence case, preserving acronyms and mixed-case tokens (`URL`, `TLS`, `OAuth2`, `GitHub`) plus a small proper-noun allowlist (`Coder`, `Terraform`, `Honeycomb`, `Anthropic`, `Bedrock`, ...). Example: `AI Gateway Send Actor Headers` becomes `Send actor headers`. - **Deprecated options** sort to the end of each section and lead with an emphasized **Deprecated** marker. Headings stay clean (no `(deprecated)` suffix) so their anchors remain stable. - **Section intros** render from a group's `Description` when the source defines one (e.g. DERP); no hand-maintained prose or links are introduced. All transformations run in pure Go at `make gen` time (no AI at generation time). Generation is idempotent, and `markdownlint` and `golangci-lint` both pass. </details> --- 🤖 Opened by Coder Agents on behalf of @nickvigilante. Continues work by @aslilac and @bpmct. --------- Co-authored-by: Kayla (via Coder Agents) <kayla@coder.com> Co-authored-by: Coder Agents <noreply@coder.com> Co-authored-by: Ben Potter <me@bpmct.net> |
||
|
Nick Vigilante
|
ee7e7ecb74 |
docs: add a glossary to the reference section (#27165)
Adds a reference glossary at `docs/reference/glossary.md` that defines
the Coder-specific terms and product names readers encounter across the
docs, and registers it in `docs/manifest.json` under **Reference**.
The page prioritizes the term collisions around "agent": it
disambiguates Coder Agents (the AI product), the workspace agent (the
in-workspace daemon), and the `coder_agent` Terraform resource with an
`[!IMPORTANT]` callout and cross-referenced entries. Every definition
was checked against the current docs, and every internal link is a
relative path that resolves in-repo.
Decision log and verification notes
**Scope of this PR**
- Creates the glossary page (`docs/reference/glossary.md`) and its
manifest entry.
- Adds glossary drift-prevention guidance in response to review feedback
(see **Follow-up from review** below).
- Out of scope (tracked separately): `Glossary: ` cross-link callouts
across the docs IA, the search-ranking boost, the workspace-daemon
rename decision, and the automated glossary lint guard
([DOCS-604](https://linear.app/codercom/issue/DOCS-604)).
**Follow-up from review (@bpmct)**
Ben flagged the risk that terms get introduced, renamed, or deprecated
without the glossary keeping up. Addressed in commit
|
||
|
Steven Masley
|
76eb43a78e |
test(coderd): drain dormancy audit log before reset in StartWakesUpDormantWorkspace (#27541)
Closes PLAT-219 / [coder/internal#1532](https://github.com/coder/internal/issues/1532). The reported failure (`should have 2 item(s), but has 3`) was the stop build's outcome audit landing after `auditor.ResetLogs()`; that path was already deflaked by #26232 and the pre-reset drain added in #25037. This closes the remaining hole in the same class: the dormancy update's audit log is exported in a middleware `defer` after the API response, so it can also land after `ResetLogs` and break the exact `len == 2` assertion. Extend the pre-reset poll to drain the dormancy write entry alongside the stop build entry. Verified with `go test ./coderd -run TestWorkspaceDormant -count=5` and `-race`. > Generated by Coder Agents on behalf of @Emyrk. |
||
|
Michael Suchacz
|
6e5f02bfbe |
fix: bound golangci-lint memory to stop lint OOM kills (#27637)
## Summary Reduce peak memory during linting so cold-cache runs do not exhaust memory on high-core development hosts or leave CI runners with little headroom. ## Problem `golangci-lint` v1 sizes its default concurrency from available CPUs, not the cgroup memory limit. On a 96-CPU development host capped at 32 GiB, a cold-cache full lint run peaked at about 33.9 GB and reached the cgroup limit. The CI workflow also used bare `make -j`, which allows every lint target to run concurrently. ## Fix Make the supported `make lint/go` path cap `golangci-lint` at the lower of detected CPUs and eight workers, preserving lower concurrency on smaller hosts. Preserve an inherited `GOMEMLIMIT`, use a configurable 8 GiB fallback when it is unset, and bound CI's parallel lint targets to the runner CPU count. In the same high-core cold-cache reproduction, peak memory for the full lint target fell to about 10.1 GB. Raw `golangci-lint run` invocations remain unchanged. A `golangci-lint` v2 migration remains separate because it does not size concurrency from the memory limit and requires broader configuration migration work. > Mux prepared and updated this PR on Mike's behalf. |
||
|
Nick Vigilante
|
4e54f311bd |
Revert "chore: add @coder/docs as a CODEOWNER for docs content and tooling" (#27802)
Reverts coder/coder#27240 The emails got too spammy, and so we need to find another mechanism to track PRs and how well each PR is documented. |
||
|
Stefan Richter
|
24ff135801 |
feat(helm/coder): make HTTPS redirect status code configurable (#27360)
Add coder.httproute.httpsRedirect.statusCode to configure the HTTPRoute redirect response code, defaulting to 308. Validate that the value is one of 301, 302, 303, 307, or 308. <!-- If you have used AI to produce some or all of this PR, please ensure you have read our [AI Contribution guidelines](https://coder.com/docs/about/contributing/AI_CONTRIBUTING) before submitting. --> |
||
|
Michael Suchacz
|
fc24c27dfd |
fix: reserve chat hook dispatch capacity for running turns (#27656)
## Context Follow-up fix from live UAT of the merged chat lifecycle hooks stack (#27430). Its companion UAT fix (#27655) has merged, so this targets `main` directly. ## Why? UAT measured a burst of 1,500 concurrent chat creations against a consumer with 1.2s latency. 255 were admitted and 1,245 got `502 hook_dispatch_failed (over_capacity)`, which is correct fail-closed behavior. The collateral wasn't: the same burst failed 24 `stop` dispatches, parking chats that had already been admitted and had already executed tools. One 256-slot semaphore served every event, so new-work admission could take every slot and kill turns in flight. Callers now classify each dispatch as admission or generation, and admission draws from a 192-slot gate held *before* the shared pool. At least 64 shared slots stay reachable only by dispatches for work a chat already admitted. The dispatcher is per `coderd` replica, so these limits are per replica, not deployment-wide, and the docs say so. **The caller classifies, not the event type.** Event type isn't a reliable proxy in either direction: a subagent spawn dispatches `user_prompt_submit` from inside a running turn, and the edit path dispatches `session_start` at admission time. `CapacityClassUnset` is rejected in `Dispatch`, so a new call site fails closed rather than silently inheriting a share. **Acquisition order is load-bearing.** Admission takes its own gate first. Taking a shared slot first would let admissions queued on the gate occupy the very capacity the reserve protects. `acquireCapacity` is the only path that takes either pool, so the order can't be bypassed. ## What this does not guarantee Nothing bounds how many turns generate concurrently, so the 192/64 split is a judgement call, not a derived ceiling. This stops an *admission* burst from consuming every slot; it does not make the remainder sufficient. A large enough generation load can still exhaust the reserve and error a running chat. The docs say so explicitly rather than promising a guarantee the code doesn't deliver. Generation can now take all 256 slots, so generation traffic starves admission harder than before. That's the intended priority: rejecting a new prompt is recoverable, ending a turn that already ran tools is not. ## Testing Red-green proved both new tests. Removing the release-on-failure path fails `RefusedSharedAcquireReleasesAdmission` deterministically; removing the expired-deadline check fails `ExpiredDeadlineRefusesFreeSlot` in 18/30 runs. That deadline check fixes a real race found in review. `acquire` previously shared one `time.Timer` across both acquires. Because `select` picks a ready case at random, an admission dispatch could take a slot after its capacity deadline had passed. Measured over 300 trials: 135 late acquisitions, worst overshoot 2.1ms. `acquire` now takes an absolute deadline and refuses an expired one before selecting, which measures 0/300. Go: `coderd/x/agenthooks/...` and `coderd/x/chatd/...`, plus `-race -count=3` on the dispatcher. > Mux opened this PR on Mike's behalf. |
||
|
Fabien Penso
|
7bd9f5ec93 |
fix: correct authorization header spelling in api docs (#27721)
Corrects the misspelled `Authorizaiton` Swagger header name to `Authorization` in the source annotation and checked-in generated API documentation. This prevents generated API specs and SCIM examples from documenting the wrong HTTP header name. |
||
|
Michael Suchacz
|
df1c0f9710 |
feat: show what a chat lifecycle hook changed (#27655)
## Stack Context Follow-up fixes from live UAT of the merged chat lifecycle hooks stack (#27430). Two PRs: 1. **This PR**: make hook effects visible and correctly attributed in the transcript. 2. [`mike/chat-hooks-uat/dispatch-capacity`]: reserve dispatch capacity so an admission burst can't fail running turns. ## Why? UAT found three ways the transcript misrepresented what a lifecycle hook did. All three are user-visible and share the same surface (`chathooks/effects.go`, `codersdk.ChatMessagePart`, the conversation timeline), so they're reviewed together. **A prompt `input_override` silently discarded attachments.** `ComposeUserPromptContent` replaced the entire submitted part list with one text part, dropping `file` and `file-reference` parts along with their `chat_file_links`. The user saw their attachments vanish with no explanation. The override now replaces submitted *text* parts only and preserves non-text parts in order. A consumer that wants to block attachments uses `deny`, which is the documented mechanism for refusing a submission. **Every user-visible `system` row was labelled "Lifecycle hook".** The timeline keyed the notice off `role === "system"`. That was correct only by accident, because the hook `user_message` was the sole client-visible system row. The backend now emits the notice as a typed `hook-notice` part and the timeline renders on that, so a future system row can't be mislabelled as a policy notice. **Nothing marked a tool call the hook had rewritten.** A consumer could replace tool input via `input_override` and the transcript showed the rewritten input as if the model had produced it. `ChatMessagePart` gains `hook_rewritten`, set from `preflight.Overrides` on the same path that already carries `ToolCallCreatedAt`, and the tool row renders a "Modified by policy" badge. `ToolCall.PolicyProvider` renders the badge itself, at four wrap sites: the `Tool` dispatch wrapper, the `ReadFilesTool` aggregate and its per-file rows, and `ReadFileTimelineBlock` (grouped and single `read_file` rows bypass `Tool`). Renderer props do not include the flag; descendants consume it through the provider context. The badge is emitted by the provider rather than by the shared header because several renderer branches return early without one, including the auth-required `execute` card, a completed `ask_user_question`, and an empty question payload. Those branches would drop the attribution with no type or runtime error, and the gap is not greppable: every renderer file contains a header somewhere, only individual branches do not. Emitting at the provider removes the possibility instead of enumerating the cases. A rewritten call is wrapped in a group labelled by its badge, so one rewritten file inside a merged read is attributed on its own rather than inheriting the group's badge. `HeaderButton` still appends the policy wording to an explicit `ariaLabel`, since an explicit `aria-label` replaces the name computed from descendants. Provider-executed calls are excluded from attribution. Hooks never see them, and duplicate tool-call ID rejection deliberately skips them, so a reused ID would otherwise mark a provider-executed call as policy-rewritten. ## Testing Go: `coderd/x/chatd/...`, `coderd/x/agenthooks/...`, `codersdk/...`, and `coderd -run 'Hook|Chat'`. Frontend: `tsc` plus every `AgentsPage` story; the only failures are `MCP Tool Completed` and `Scroll To Bottom Button Works With Inverse Scroll`, both of which fail on trunk. A registry-wide story asserts every registered renderer shows the badge, verified against three inverted toggles: removing the badge, hiding it with `display:none`, and skipping the provider for one renderer (which names that renderer). Storybook also covers the rewritten subagent spawn, a completed empty question payload, a non-hook system message, and a failed `read_file` guarding the accessible name. > Mux opened this PR on Mike's behalf. |
||
|
Bobby HoandTracy Johnson
|
4245e4e378 |
feat: expose dynamic client registration in deployment settings (#27480)
Adds the admin-controlled OAuth2 Dynamic Client Registration setting landed by #27316 (`GET`/`PUT /api/v2/oauth2-provider/settings`) to the OAuth2 Applications deployment settings page, since it was previously only reachable via the API or `coder oauth2-provider dcr enable|disable`. The page is now tabbed, **Applications** and **Settings**, so DCR has a home that further OAuth2 settings can share (an Initial Access Token setting is a likely next one). The active tab is backed by a `tab` search param, so `?tab=settings` links straight to it, and an unpermitted deep link falls back to **Applications** rather than selecting nothing. On the Settings tab, DCR renders as a titled section with a description, an `Enabled` badge when active, and an Enable/Disable button. Enabling opens a confirmation dialog, since it lets any OAuth2 client self-register against the deployment without prior admin approval (RFC 7591). Disabling is immediate, no confirmation. The control is a button rather than a switch on design feedback: a switch reads as an immediate on/off flip, which conflicts with a confirmation dialog standing in front of it, and it left the only explanation of the risk inside a dialog that disappears. A button carries the confirmation step without misrepresenting what a click costs, the always-visible description explains the setting on the page, and the `Enabled` badge gives the active state a persistent indicator. The layout follows Tracy's mockup on `tj/oauth2-apps-pagination`; the apps-table pagination work that shares that branch is deliberately not included here. Visibility and editability are gated on the same `ResourceDeploymentConfig` RBAC checks the endpoint itself enforces (`viewDeploymentConfig` / `editDeploymentConfig`), not a separate hardcoded check. The view takes the settings values as one optional `settings` prop, absent when the viewer lacks `viewDeploymentConfig`, so "cannot view" is the shape of the prop rather than a flag the caller keeps consistent with the values beside it, and the tab is not rendered at all. Closes https://github.com/coder/coder/issues/27432 ## Where this sits in the request path ```mermaid sequenceDiagram autonumber actor Admin participant View as OAuth2AppsSettingsPageView<br/>(Tabs + Enable/Disable + Dialog) participant Page as OAuth2AppsSettingsPage<br/>(React Query) participant S as coderd Note over Page: On mount Page->>S: GET /api/v2/oauth2-provider/settings S-->>Page: { dynamic_client_registration_enabled } Page-->>View: settings: { dynamicClientRegistrationEnabled, canEdit, ... } Note over Admin,View: Admin opens the Settings tab and enables DCR Admin->>View: click "Enable" View->>View: open confirmation dialog<br/>(no request sent yet) Admin->>View: click Confirm View->>Page: settings.onDynamicClientRegistrationChange(true) Page->>S: PUT /api/v2/oauth2-provider/settings<br/>{dynamic_client_registration_enabled: true} S-->>Page: 200 OK (audited) Page->>S: GET /api/v2/oauth2-provider/settings (refetch) S-->>Page: { dynamic_client_registration_enabled: true } Page-->>View: section shows the "Enabled" badge and a Disable button Note over Admin,View: Admin disables DCR Admin->>View: click "Disable" View->>Page: onDynamicClientRegistrationChange(false)<br/>(no dialog, disable is immediate) Page->>S: PUT ... {dynamic_client_registration_enabled: false} S-->>Page: 200 OK (audited) ``` ## Files changed All 10 files are hand-written; nothing in this PR is `make gen` output. | File | What changed | |---|---| | `site/src/api/api.ts` | New `getOAuth2ProviderSettings`/`putOAuth2ProviderSettings` methods, thin typed wrappers around the two endpoints #27316 added to `main`. | | `site/src/api/api.test.ts` | Covers both methods against the request they issue and the error they propagate. | | `site/src/api/queries/oauth2.ts` | A `getSettings` query and a `putSettings` mutation that invalidates the settings key on success. Both the app and settings keys now derive from a shared `oauth2ProviderKey` constant. | | `site/src/api/queries/oauth2.test.ts` | 4 tests: the key nesting, both delegations, and that a successful update invalidates the settings key without touching app queries. | | `.../OAuth2AppsSettingsPage.tsx` | Wires query and mutation into the page and passes the settings values down as one object, or omits it entirely without `viewDeploymentConfig`. The apps error stays its own prop, since the view gates the applications empty state on it. | | `.../OAuth2AppsSettingsPageView.tsx` | `Tabs` splitting Applications from Settings. The settings tab distinguishes loading, failed, and a value the server omitted rather than rendering nothing, and the header's "Add application" action is scoped to the applications tab. | | `.../OAuth2AppsSettingsPageView.stories.tsx` | 14 stories, covering the tab wiring, both permission boundaries, the header action's scope, and the settings tab's loading, fetch-error, update-error, and value-omitted states. | | `.../DynamicClientRegistrationSetting.tsx` | The section itself: heading, description including what disabling does not undo, `Enabled` badge, a permission explanation when the viewer cannot edit, and one button that confirms only in the enable direction. | | `.../DynamicClientRegistrationSetting.stories.tsx` | 11 stories, including focus surviving an in-flight request and the dialog ignoring a value that changes underneath it. | | `docs/admin/integrations/oauth2-provider.md` | Adds the web UI route to the DCR section, which previously enumerated only the CLI and the management API. | ## Suggested review order Follows the direction data actually flows, from the raw HTTP call up to the rendered section. 1. **`site/src/api/api.ts`**: the two new methods. Confirms they match the `codersdk.OAuth2ProviderSettings` shape #27316 landed and sit next to the existing OAuth2 app methods they mirror. 2. **`site/src/api/queries/oauth2.ts`**: the query/mutation pair. The mutation's `onSuccess` → `invalidateQueries` is the one detail worth double-checking: it's what makes the on-screen state catch up with what was just saved, rather than trusting the PUT payload. 3. **`OAuth2AppsSettingsPage.tsx`**: the container. Check the two separate permission gates (`viewDeploymentConfig` on the query's `enabled` option, `editDeploymentConfig` on the button's editability) match the RBAC the backend enforces. 4. **`OAuth2AppsSettingsPageView.tsx`**: the tabs and the settings tab's four states. The `settings` prop being optional is what hides the tab; the error inside the tab is deliberately separate from the page-level `error`, which gates the applications empty state. 5. **`DynamicClientRegistrationSetting.tsx`**: the section. Two things worth reading closely: the enable path opens the dialog while the disable path calls straight through, and lacking permission uses the native `disabled` attribute while an in-flight request uses `aria-disabled`, so a keyboard user is not blurred mid-flip. 6. **The two story files**: read last, as they exercise everything above without a real server. The dialog stories query `canvasElement.ownerDocument.body` rather than `canvasElement`, since the dialog renders into a portal attached to `<body>`. ## Deliberately not in this PR - **ENG-3116**: the applications list cannot distinguish self-registered clients from admin-created ones. Surfacing that needs a new field on `codersdk.OAuth2ProviderApp`, which is an API addition this PR does not need. - **ENG-3118**: reusing the shared `EnabledBadge` and `SettingsHeader` primitives for this section. Both hinge on what the mockup intends, and the badge in particular is a visible change either here or on the four other pages that share it. ## Screenshots Default (disabled): <img width="1676" height="497" alt="image" src="https://github.com/user-attachments/assets/cfa60266-8678-410e-9577-16ef474491e3" /> Enabling (confirmation dialog): <img width="1661" height="558" alt="image" src="https://github.com/user-attachments/assets/a7d54fdd-f65d-4fec-9ed9-3bfdcfdae5be" /> Enabled: <img width="1666" height="559" alt="image" src="https://github.com/user-attachments/assets/d39251c2-771c-4608-81c2-dda151b35c3d" /> --------- Co-authored-by: Tracy Johnson <tracy@coder.com> |
||
|
Jake Howell
|
497ab9e1a6 |
refactor(site): demui PortForwardButton and popover view (#27786)
Migrate the port-forward popover off MUI and Emotion onto shadcn Select/FormField and Tailwind. Replaces FormControl, Select, MenuItem, TextField, Stack, and Link usage in `PortForwardButton` / `PortForwardPopoverView`, and updates the popover stories to match. |
||
|
Jake Howell
|
0a30dc8184 |
refactor(site): demui template editor dialogs and create-template inputs (#27791)
Migrate remaining MUI usage in template create/editor flows to shared shadcn components (`FormField`, `Input`, `Textarea`, `Checkbox`, `RadioGroup`, `Link`). Also drops `disablePortal` on the publish-version help popover so it is no longer clipped by the dialog overflow. |
||
|
Jake Howell
|
20ff957c74 | refactor(site): demui workspace topbar, schedule controls, and timings (#27790) | ||
|
Ethan
|
4dbb3a236c |
test: fix tailnet connection teardown flake (#27768)
Closes https://github.com/coder/internal/issues/1620 Closes ENG-3043 The callback cleanup added in #20687 stops new node callbacks, but it can still race with one that's already in flight. That callback may call `UpdatePeers` after the destination `tailnet.Conn` closes, so the test fails with `connection closed` even though the redirect behaviour is correct. To fix, we'll just ignore `tailnet.ErrConnClosed` in the asynchronous `stitch` helpers, whilst continuing to assert on every other error. |
||
|
Marcin TojekandNick Vigilante
|
07073024ee |
docs: update 2.35 latest release to v2.35.3 (#27511)
Updates the release calendar in `docs/install/releases/index.md` so the 2.35 mainline row points at the latest patch release `v2.35.3` instead of `v2.35.2`. > [!NOTE] > This PR was generated by Coder Agents on behalf of @mtojek. --------- Co-authored-by: Nick Vigilante <nickvigilante@users.noreply.github.com> |
||
|
Jake Howell
|
fc27714fcd |
refactor(site): demui workspace build data and outdated tooltip (#27787)
Replace Emotion `css` / `useTheme` and MUI `Link` in `WorkspaceBuildData` and `WorkspaceOutdatedTooltip` with Tailwind semantic classes and the shared `Link` component. |
||
|
Nick Vigilante
|
0e1a9a9f05 |
ci: run test-go-pg mise tool install under bash on Windows (#27483)
## What Add `shell: bash` to the `Install Go mise tools` step in the `test-go-pg` job so it runs under Git bash on the `windows-2022` matrix leg. ## Why `test-go-pg (windows-2022)` has been failing in the **Normalize File and Directory Timestamps** step with: ``` mtimehash: command not found ##[error]Process completed with exit code 127. ``` before any tests run, which trips the aggregate `required` gate. Root cause: the `Install Go mise tools` step had no `shell:`, so on Windows it ran under **PowerShell**, while `./.github/scripts/retry.sh` is a bash script (`#!/usr/bin/env bash`). The step silently no-oped on Windows (zero output), so `mtimehash` was only present when the mise tool cache was warm. On a cache miss it was never installed, and the normalize step failed with exit 127. `main` stays green only because the cache is usually warm — both green and failing runs use the same `depot-windows-2022-16` runner, so this is **not** a fork/runner-routing issue. Pre-existing CI-tooling issue, unrelated to the change that surfaced it (a Helm-only community PR, #27360). ## Fix One line: pin the step to `shell: bash` so the install actually runs on Windows and repairs a cache miss instead of being silently skipped. ## Verification <details> <summary>Local proof that the step's install target builds and <code>mtimehash</code> runs under bash</summary> ``` $ bash ./.github/scripts/retry.sh --max-attempts 1 -- echo "retry.sh OK under bash" retry.sh OK under bash $ GOBIN=/tmp/demobin go install github.com/slsyy/mtimehash/cmd/mtimehash@v1.0.0 $ ls -l /tmp/demobin/mtimehash -rwxr-xr-x 1 coder coder 6692858 /tmp/demobin/mtimehash # the tool that was "command not found" now runs and rewrites the mtime: $ printf 'hello' > /tmp/mt.txt # mtime 2026-07-24 15:32 $ find /tmp/mt.txt | /tmp/demobin/mtimehash # exit 0 $ # mtime now 1997-11-30 (content-hash derived) ``` </details> Final confirmation is this PR's own `test-go-pg (windows-2022)` run. Note: if the mise cache is warm on this run the job passes regardless; the fix specifically hardens the cache-miss path this step exercises on Windows. ## Follow-up (not in this PR) - Make the normalize step resilient (skip when `mtimehash` is absent / invoke via `mise exec`) so a missing cache optimizer can't hard-fail the job. - Audit other Windows `run:` steps that invoke `retry.sh`/bash scripts without `shell: bash`. Linear: DOCS-605 > This PR was created with AI assistance (Coder Agents). |
||
|
Susana Ferreira
|
ec9b0f04d1 |
feat(site): label AI spend as estimated (#27584)
AI spend is estimated by multiplying token usage by a snapshot of published model prices that ships with each Coder release, so it can differ from provider invoices. Label spend figures as estimated and link to the [How spend is estimated](https://coder.com/docs/@main/ai-coder/ai-gateway/cost-controls#how-spend-is-estimated) docs section. "Estimated spend" matches the terminology already defined in the cost controls doc. ## Changes - Group members tooltip: "Monthly AI spend for this user." becomes "Estimated monthly AI spend for this user.", followed by an inline docs link. - Groups table tooltip: "Current AI spend compared to the group's AI budget..." becomes "Estimated AI spend compared to...", with the same link. - User dropdown: "(AI spend/month)" becomes "(Estimated AI spend/month)". - `StatusIconTooltip` now exports `SpendEstimateDocsLink`, shared by both tooltips. > [!NOTE] > Initially generated by Claude Opus 5, modified and reviewed by @ssncferreira |
||
|
Susana Ferreira
|
f4110122ec |
fix(site): link spend page alert to cost control migration section (#27782)
The "Read more here" link in the spend page alert pointed at the top of the cost controls doc, which doesn't explain the v2.36 move to AI Governance. Point it at the `#migrate-from-coder-agents-cost-control` section instead: https://coder.com/docs/@main/ai-coder/ai-gateway/cost-controls#migrate-from-coder-agents-cost-control Related to internal slack thread: https://codercom.slack.com/archives/C0AEHQGLW22/p1785747924721539 |
||
|
Sas SwartandClaude Opus 4.8
|
8886a5749a |
feat: add network calls list to AI session threads API (#27425)
The AI session threads API returned only a network call *summary* (total/blocked counts + top domains). This adds the per-call list so the session detail can render individual Agent Firewall network calls. `ListAIBridgeSessionNetworkCalls` reuses the same sequence-number windowing as the existing summary and includes all protocols. The list is exposed as `network_call_logs` on the threads response and is capped server-side at 100 rows. The summary (`network_calls.total`/`blocked`) remains authoritative for whole-session totals: the list length and its blocked count equal the summary only when a session has at most 100 calls, and are truncated beyond that. ### PR map (merge strictly bottom-up) This change is a 4-PR stack. Each PR depends on all the ones below it, so merge in this exact order: 1. #27417 — backend network summary 2. #27418 — frontend summary rows 3. #27425 — backend per-call list `network_call_logs` 4. #27426 — frontend network-calls panel Refs AIGOV-464 🤖 Generated with [Claude Code](https://claude.com/claude-code) --------- Co-authored-by: Claude Opus 4.8 (1M context) <noreply@anthropic.com> |
||
|
Jake Howell
|
fba9f0d485 |
refactor(site): migrate <Markdown /> and <InlineMarkdown /> off MUI (#27724)
Replace Emotion `css` / MUI theme tokens in `Markdown` with Tailwind semantic classes, and swap `InlineMarkdown`'s MUI `Link` for the shared `Link` component. Code block colors now use theme tokens (`surface-secondary`, `syntax-key`, `content-destructive`) instead of hardcoded zinc/teal and `theme.palette`. Also adds a `WithLink` story for the full Markdown component. |
||
|
Jake Howell
|
31ac9a4782 |
fix(site): use "Create token" wording in token settings (#27634)
> 🤖 This PR was written by Coder Agents on behalf of Jake Howell.

The token settings page button read **"Add token"**, while everything
else uses **"Create"**:

- The page the button navigates to is titled "Create Token" with a
"Create token" submit button (`CreateTokenPage` / `CreateTokenForm`).
- CLI: `coder tokens create`
- SDK: `CreateToken`
- API: `create-token-api-key` / `CreateTokenRequest`

This aligns the button with the dominant nomenclature by changing "Add
token" → "Create token".
|
||
|
Jake Howell
|
c350710aeb |
refactor(site): remove mui components from <LicenseSettingsPage /> descendants (#27764)
Migrate license settings views off MUI by replacing `TextField` with `Textarea` on the add-license form and `MuiLink` with our `Link` component in the empty licenses state. |
||
|
Jake Howell
|
a76c51dfc4 |
fix(site): correct autostop restart prompt on the workspace schedule page (#27632)
> 🤖 This PR was written by Coder Agents on behalf of Jake Howell. ## Problem Enabling autostop on a running workspace never showed the "restart now to apply?" dialog. The new TTL was saved, but a running build's deadline is only calculated when the build starts, so autostop silently did not take effect until a manual restart. Changing an already-enabled value did prompt, so the behavior was inconsistent. Separately, dismissing that dialog with **Apply later** navigated the user away to the workspace, exactly like confirming did. ## Root cause The dialog was gated on `getAutostop(workspace).autostopEnabled`, which derives from `workspace.ttl_ms` — the **pre-submit** state (the workspace is not refetched until after the mutation). That expression means "was autostop enabled *before* this change", which maps to: | Transition | Pre-submit enabled | Dialog | Correct? | |---|---|---|---| | Disabled → enabled (add) | `false` | not shown | ❌ the reported bug | | Enabled → new value (modify) | `true` | shown | ✅ | | Enabled → disabled (remove) | `true` | shown | ❌ (nothing to apply) | This guard came from #16085, which intended to *skip* the prompt when **removing** autostop (safe, because that PR also made the backend clear a running build's deadline server-side when TTL is set to null). By keying off the old state it actually skipped the prompt on **add** and still showed it on **remove** — the opposite of its intent. ## Fix - Key the prompt off the submitted form value (`values.autostopEnabled`), with an inline comment documenting the trigger conditions. This fixes the reported bug and restores #16085's intent: - add → prompt ✅ - modify → prompt ✅ - remove → no prompt ✅ (deadline cleared server-side) - stopped / unchanged → no prompt ✅ - **Apply later** now just closes the dialog and keeps the user on the schedule page; the saved value still applies on the next start. **Restart** is unchanged (restarts and navigates to the workspace). ## Testing Storybook `play`-function coverage on `WorkspaceSchedulePage` for all cases: enable, change value, disable, enable-while-stopped, autostart-only, and Apply-later-stays-on-page (the last also asserts `restartWorkspace` is not called). A prior story that asserted the pre-fix behavior (prompting on disable) was reworked. `tsc` and `biome` clean. <details> <summary>Investigation notes</summary> History of the gating condition: - Originally `if (data.autostopChanged) { ... }` — prompted on every autostop change (enable included). - #16085 ("allow removing deadline for running workspace", fixes #9775) added `&& getAutostop(workspace).autostopEnabled`. Its description states the goal was to "not show a confirmation dialog when the change is to remove autostop", and the same PR added backend logic in `putWorkspaceTTL` to clear a running build's deadline when TTL is null. - A later refactor added `&& workspace.latest_build.status === "running"`. Because the backend already clears the deadline live on removal, no restart is needed there; the frontend only needs to prompt when autostop ends up enabled on a running workspace. The fix keys off the submitted state so all three transitions behave correctly. </details> |
||
|
Jake Howell
|
0028fea0e5 |
refactor(site): migrate VS Code button menus off MUI (#27730)
Replace MUI `Menu`/`MenuItem` (and the Emotion `css` prop) in `VSCodeDesktopButton` and `VSCodeDevContainerButton` with the shared shadcn `DropdownMenu`. The variant selector keeps the split-button layout, sizes the menu to the button group via an `inline-flex` anchor (so width is not the full parent), and uses `collisionPadding` so the menu stays inset from the viewport edge. |
||
|
Jake Howell
|
5e29a878f2 |
refactor(site): demui <ProvisionerTagsField /> (#27763)
Replace MUI `TextField` in `ProvisionerTagsField` with the shared `Input` component. |
||
|
Jake Howell
|
ce20ad8b2f |
refactor(site): demui <NotificationEvents /> into dropdown (#27732)
> [!NOTE] > We don't have a planned migration path for the MUI `<ToggleGroup />`. Therefore, I've swapped these to dropdowns as an inbetween. Migrate deployment notification event settings off MUI `Card`/`List`/`ToggleButtonGroup` and Emotion styles. Template groups now use the same Tailwind card layout as user notification settings, and the delivery method control is a shared `Select` dropdown with icon + label. | Old | New | | --- | --- | | <img width="1041" height="189" alt="NOTIFICATION_EVENTS_OLD" src="https://github.com/user-attachments/assets/2fe37dab-1ba2-43c2-9d01-3edf9883054a" /> | <img width="1041" height="203" alt="NOTIFICATION_EVENTS_NEW" src="https://github.com/user-attachments/assets/40afc42f-93f6-4972-8e02-dceaf95fb034" /> | |
||
|
Jake Howell
|
26bae42c98 |
refactor(site): rename <404Page /> to <NotFoundPage /> (#27731)
The component was already named `NotFoundPage`, but it lived under `pages/404Page/404Page.tsx`. Rename the directory and file to match the component name, and update the lazy import and organization settings import paths. |
||
|
Jake Howell
|
0a42334f77 |
refactor(site): demui Form.stories.tsx stories (#27762)
Replace MUI `TextField` in the Form Storybook stories with `FormField`, wired through Formik and `getFormHelpers` so the examples match how real forms use the layout components. |
||
|
dependabot[bot]
|
b05a499a36 |
chore: bump autoprefixer from 10.5.0 to 10.5.4 in /site (#27755)
Bumps [autoprefixer](https://github.com/postcss/autoprefixer) from 10.5.0 to 10.5.4. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/postcss/autoprefixer/releases">autoprefixer's releases</a>.</em></p> <blockquote> <h2>10.5.4</h2> <ul> <li>Fixed prefixed rule duplication (by <a href="https://github.com/xianjianlf2"><code>@xianjianlf2</code></a>).</li> </ul> <h2>10.5.3</h2> <ul> <li>Fixed brackets and gradient parser (<a href="https://github.com/alanturing881"><code>@alanturing881</code></a>).</li> </ul> <h2>10.5.2</h2> <ul> <li>Moved <code>-webkit-fill-available</code> before <code>-moz-available</code>, so Firefox will use <code>-webkit-</code> version which is closer to <code>stretch</code>.</li> </ul> <h2>10.5.1</h2> <ul> <li>Fixed <code>grid-area</code> span reset for overriding areas (by <a href="https://github.com/puneetdixit200"><code>@puneetdixit200</code></a>).</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/postcss/autoprefixer/blob/main/CHANGELOG.md">autoprefixer's changelog</a>.</em></p> <blockquote> <h2>10.5.4</h2> <ul> <li>Fixed prefixed rule duplication (by <a href="https://github.com/xianjianlf2"><code>@xianjianlf2</code></a>).</li> </ul> <h2>10.5.3</h2> <ul> <li>Fixed brackets and gradient parser (<a href="https://github.com/alanturing881"><code>@alanturing881</code></a>).</li> </ul> <h2>10.5.2</h2> <ul> <li>Moved <code>-webkit-fill-available</code> before <code>-moz-available</code>, so Firefox will use <code>-webkit-</code> version which is closer to <code>stretch</code>.</li> </ul> <h2>10.5.1</h2> <ul> <li>Fixed <code>grid-area</code> span reset for overriding areas (by <a href="https://github.com/puneetdixit200"><code>@puneetdixit200</code></a>).</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/postcss/autoprefixer/commit/4cad00f0e839f3d7bbcdcc00b7df6fc448fb28f3"><code>4cad00f</code></a> Release 10.5.4 version</li> <li><a href="https://github.com/postcss/autoprefixer/commit/e62a4b1782f4ece51070feba79b0ff19f4305c68"><code>e62a4b1</code></a> Update CI config</li> <li><a href="https://github.com/postcss/autoprefixer/commit/c8f0d0ae00f5bb28bbcc3413f70b088020007469"><code>c8f0d0a</code></a> Update dependencies</li> <li><a href="https://github.com/postcss/autoprefixer/commit/cae35771dc4a4dfeda637a31dc1795ace6d9d28b"><code>cae3577</code></a> Move back to latest pnpm 11</li> <li><a href="https://github.com/postcss/autoprefixer/commit/fd31eb33b56ab9663d298b5bf08ae4ff47f76878"><code>fd31eb3</code></a> Fix duplicated prefixed selectors on reformatted CSS (<a href="https://redirect.github.com/postcss/autoprefixer/issues/1552">#1552</a>)</li> <li><a href="https://github.com/postcss/autoprefixer/commit/958d390787c31c3044c1fb68ec37efc29637e26b"><code>958d390</code></a> Release 10.5.3 version</li> <li><a href="https://github.com/postcss/autoprefixer/commit/21d2adb4d1fc6103c1e3cc39c991de59fdb5496e"><code>21d2adb</code></a> Fix gradient parser</li> <li><a href="https://github.com/postcss/autoprefixer/commit/f7ddae99f0ebfa3961a5c14bd9ecb7d4310601a6"><code>f7ddae9</code></a> Fix bracket parser</li> <li><a href="https://github.com/postcss/autoprefixer/commit/10ea5e7b8511a3e07aeb8a0f50f61496bc3faf4f"><code>10ea5e7</code></a> Update dependencies and remove patch</li> <li><a href="https://github.com/postcss/autoprefixer/commit/b6e8a2a4672cafafcb3bb2c72cd0027a31b1a320"><code>b6e8a2a</code></a> Update Dev Container</li> <li>Additional commits viewable in <a href="https://github.com/postcss/autoprefixer/compare/10.5.0...10.5.4">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for autoprefixer since your current version.</p> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
4fc605abe6 |
chore: bump motion from 12.40.0 to 12.42.2 in /site (#27748)
Bumps [motion](https://github.com/motiondivision/motion) from 12.40.0 to 12.42.2. <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/motiondivision/motion/blob/main/CHANGELOG.md">motion's changelog</a>.</em></p> <blockquote> <h2>[12.42.2] 2026-07-01</h2> <h3>Fixed</h3> <ul> <li><code>animateView</code>: Cropped group layers now animate <code>border-radius</code> from the old to new radius.</li> </ul> <h2>[12.42.1] 2026-06-30</h2> <h3>Fixed</h3> <ul> <li><code>animateView</code>: Old layer fade out now cancelled when defining <code>.new()</code>.</li> </ul> <h2>[12.42.0] 2026-06-24</h2> <h3>Changed</h3> <ul> <li><code>animateView</code>: Layers are automatically grouped to match their DOM-hierarchy. New <code>.group(false)</code> method opts-out.</li> </ul> <h3>Fixed</h3> <ul> <li><code>animateView</code>: Auto-crop is now aspect-ratio aware, disabling crops for matching aspect-ratios.</li> <li><code>animateView</code>: Disabled automatic <code>border-radius</code> animation.</li> </ul> <h2>[12.41.0] 2026-06-23</h2> <h3>Added</h3> <ul> <li><code>animateView</code>: Moves from Motion+ Early Access and alpha to main library.</li> <li><code>animateView</code>: <code>.add()</code> resolves a CSS selector or <code>Element</code> to automatically generate, apply and remove <code>view-transition-name</code>.</li> <li><code>animateView</code>: <code>.new()</code> and <code>.old()</code> configures values to animate on new and old layers.</li> <li><code>animateView</code>: <code>.layout()</code> can set a custom transition on the size/position animation of the currently selected elements.</li> <li><code>animateView</code>: Group layers now automatically crop with children set to <code>cover</code>, with <code>border-radius</code> animating from old radius to new. <code>.crop(false)</code> disables this behaviour.</li> <li><code>animateView</code>: <code>.class(name)</code> tags currently selected elements with a <code>view-transition-class</code> as a custom CSS hook.</li> </ul> <h3>Fixed</h3> <ul> <li><code>AnimatePresence</code>: Prevent stuck exit animations when children interrupt.</li> <li><code>drag</code>: Child <code>e.stopPropagation()</code> no longer break drag end.</li> <li>Fixing Next.js OOM on Windows when importing via <code>motion</code> package.</li> <li><code>animateLayout</code>: Improve handling of parallel/interleaved calls.</li> </ul> <h3>Changed</h3> <ul> <li><code>animateView</code>: <code>.enter()</code> and <code>.exit()</code> now refer specifically to <code>new</code> and <code>old</code> layers where there are no matching <code>old</code> or <code>new</code> layers.</li> <li><code>animateView</code>: Interrupted transition setups now return resolved animation rather than throwing.</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/motiondivision/motion/commit/40e8756c63b258c9dd07de9501cb788410eefb02"><code>40e8756</code></a> v12.42.2</li> <li><a href="https://github.com/motiondivision/motion/commit/718ccc7d4e8d17dddb36e73198b730fac57267c4"><code>718ccc7</code></a> Merge pull request <a href="https://redirect.github.com/motiondivision/motion/issues/3768">#3768</a> from motiondivision/view-cropped-corner-radius</li> <li><a href="https://github.com/motiondivision/motion/commit/19195a4bfc77389afb9cfd06bb2fb9eaeb798e8f"><code>19195a4</code></a> Dedupe corner-radius longhands; merge crop box/radii measurements</li> <li><a href="https://github.com/motiondivision/motion/commit/5299aa65a2428c55728d28b68c0d3242052d8b7a"><code>5299aa6</code></a> Resolve cropped-clip radius timing once; fix transition-option leak</li> <li><a href="https://github.com/motiondivision/motion/commit/937cdf396c29fa2826ba0836c1e6f1a1466e5064"><code>937cdf3</code></a> Animate cropped view-transition group corner radius</li> <li><a href="https://github.com/motiondivision/motion/commit/fd2d6f66d1cffcfeb2e2e0d9e39dc54796025db2"><code>fd2d6f6</code></a> v12.42.1</li> <li><a href="https://github.com/motiondivision/motion/commit/2223d873d8c78bab03301e5d9e3272c6d76907e6"><code>2223d87</code></a> Hold the old layer when only a non-opacity .new() is set</li> <li><a href="https://github.com/motiondivision/motion/commit/9c841455973b280c7989befd6dc918da0246a7fa"><code>9c84145</code></a> v12.42.0</li> <li><a href="https://github.com/motiondivision/motion/commit/60d7c72bc3d8052e2453424542d102467f3ed2fc"><code>60d7c72</code></a> Add view-transition group nesting and aspect-aware cropping</li> <li><a href="https://github.com/motiondivision/motion/commit/6437276caa543467a3bc407514ad0a4f842c37e0"><code>6437276</code></a> Updating</li> <li>Additional commits viewable in <a href="https://github.com/motiondivision/motion/compare/v12.40.0...v12.42.2">compare view</a></li> </ul> </details> <br /> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
6abd926807 |
chore: bump express from 4.21.2 to 4.22.2 in /site (#27752)
Bumps [express](https://github.com/expressjs/express) from 4.21.2 to 4.22.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/expressjs/express/releases">express's releases</a>.</em></p> <blockquote> <h2>v4.22.2</h2> <h2>What's Changed</h2> <ul> <li>fix: restore >20 array parsing for <code>req.query</code> repeated keys (<a href="https://github.com/expressjs/express/commit/8d09bfe6d88983da5c3e12cfdd54782c4dc675db"><code>8d09bfe6</code></a>) <ul> <li>This also unifies array-cap behavior across notations. Indexed notation (<code>a[0]=...</code>) was historically capped at qs's default <code>arrayLimit</code> of 20 even in older qs versions; after this change it also allows up to 1000 items.</li> </ul> </li> <li>deps: qs@~6.15.1</li> <li>deps: body-parser@~1.20.5</li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/suuuuuuminnnnnn"><code>@suuuuuuminnnnnn</code></a> made their first contribution in <a href="https://redirect.github.com/expressjs/express/pull/7021">expressjs/express#7021</a></li> <li><a href="https://github.com/SAY-5"><code>@SAY-5</code></a> made their first contribution in <a href="https://redirect.github.com/expressjs/express/pull/7181">expressjs/express#7181</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/express/compare/v4.22.1...v4.22.2">https://github.com/expressjs/express/compare/v4.22.1...v4.22.2</a></p> <h2>v4.22.1</h2> <h2>What's Changed</h2> <blockquote> <p>[!IMPORTANT]<br /> The prior release (4.22.0) included an erroneous breaking change related to the extended query parser. There is no actual security vulnerability associated with this behavior (CVE-2024-51999 has been rejected). The change has been fully reverted in this release.</p> </blockquote> <ul> <li>Release: 4.22.1 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6934">expressjs/express#6934</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/express/compare/4.22.0...v4.22.1">https://github.com/expressjs/express/compare/4.22.0...v4.22.1</a></p> <h2>4.22.0</h2> <h2>Important: Security</h2> <ul> <li>Security fix for <a href="https://www.cve.org/CVERecord?id=CVE-2024-51999">CVE-2024-51999</a> (<a href="https://github.com/expressjs/express/security/advisories/GHSA-pj86-cfqh-vqx6">GHSA-pj86-cfqh-vqx6</a>)</li> </ul> <h2>What's Changed</h2> <ul> <li>Refactor: improve readability by <a href="https://github.com/sazk07"><code>@sazk07</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6190">expressjs/express#6190</a></li> <li>ci: add support for Node.js@23.0 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6080">expressjs/express#6080</a></li> <li>Method functions with no path should error by <a href="https://github.com/wesleytodd"><code>@wesleytodd</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/5957">expressjs/express#5957</a></li> <li>ci: updated github actions ci workflow by <a href="https://github.com/Phillip9587"><code>@Phillip9587</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6323">expressjs/express#6323</a></li> <li>ci: reorder <code>npm i</code> steps to fix ci for older node versions by <a href="https://github.com/Phillip9587"><code>@Phillip9587</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6336">expressjs/express#6336</a></li> <li>Backport: ci: add node.js 24 to test matrix by <a href="https://github.com/Phillip9587"><code>@Phillip9587</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6506">expressjs/express#6506</a></li> <li>chore(4.x): wider range for query test skip by <a href="https://github.com/jonchurch"><code>@jonchurch</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6513">expressjs/express#6513</a></li> <li>use tilde notation for certain dependencies by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6905">expressjs/express#6905</a></li> <li>deps: qs@6.14.0 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6909">expressjs/express#6909</a></li> <li>deps: use tilde notation for <code>qs</code> by <a href="https://github.com/Phillip9587"><code>@Phillip9587</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6919">expressjs/express#6919</a></li> <li>Release: 4.22.0 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/express/pull/6921">expressjs/express#6921</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/express/compare/4.21.2...4.22.0">https://github.com/expressjs/express/compare/4.21.2...4.22.0</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/expressjs/express/blob/v4.22.2/History.md">express's changelog</a>.</em></p> <blockquote> <h1>4.22.2 / 2026-05-011</h1> <ul> <li>fix: restore >20 array parsing for <code>req.query</code> repeated keys (<a href="https://github.com/expressjs/express/commit/8d09bfe6d88983da5c3e12cfdd54782c4dc675db"><code>8d09bfe6</code></a>) <ul> <li>This also unifies array-cap behavior across notations. Indexed notation (<code>a[0]=...</code>) was historically capped at qs's default <code>arrayLimit</code> of 20 even in older qs versions; after this change it also allows up to 1000 items.</li> </ul> </li> <li>deps: qs@~6.15.1</li> <li>deps: body-parser@~1.20.5</li> </ul> <h1>4.22.1 / 2025-12-01</h1> <ul> <li>Revert security fix for <a href="https://www.cve.org/CVERecord?id=CVE-2024-51999">CVE-2024-51999</a> (<a href="https://github.com/expressjs/express/security/advisories/GHSA-pj86-cfqh-vqx6">GHSA-pj86-cfqh-vqx6</a>) <ul> <li>The prior release (4.22.0) included an erroneous breaking change related to the extended query parser. There is no actual security vulnerability associated with this behavior (CVE-2024-51999 has been rejected). The change has been fully reverted in this release.</li> </ul> </li> </ul> <h1>4.22.0 / 2025-12-01</h1> <ul> <li>Security fix for <a href="https://www.cve.org/CVERecord?id=CVE-2024-51999">CVE-2024-51999</a> (<a href="https://github.com/expressjs/express/security/advisories/GHSA-pj86-cfqh-vqx6">GHSA-pj86-cfqh-vqx6</a>)</li> <li>deps: use tilde notation for dependencies</li> <li>deps: qs@6.14.0</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/expressjs/express/commit/df0abc9333a3398b97b71f6ea7cd77d5ea3e9f97"><code>df0abc9</code></a> 4.22.2</li> <li><a href="https://github.com/expressjs/express/commit/836d36668ea750f78b4373b4de79bbd22634e6ec"><code>836d366</code></a> <code>4.x</code> update qs to 6.15.1, body-parser 1.20.5 (<a href="https://redirect.github.com/expressjs/express/issues/7224">#7224</a>)</li> <li><a href="https://github.com/expressjs/express/commit/8d09bfe6d88983da5c3e12cfdd54782c4dc675db"><code>8d09bfe</code></a> fix: restore array parsing for req.query repeated keys (<a href="https://redirect.github.com/expressjs/express/issues/7181">#7181</a>)</li> <li><a href="https://github.com/expressjs/express/commit/d39e8ad1778a0b8a606a5a7b17096d0cc5ec722d"><code>d39e8ad</code></a> deps: body-parser@~1.20.4 (<a href="https://redirect.github.com/expressjs/express/issues/7021">#7021</a>)</li> <li><a href="https://github.com/expressjs/express/commit/efe85d9fdc9e3a62f7a1121b4f5f484862298b48"><code>efe85d9</code></a> deps: qs@^6.14.1 (<a href="https://redirect.github.com/expressjs/express/issues/6972">#6972</a>)</li> <li><a href="https://github.com/expressjs/express/commit/f62378e1bc776259c0a471476c2dc043a02ac762"><code>f62378e</code></a> 📝 add note to history</li> <li><a href="https://github.com/expressjs/express/commit/12fae14531a78f19a2caaa5d4f58d9b01eaf3194"><code>12fae14</code></a> 4.22.1</li> <li><a href="https://github.com/expressjs/express/commit/5ddf311af32e772a77fd48b6266ce2f1ba330e1a"><code>5ddf311</code></a> Revert "sec: security patch for CVE-2024-51999"</li> <li><a href="https://github.com/expressjs/express/commit/49744abd1120484fe64d7bde1cd3197c32523b6e"><code>49744ab</code></a> 4.22.0 (<a href="https://redirect.github.com/expressjs/express/issues/6921">#6921</a>)</li> <li><a href="https://github.com/expressjs/express/commit/6e97452f600a3b01719fbc5517d833c7646b0bb7"><code>6e97452</code></a> sec: security patch for CVE-2024-51999</li> <li>Additional commits viewable in <a href="https://github.com/expressjs/express/compare/4.21.2...v4.22.2">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
025a3b253d |
chore: bump @lexical/utils from 0.44.0 to 0.48.0 in /site (#27751)
Bumps [@lexical/utils](https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils) from 0.44.0 to 0.48.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/facebook/lexical/releases">@lexical/utils's releases</a>.</em></p> <blockquote> <p>v0.48.0 is a maintenance release focused on bug fixes across Markdown, tables, lists, links, and selection. It's headlined by a fix for a v0.46.0 regression that broke native text drag-and-drop (<a href="https://redirect.github.com/facebook/lexical/pull/8842">#8842</a>) and a couple of notable security hardening fixes. It also adds a handful of new features, including an <code>MdastHtmlExtension</code> with examples for authoring custom Markdown constructs (collapsibles, <code>kbd</code>, alerts, footnotes), a customizable Yjs shared-type root name for collaborative editing, and new table row manipulation helpers.</p> <h2>New APIs & Features</h2> <ul> <li><a href="https://lexical.dev/docs/api/modules/lexical_table"><code>@lexical/table</code></a> — Added <code>$moveTableRow</code> for reordering table rows, plus the previously missing <code>$unmergeCellNode</code> export (<a href="https://redirect.github.com/facebook/lexical/pull/8833">#8833</a>)</li> <li><a href="https://lexical.dev/docs/api/modules/lexical_yjs"><code>@lexical/yjs</code></a> / <a href="https://lexical.dev/docs/api/modules/lexical_react"><code>@lexical/react</code></a> — The Yjs shared-type root name is now customizable, so Lexical can share a Yjs document with other content that uses a different root key (<a href="https://redirect.github.com/facebook/lexical/pull/8841">#8841</a>)</li> <li><a href="https://lexical.dev/docs/api/modules/lexical_extension"><code>@lexical/extension</code></a> / <a href="https://lexical.dev/docs/api/modules/lexical_mdast"><code>@lexical/mdast</code></a> — Added <code>MdastHtmlExtension</code> and Markdown custom-construct examples (collapsible sections, <code>kbd</code>, alerts, footnotes) demonstrating how to extend the Markdown ↔ mdast pipeline. See the <a href="https://lexical.dev/docs/serialization/markdown-mdast">Markdown & mdast serialization guide</a> (<a href="https://redirect.github.com/facebook/lexical/pull/8826">#8826</a>)</li> </ul> <h2>Notable Fixes</h2> <p><strong>Drag & drop (fix for v0.46.0 regression)</strong></p> <ul> <li>Don't cancel <code>dragover</code> for text drags, so native drops work again (<a href="https://redirect.github.com/facebook/lexical/pull/8842">#8842</a>)</li> </ul> <p><strong>Security</strong></p> <ul> <li><code>LinkNode.sanitizeUrl()</code> now fails closed on unparseable URLs, preventing a potential XSS vector (<a href="https://redirect.github.com/facebook/lexical/pull/8846">#8846</a>)</li> <li>Fixed a <code>serialize-javascript</code> dependency vulnerability (<a href="https://redirect.github.com/facebook/lexical/pull/8803">#8803</a>)</li> </ul> <p><strong>Markdown & code</strong></p> <ul> <li>Roundtrip overlapping inline formats correctly through mdast/Markdown (<a href="https://redirect.github.com/facebook/lexical/pull/8825">#8825</a>)</li> <li>Force re-tokenization after an async language load so highlighting appears once the grammar is ready (<a href="https://redirect.github.com/facebook/lexical/pull/8830">#8830</a>)</li> </ul> <p><strong>Tables</strong></p> <ul> <li>Auto-scroll while drag-selecting cells past the visible edge (<a href="https://redirect.github.com/facebook/lexical/pull/8822">#8822</a>)</li> <li>Enable table copy in read-only mode (<a href="https://redirect.github.com/facebook/lexical/pull/8845">#8845</a>)</li> </ul> <p><strong>Lists & character limit</strong></p> <ul> <li>Backspace at the start of a list item now outdents or converts to a paragraph (<a href="https://redirect.github.com/facebook/lexical/pull/8829">#8829</a>)</li> <li>Merge adjacent <code>OverflowNode</code>s in <code>useCharacterLimit</code> (<a href="https://redirect.github.com/facebook/lexical/pull/8831">#8831</a>)</li> <li>Count block separators when wrapping character-limit overflow (<a href="https://redirect.github.com/facebook/lexical/pull/8840">#8840</a>)</li> </ul> <p><strong>Links & selection</strong></p> <ul> <li>Disable link opening for disabled autolinks (<a href="https://redirect.github.com/facebook/lexical/pull/8839">#8839</a>)</li> <li>Skip <code>scrollIntoViewIfNeeded</code> when the selection rect is above the editor, fixing a Safari RTL caret jump (<a href="https://redirect.github.com/facebook/lexical/pull/8848">#8848</a>)</li> </ul> <h2>What's Changed</h2> <ul> <li>[lexical-mdast][lexical-markdown] Bug Fix: Roundtrip overlapping inline formats by <a href="https://github.com/etrepum"><code>@etrepum</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8825">facebook/lexical#8825</a></li> <li>[lexical-table][lexical-playground] Bug Fix: Auto-scroll while drag-selecting cells past the visible edge by <a href="https://github.com/JohnJunior"><code>@JohnJunior</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8822">facebook/lexical#8822</a></li> <li>[lexical-code-shiki] Bug Fix: force re-tokenize after async language load by <a href="https://github.com/ochevallier"><code>@ochevallier</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8830">facebook/lexical#8830</a></li> <li>[lexical-react] Bug Fix: Merge adjacent OverflowNodes in useCharacterLimit by <a href="https://github.com/mayrang"><code>@mayrang</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8831">facebook/lexical#8831</a></li> <li>Open playground links in a new tab by <a href="https://github.com/potatowagon"><code>@potatowagon</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8837">facebook/lexical#8837</a></li> <li>[lexical-rich-text][lexical-plain-text] Bug Fix: don't cancel dragover for text drags so native drops work again by <a href="https://github.com/etrepum"><code>@etrepum</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8842">facebook/lexical#8842</a></li> <li>[lexical-link] Bug Fix: disable link opening for disabled autolink in… by <a href="https://github.com/ochevallier"><code>@ochevallier</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8839">facebook/lexical#8839</a></li> <li>[lexical-table] Feature: Add $moveTableRow function & Add missing export for $unmergeCellNode by <a href="https://github.com/hamo-o"><code>@hamo-o</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8833">facebook/lexical#8833</a></li> <li>[lexical-list] Bug Fix: Backspace at start of list item outdents or converts to paragraph by <a href="https://github.com/mayrang"><code>@mayrang</code></a> in <a href="https://redirect.github.com/facebook/lexical/pull/8829">facebook/lexical#8829</a></li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/facebook/lexical/blob/main/CHANGELOG.md">@lexical/utils's changelog</a>.</em></p> <blockquote> <h2>v0.48.0 (2026-07-16)</h2> <ul> <li>lexical-reactlexical-table Bug Fix Enable table copy in read-only mode (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8845">#8845</a>) mayrang</li> <li>lexical-extensionlexical-mdastdev-mdast-editor-example Feature Add MdastHtmlExtension and Markdown custom-construct examples (collapsible, kbd, alerts, footnotes) (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8826">#8826</a>) Bob Ippolito</li> <li>Fix fail closed in LinkNode.sanitizeUrl() on unparseable URLs (XSS) (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8846">#8846</a>) xiezhenjia-meta</li> <li>lexical Chore Fix serialize-javascript package dependency vulnerability (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8803">#8803</a>) vijay ojha</li> <li>lexical-react Bug Fix Count block separators in character limit overflow wrapping (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8840">#8840</a>) mayrang</li> <li>lexical-yjslexical-react Feature Customizable Yjs shared-type root name (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8841">#8841</a>) mayrang</li> <li>lexical-list Bug Fix Backspace at start of list item outdents or converts to paragraph (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8829">#8829</a>) mayrang</li> <li>lexical-table Feature Add moveTableRow function Add missing export for unmergeCellNode (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8833">#8833</a>)</li> <li>lexical-link Bug Fix disable link opening for disabled autolink in (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8839">#8839</a>) Olivier Chevallier</li> <li>lexical-rich-textlexical-plain-text Bug Fix dont cancel dragover for text drags so native drops work again (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8842">#8842</a>) Bob Ippolito</li> <li>Open playground links in a new tab (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8837">#8837</a>) Sherry</li> <li>lexical-react Bug Fix Merge adjacent OverflowNodes in useCharacterLimit (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8831">#8831</a>) mayrang</li> <li>lexical-code-shiki Bug Fix force re-tokenize after async language load (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8830">#8830</a>) Olivier Chevallier</li> <li>lexical-tablelexical-playground Bug Fix Auto-scroll while drag-selecting cells past the visible edge (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8822">#8822</a>) Oleksandr Trukhnii</li> <li>lexical-mdastlexical-markdown Bug Fix Roundtrip overlapping inline formats (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8825">#8825</a>) Bob Ippolito</li> <li>v0.47.0 (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8821">#8821</a>) Bob Ippolito</li> <li>v0.47.0 Lexical GitHub Actions Bot</li> </ul> <h2>v0.47.0 (2026-07-10)</h2> <ul> <li>lexicallexical-rich-text Bug Fix Fix formatText toggle direction and add SETTEXTFORMATCOMMAND (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8807">#8807</a>) mayrang</li> <li>scripts Bug Fix Let npm prompt for OTP when publishing bootstrap stubs (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8820">#8820</a>) Bob Ippolito</li> <li>lexical-playground Bug Fix Clear inline font-size when converting to heading (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8800">#8800</a>) mayrang</li> <li>lexical-tablelexical-playground Feature setTableRowIsHeader and setTableColumnIsHeader utilities (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8815">#8815</a>) mayrang</li> <li>lexical-website Documentation Update Rewrite testing guide (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8811">#8811</a>) mayrang</li> <li>lexical-mdastlexical-rich-text Feature lexicalmdast, a micromarkmdast-based alternative to lexicalmarkdown (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8794">#8794</a>) Bob Ippolito</li> <li>Make dependency-check resilient to transient registry errors (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8818">#8818</a>) Gerard Rovira</li> <li>lexical Refactor Move event module globals into per-editor InputState (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8809">#8809</a>) mayrang</li> <li>lexical Bug Fix getDocument() should fall back to the global document when there is no active editor (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8813">#8813</a>) Sherry</li> <li>lexical-playground Bug Fix Keep cell background color modal open on first click (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8806">#8806</a>) sahir</li> <li>lexical-playground Bug Fix Use consistent default maxWidth for markdown-imported images (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8810">#8810</a>) mayrang</li> <li>lexical-devtoolslexical-playground Chore Update flow, hermes, and babel packages to latest (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8795">#8795</a>) Bob Ippolito</li> <li>Add a 7-day pnpm minimumReleaseAge to match the Dependabot cooldown (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8808">#8808</a>) Gerard Rovira</li> <li>lexical Chore Fix tmp package dependency vulnerability (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8802">#8802</a>) vijay ojha</li> <li>lexical Chore Add missing Flow type declarations (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8799">#8799</a>) mayrang</li> <li>lexical-markdown Feature Add generateNodesFromMarkdownString (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8789">#8789</a>) mayrang</li> <li>lexicallexical-playground Chore Refactor IME composition test infrastructure and add browser-level coverage (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8793">#8793</a>) mayrang</li> <li>lexical-playground Bug Fix Use viewBox dimensions for unsized Excalidraw output (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8798">#8798</a>) mayrang</li> <li>lexical-table Bug Fix Export insertTableRowAtNode and insertTableColumnAtNode (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8791">#8791</a>)</li> <li>lexical-playgroundlexical-website Feature Add Vercel Analytics and Speed Insights (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8796">#8796</a>) Gerard Rovira</li> <li>lexicallexical-eslint-plugin Feature Add getDocument() API and Shadow DOM lint enforcement (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8788">#8788</a>) mayrang</li> <li>scripts Bug Fix strip misplaced pure annotations from prod builds (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8786">#8786</a>) Bob Ippolito</li> <li>lexical Bug Fix deleteCharacter overwrites X11 PRIMARY selection via Selection.modify (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8774">#8774</a>) Bob Ippolito</li> <li>lexical-playground Bug Fix Support Unicode URLs in autolink matcher (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8787">#8787</a>) mayrang</li> <li>lexical-table Feature Spread pasted TSV text across table cells (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8780">#8780</a>) mayrang</li> <li>Breaking Changelexical Bug Fix Preserve DOM element when composing on segmented TextNode middle (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8784">#8784</a>) mayrang</li> <li>Breaking Changelexical-reactlexical-devtools-core Chore Drop React 17 support, baseline is now React 18 (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8782">#8782</a>) Bob Ippolito</li> <li>lexical-playgroundlexical Feature Ruby annotation node with floating editor (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8741">#8741</a>) mayrang</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/facebook/lexical/commit/284b7491d014c412a11ecc8e4b8ea8e09e07f7e9"><code>284b749</code></a> v0.48.0</li> <li><a href="https://github.com/facebook/lexical/commit/e4b7cc3f420226059c8aa30df6e89bd5fadbea90"><code>e4b7cc3</code></a> v0.47.0 (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8821">#8821</a>)</li> <li><a href="https://github.com/facebook/lexical/commit/a7666ab11f5e8c674a3f5ca8a83d2e92f1b171d0"><code>a7666ab</code></a> [*][lexical-devtools][lexical-playground] Chore: Update flow, hermes, and bab...</li> <li><a href="https://github.com/facebook/lexical/commit/e649ab28b7e2dd58c1b4798c446e611f54356518"><code>e649ab2</code></a> [lexical][lexical-eslint-plugin] Feature: Add $getDocument() API and Shadow D...</li> <li><a href="https://github.com/facebook/lexical/commit/62a4b30f382b4dc60cacd1a9d753a2d1f44d9f5e"><code>62a4b30</code></a> [lexical][*] Feature: registerEventListener / registerEventListeners DOM help...</li> <li><a href="https://github.com/facebook/lexical/commit/cf25494881c9c04b090f6681d7b603ec31e157ff"><code>cf25494</code></a> [lexical-utils] Bug Fix: positionNodeOnRange leaking orphan rect nodes when r...</li> <li><a href="https://github.com/facebook/lexical/commit/1803c54f0e9cffad42a145e3bcaaf5051fe7fdee"><code>1803c54</code></a> [lexical-selection] Bug Fix: Properly handle block end focus in backward sele...</li> <li><a href="https://github.com/facebook/lexical/commit/fc162d45ae707869f47066f1aafc6fe47b1dfae1"><code>fc162d4</code></a> [lexical-extension][lexical-playground] Chore: Some cleanups (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8732">#8732</a>)</li> <li><a href="https://github.com/facebook/lexical/commit/041c8642c0c0f4d0b7e791f3c499dfeac50a4a9e"><code>041c864</code></a> v0.46.0 (<a href="https://github.com/facebook/lexical/tree/HEAD/packages/lexical-utils/issues/8748">#8748</a>)</li> <li><a href="https://github.com/facebook/lexical/commit/6352a9a7f99c33d10e8b2698738d3bb6c5b6fe51"><code>6352a9a</code></a> [lexical-utils][lexical-react] Chore: Move getScrollParent to <code>@lexical/utils</code> ...</li> <li>Additional commits viewable in <a href="https://github.com/facebook/lexical/commits/v0.48.0/packages/lexical-utils">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for <code>@lexical/utils</code> since your current version.</p> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
e63bbc8a32 |
chore: bump tailwindcss from 3.4.18 to 3.4.19 in /site (#27750)
Bumps [tailwindcss](https://github.com/tailwindlabs/tailwindcss/tree/HEAD/packages/tailwindcss) from 3.4.18 to 3.4.19. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/tailwindlabs/tailwindcss/releases">tailwindcss's releases</a>.</em></p> <blockquote> <h2>v3.4.19</h2> <h3>Fixed</h3> <ul> <li>Don’t break <code>sibling-*()</code> functions when used inside <code>calc(…)</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19335">#19335</a>)</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/tailwindlabs/tailwindcss/blob/main/CHANGELOG.md">tailwindcss's changelog</a>.</em></p> <blockquote> <h2>[3.4.19] - 2025-12-10</h2> <h3>Fixed</h3> <ul> <li>Don’t break <code>sibling-*()</code> functions when used inside <code>calc(…)</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19335">#19335</a>)</li> </ul> <h2>[4.1.17] - 2025-11-06</h2> <h3>Fixed</h3> <ul> <li>Substitute <code>@variant</code> inside legacy JS APIs (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19263">#19263</a>)</li> <li>Prevent occasional crash on Windows when loaded into a worker thread (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19242">#19242</a>)</li> </ul> <h2>[4.1.16] - 2025-10-23</h2> <h3>Fixed</h3> <ul> <li>Discard candidates with an empty data type (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19172">#19172</a>)</li> <li>Fix canonicalization of arbitrary variants with attribute selectors (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19176">#19176</a>)</li> <li>Fix invalid colors due to nested <code>&</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19184">#19184</a>)</li> <li>Improve canonicalization for <code>& > :pseudo</code> and <code>& :pseudo</code> arbitrary variants (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19178">#19178</a>)</li> </ul> <h2>[4.1.15] - 2025-10-20</h2> <h3>Fixed</h3> <ul> <li>Fix Safari devtools rendering issue due to <code>color-mix</code> fallback (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19069">#19069</a>)</li> <li>Suppress Lightning CSS warnings about <code>:deep</code>, <code>:slotted</code>, and <code>:global</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19094">#19094</a>)</li> <li>Fix resolving theme keys when starting with the name of another theme key in JS configs and plugins (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19097">#19097</a>)</li> <li>Allow named groups in combination with <code>not-*</code>, <code>has-*</code>, and <code>in-*</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19100">#19100</a>)</li> <li>Prevent important utilities from affecting other utilities (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19110">#19110</a>)</li> <li>Don’t index into strings with the <code>theme(…)</code> function (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19111">#19111</a>)</li> <li>Fix parsing issue when <code>\t</code> is used in at-rules (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19130">#19130</a>)</li> <li>Upgrade: Canonicalize utilities containing <code>0</code> values (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19095">#19095</a>)</li> <li>Upgrade: Migrate deprecated <code>break-words</code> to <code>wrap-break-word</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19157">#19157</a>)</li> </ul> <h3>Changed</h3> <ul> <li>Remove the <code>postinstall</code> script from oxide (<a href="https://github.com/tailwindlabs/tailwindcss/tree/HEAD/packages/tailwindcss/issues/19149">#19149</a>)(<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/19149">tailwindlabs/tailwindcss#19149</a>)</li> </ul> <h2>[4.1.14] - 2025-10-01</h2> <h3>Fixed</h3> <ul> <li>Handle <code>'</code> syntax in ClojureScript when extracting classes (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18888">#18888</a>)</li> <li>Handle <code>@variant</code> inside <code>@custom-variant</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18885">#18885</a>)</li> <li>Merge suggestions when using <code>@utility</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18900">#18900</a>)</li> <li>Ensure that file system watchers created when using the CLI are always cleaned up (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18905">#18905</a>)</li> <li>Do not generate <code>grid-column</code> utilities when configuring <code>grid-column-start</code> or <code>grid-column-end</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18907">#18907</a>)</li> <li>Do not generate <code>grid-row</code> utilities when configuring <code>grid-row-start</code> or <code>grid-row-end</code> (<a href="https://redirect.github.com/tailwindlabs/tailwindcss/pull/18907">#18907</a>)</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/tailwindlabs/tailwindcss/commits/v3.4.19/packages/tailwindcss">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
c3bd8bece4 |
chore: bump @fontsource-variable/geist from 5.2.9 to 5.3.0 in /site (#27749)
Bumps [@fontsource-variable/geist](https://github.com/fontsource/font-files/tree/HEAD/fonts/variable/geist) from 5.2.9 to 5.3.0. <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/fontsource/font-files/commits/HEAD/fonts/variable/geist">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
0b3212ddf2 |
chore: bump @fontsource/source-code-pro from 5.2.7 to 5.3.0 in /site (#27746)
Bumps [@fontsource/source-code-pro](https://github.com/fontsource/font-files/tree/HEAD/fonts/google/source-code-pro) from 5.2.7 to 5.3.0. <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/fontsource/font-files/commits/HEAD/fonts/google/source-code-pro">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
2cbb6629e4 |
chore: bump humanize-duration from 3.33.1 to 3.34.0 in /site (#27742)
Bumps [humanize-duration](https://github.com/EvanHahn/HumanizeDuration.js) from 3.33.1 to 3.34.0. <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/EvanHahn/HumanizeDuration.js/blob/main/HISTORY.md">humanize-duration's changelog</a>.</em></p> <blockquote> <h1>3.34.0 / 2026-06-29</h1> <ul> <li>new: Norwegian Nynorsk support (<code>nn</code>)</li> <li>fix: Lithuanian now uses the singular form for counts such as 101 and 201 (for example "101 diena" instead of "101 dienų")</li> </ul> <h1>3.33.2 / 2025-12-07</h1> <ul> <li>fix: Romanian now correctly uses "de" before nouns for numbers >= 20 such as "20 de minute" instead of "20 minute" (see <a href="https://redirect.github.com/EvanHahn/HumanizeDuration.js/pull/235">#235</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/49fa19c1e64833630f1f5a2b7ef5b5410933c372"><code>49fa19c</code></a> 3.34.0</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/47ab9424702dd10808d5b6292fdcf8dfd340103a"><code>47ab942</code></a> Update changelog and bower.json for 3.34.0 release</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/545a37b2d8318f6b21851cc886ff2edf7a79e3cf"><code>545a37b</code></a> Update devDependencies to latest versions</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/23607f9fa017638809dad87d9f6961f7d99d7487"><code>23607f9</code></a> Update TypeScript to latest (RC) version</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/0883f5dbf59c6d81aac57279e969d621dad6e31b"><code>0883f5d</code></a> Update changelog with Norwegian Nynorsk change</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/ffcfa2a482570db1ed4a967f2ed28259eb9bb0ea"><code>ffcfa2a</code></a> Update ESLint dependencies to latest version</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/c2791af9d6818242fa9dee636004dde2980b3033"><code>c2791af</code></a> Update Git URL</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/0f69e090fa5e702aaabab1df610db2302fa97359"><code>0f69e09</code></a> Fix Lithuanian form for counts like 101 and 201 (<a href="https://redirect.github.com/EvanHahn/HumanizeDuration.js/issues/237">#237</a>)</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/fd49da2861bfd3f76711e8b4b87977d699dee983"><code>fd49da2</code></a> Add Norwegian Nynorsk (nn) language</li> <li><a href="https://github.com/EvanHahn/HumanizeDuration.js/commit/b961e8cace217f77f4481981ec5108065f0de2af"><code>b961e8c</code></a> Mention <code>Intl.DurationFormat</code> in the readme</li> <li>Additional commits viewable in <a href="https://github.com/EvanHahn/HumanizeDuration.js/compare/v3.33.1...v3.34.0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
4c079ef689 |
chore: bump axios from 1.18.0 to 1.18.1 in /site (#27741)
Bumps [axios](https://github.com/axios/axios) from 1.18.0 to 1.18.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/axios/axios/releases">axios's releases</a>.</em></p> <blockquote> <h2>v1.18.1 — June 21, 2026</h2> <p>This release focuses on Node HTTP adapter fixes, safer AxiosError serialisation, runtime/type correctness fixes, documentation updates, and dependency maintenance.</p> <h2>🐛 Bug Fixes</h2> <ul> <li>AxiosError Serialisation: Made AxiosError#cause non-enumerable to prevent circular JSON serialisation failures when errors include nested causes. (<a href="https://redirect.github.com/axios/axios/issues/10913">#10913</a>)</li> <li>Node HTTP Adapter: Guarded socket.setKeepAlive for proxy agent streams, accepted path-only URLs when socketPath is configured, deferred environment proxy handling to Node, and explicitly passed maxBodyLength through to follow-redirects. (<a href="https://redirect.github.com/axios/axios/issues/10917">#10917</a>, <a href="https://redirect.github.com/axios/axios/issues/10930">#10930</a>, <a href="https://redirect.github.com/axios/axios/issues/10942">#10942</a>, <a href="https://redirect.github.com/axios/axios/issues/10993">#10993</a>)</li> <li>Runtime and Type Correctness: Fixed several runtime crashes, type definition mismatches, and incorrect error handling paths. (<a href="https://redirect.github.com/axios/axios/issues/10959">#10959</a>, <a href="https://redirect.github.com/axios/axios/issues/11021">#11021</a>)</li> <li>AxiosURLSearchParams: Switched the encoder callback to an arrow function so <code>encoder.call(this)</code> receives the <code>AxiosURLSearchParams</code> instance correctly. (<a href="https://redirect.github.com/axios/axios/issues/11019">#11019</a>)</li> </ul> <h2>🔧 Maintenance & Chores</h2> <ul> <li> <p>Documentation: Documented sensitive headers and status transition behaviour, prepared cleaned-up docs, added Deno install instructions, and clarified that request data is request-specific (<a href="https://redirect.github.com/axios/axios/issues/11007">#11007</a>, <a href="https://redirect.github.com/axios/axios/issues/11010">#11010</a>, <a href="https://redirect.github.com/axios/axios/issues/11023">#11023</a>, <a href="https://redirect.github.com/axios/axios/issues/11025">#11025</a>)</p> </li> <li> <p>Dependencies: Bumped vite, rollup, form-data, js-yaml, and multer across the root project, docs, smoke tests, and module test workspaces. (<a href="https://redirect.github.com/axios/axios/issues/11011">#11011</a>, <a href="https://redirect.github.com/axios/axios/issues/11012">#11012</a>, <a href="https://redirect.github.com/axios/axios/issues/11013">#11013</a>, <a href="https://redirect.github.com/axios/axios/issues/11014">#11014</a>, <a href="https://redirect.github.com/axios/axios/issues/11015">#11015</a>, <a href="https://redirect.github.com/axios/axios/issues/11016">#11016</a>, <a href="https://redirect.github.com/axios/axios/issues/11017">#11017</a>, <a href="https://redirect.github.com/axios/axios/issues/11026">#11026</a>)</p> </li> </ul> <h2>🌟 New Contributors</h2> <p>We are thrilled to welcome our new contributors. Thank you for helping improve axios:</p> <ul> <li><a href="https://github.com/webdevelopersrinu"><code>@webdevelopersrinu</code></a> (<a href="https://redirect.github.com/axios/axios/issues/10913">#10913</a>)</li> <li><a href="https://github.com/sijie-Z"><code>@sijie-Z</code></a> (<a href="https://redirect.github.com/axios/axios/issues/10993">#10993</a>)</li> <li><a href="https://github.com/bartlomieju"><code>@bartlomieju</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11023">#11023</a>)</li> <li><a href="https://github.com/JSap0914"><code>@JSap0914</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11019">#11019</a>)</li> </ul> <p><a href="https://github.com/axios/axios/compare/v1.18.0...v1.18.1">Full Changelog</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/axios/axios/blob/v1.x/CHANGELOG.md">axios's changelog</a>.</em></p> <blockquote> <h1>Changelog</h1> <h2>v1.19.0 — July 22, 2026</h2> <p>This release raises the form-data security floor, adds configuration and type-system capabilities, and fixes NO_PROXY matching, interceptor errors, progress reporting, and serialization edge cases.</p> <h2>🔒 Security Fixes</h2> <ul> <li>Multipart Form Data: Raised the form-data dependency floor to ^4.0.6, preventing fresh installations from resolving versions affected by the CRLF injection vulnerability GHSA-hmw2-7cc7-3qxx (<a href="https://github.com/advisories/GHSA-hmw2-7cc7-3qxx">https://github.com/advisories/GHSA-hmw2-7cc7-3qxx</a>). (<a href="https://redirect.github.com/axios/axios/issues/11028">#11028</a>)</li> </ul> <h2>🚀 New Features</h2> <ul> <li>Configuration Extensibility: Preserved own-enumerable symbol-keyed fields through mergeConfig and added a generic params type across public TypeScript declarations, responses, errors, adapters, and serializers. (<a href="https://redirect.github.com/axios/axios/issues/11043">#11043</a>, <a href="https://redirect.github.com/axios/axios/issues/11081">#11081</a>)</li> <li>Header Parameter Parsing: Added the opt-in AxiosHeaders.parseParameters() parser for quote-aware, RFC-style HTTP parameter parsing while preserving legacy parsing behavior. (<a href="https://redirect.github.com/axios/axios/issues/11051">#11051</a>)</li> <li>HTTP Status Codes: Added the missing Cloudflare 520 WebServerReturnsAnUnknownError status and matching ESM/CJS declarations. (<a href="https://redirect.github.com/axios/axios/issues/11067">#11067</a>)</li> </ul> <h2>🐛 Bug Fixes</h2> <ul> <li> <p>Form Data Conversion: Limited formDataToJSON path splitting to dot and bracket notation, preserving literal punctuation in keys, and removed browser-facing Buffer.from usage from toFormData to avoid unnecessary polyfills. (<a href="https://redirect.github.com/axios/axios/issues/11006">#11006</a>, <a href="https://redirect.github.com/axios/axios/issues/11018">#11018</a>)</p> </li> <li> <p>Proxy Bypass: Canonicalized IPv4 shorthand, octal, and hexadecimal forms during NO_PROXY matching and honored * entries within comma- or space-separated bypass lists. (<a href="https://redirect.github.com/axios/axios/issues/11029">#11029</a>, <a href="https://redirect.github.com/axios/axios/issues/11053">#11053</a>)</p> </li> <li> <p>Cancellation: Propagated already-aborted input signals immediately when composing abort signals. (<a href="https://redirect.github.com/axios/axios/issues/11035">#11035</a>)</p> </li> <li> <p>Header Handling: Preserved empty first values for duplicate singleton headers and made AxiosHeaders#getSetCookie() consistently return arrays for present values. (<a href="https://redirect.github.com/axios/axios/issues/11036">#11036</a>, <a href="https://redirect.github.com/axios/axios/issues/11037">#11037</a>)</p> </li> <li> <p>URL Handling: Included normalized, safely redacted offending URLs in malformed-protocol errors and removed repeated trailing slashes when combining base URLs. (<a href="https://redirect.github.com/axios/axios/issues/11008">#11008</a>, <a href="https://redirect.github.com/axios/axios/issues/11038">#11038</a>)</p> </li> <li> <p>Progress Events: Clamped malformed negative progress values to zero and ensured final Node.js download progress events are delivered before streamed responses close. (<a href="https://redirect.github.com/axios/axios/issues/11039">#11039</a>, <a href="https://redirect.github.com/axios/axios/issues/11040">#11040</a>)</p> </li> <li> <p>Error and JSON Serialization: Serialized Set values as arrays in JSON-compatible snapshots and synthesized useful AxiosError messages from otherwise-empty AggregateError instances. (<a href="https://redirect.github.com/axios/axios/issues/11044">#11044</a>, <a href="https://redirect.github.com/axios/axios/issues/11059">#11059</a>)</p> </li> <li> <p>Content-Length Enforcement: Corrected base64 data: URL size estimation so maxContentLength is enforced consistently by the HTTP and Fetch adapters. (<a href="https://redirect.github.com/axios/axios/issues/11061">#11061</a>)</p> </li> <li> <p>Synchronous Interceptors: Prevented requests from being dispatched after synchronous request interceptors fail unless their paired rejection handler resolves successfully. (<a href="https://redirect.github.com/axios/axios/issues/11071">#11071</a>)</p> </li> </ul> <h2>🔧 Maintenance & Chores</h2> <ul> <li>Dependencies: Updated development and test tooling, the docs fixture's Axios version, and GitHub Actions integrations including Checkout, Setup Node, Setup Deno, and Zizmor. (<a href="https://redirect.github.com/axios/axios/issues/11031">#11031</a>, <a href="https://redirect.github.com/axios/axios/issues/11055">#11055</a>, <a href="https://redirect.github.com/axios/axios/issues/11056">#11056</a>, <a href="https://redirect.github.com/axios/axios/issues/11058">#11058</a>, <a href="https://redirect.github.com/axios/axios/issues/11079">#11079</a>, <a href="https://redirect.github.com/axios/axios/issues/11080">#11080</a>, <a href="https://redirect.github.com/axios/axios/issues/11088">#11088</a>, <a href="https://redirect.github.com/axios/axios/issues/11089">#11089</a>, <a href="https://redirect.github.com/axios/axios/issues/11090">#11090</a>)</li> <li>Build Outputs: Limited sourcemap generation to published minified bundles, removing broken map references from non-minified builds. (<a href="https://redirect.github.com/axios/axios/issues/11054">#11054</a>)</li> <li>Form Data Internals: Centralized FormData header handling and made the Node.js adapter tolerate getHeaders() returning undefined under the content-only policy. (<a href="https://redirect.github.com/axios/axios/issues/11062">#11062</a>)</li> <li>Developer Experience: Ignored common local AI-tooling directories and fixed a constant-reassignment crash when the development sandbox serves its root path. (<a href="https://redirect.github.com/axios/axios/issues/11032">#11032</a>, <a href="https://redirect.github.com/axios/axios/issues/11073">#11073</a>)</li> <li>Documentation: Updated sponsor information, clarified that baseURL is not a path-security boundary, scoped provenance claims to attested releases, and corrected the configuration-defaults documentation. (<a href="https://redirect.github.com/axios/axios/issues/11041">#11041</a>, <a href="https://redirect.github.com/axios/axios/issues/11068">#11068</a>, <a href="https://redirect.github.com/axios/axios/issues/11076">#11076</a>, <a href="https://redirect.github.com/axios/axios/issues/11078">#11078</a>)</li> <li>Publishing: Simplified v1 publishing to use the npm version bundled with Node.js 26 and updated package metadata for the 1.19.0 release. (<a href="https://redirect.github.com/axios/axios/issues/11083">#11083</a>, <a href="https://redirect.github.com/axios/axios/issues/11095">#11095</a>)</li> </ul> <h2>🌟 New Contributors</h2> <p>We are thrilled to welcome our new contributors. Thank you for helping improve Axios:</p> <ul> <li><a href="https://github.com/afonsojramos"><code>@afonsojramos</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11028">#11028</a>)</li> <li><a href="https://github.com/MahinAnowar"><code>@MahinAnowar</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11006">#11006</a>)</li> <li><a href="https://github.com/yassertawfik4"><code>@yassertawfik4</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11024">#11024</a>)</li> <li><a href="https://github.com/AnandSundar"><code>@AnandSundar</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11029">#11029</a>)</li> <li><a href="https://github.com/lin-hongkuan"><code>@lin-hongkuan</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11035">#11035</a>)</li> <li><a href="https://github.com/Wali007-lab"><code>@Wali007-lab</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11054">#11054</a>)</li> <li><a href="https://github.com/magicdawn"><code>@magicdawn</code></a> (<a href="https://redirect.github.com/axios/axios/issues/11043">#11043</a>)</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/axios/axios/commit/a209bfb1e5dcbce3cecbf4bd955339d006358887"><code>a209bfb</code></a> chore(release): prepare release 1.18.1 (<a href="https://redirect.github.com/axios/axios/issues/11027">#11027</a>)</li> <li><a href="https://github.com/axios/axios/commit/fa6a55ef99235074d2c11d80a1064ef02850d598"><code>fa6a55e</code></a> chore(deps-dev): bump multer from 2.1.1 to 2.2.0 (<a href="https://redirect.github.com/axios/axios/issues/11026">#11026</a>)</li> <li><a href="https://github.com/axios/axios/commit/40e7be8a78dd43caaeb2313cc4be3f8e714be91d"><code>40e7be8</code></a> docs: clarifies that request data is request-specific in axios (<a href="https://redirect.github.com/axios/axios/issues/11025">#11025</a>)</li> <li><a href="https://github.com/axios/axios/commit/a446b39b19c8b570214a4158520c5ddd5b020366"><code>a446b39</code></a> fix(AxiosURLSearchParams): use arrow function so encoder.call(this) receives ...</li> <li><a href="https://github.com/axios/axios/commit/cf1306a42d97960b635c894c83658f2692e53585"><code>cf1306a</code></a> docs: add Deno to install instructions (<a href="https://redirect.github.com/axios/axios/issues/11023">#11023</a>)</li> <li><a href="https://github.com/axios/axios/commit/b32880af48017457a1203ab2e63720902d3b71b3"><code>b32880a</code></a> fix: incorrect use of error (<a href="https://redirect.github.com/axios/axios/issues/11021">#11021</a>)</li> <li><a href="https://github.com/axios/axios/commit/1792eda11aff8fe0f8c8a6e5ae6ff305740a6460"><code>1792eda</code></a> fix: ensure maxBodyLength is explicitly passed to follow-redirects (<a href="https://redirect.github.com/axios/axios/issues/10993">#10993</a>)</li> <li><a href="https://github.com/axios/axios/commit/30499d6af0961ec38619792013a534d1933b08a9"><code>30499d6</code></a> fix: various runtime crashes and type definition mismatches (<a href="https://redirect.github.com/axios/axios/issues/10959">#10959</a>)</li> <li><a href="https://github.com/axios/axios/commit/20ce9c412ebd88823d1a4a47000cb133a8f79440"><code>20ce9c4</code></a> fix(http): defer env proxy handling to Node (<a href="https://redirect.github.com/axios/axios/issues/10942">#10942</a>)</li> <li><a href="https://github.com/axios/axios/commit/e64bcf9c5af231d6f37d8389b1e57ded314fff86"><code>e64bcf9</code></a> chore(deps): merge branch 'v1.x' into tests/module/cjs (<a href="https://redirect.github.com/axios/axios/issues/11014">#11014</a>)</li> <li>Additional commits viewable in <a href="https://github.com/axios/axios/compare/v1.18.0...v1.18.1">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
f2774d4d3c |
chore: bump the react group across 1 directory with 3 updates (#27734)
[//]: # (dependabot-start) ⚠️ **Dependabot is rebasing this PR** ⚠️ Rebasing might not happen immediately, so don't worry if this takes some time. Note: if you make any changes to this PR yourself, they will take precedence over the rebase. --- [//]: # (dependabot-end) Bumps the react group with 3 updates in the /site directory: [react](https://github.com/react/react/tree/HEAD/packages/react), [@types/react](https://github.com/DefinitelyTyped/DefinitelyTyped/tree/HEAD/types/react) and [react-dom](https://github.com/react/react/tree/HEAD/packages/react-dom). Updates `react` from 19.2.6 to 19.2.8 <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/react/react/releases">react's releases</a>.</em></p> <blockquote> <h2>19.2.8 (July 21st, 2026)</h2> <h2>React Server Components</h2> <ul> <li>Performance improvements when decoding (<a href="https://redirect.github.com/facebook/react/pull/37087">#37087</a> by <a href="https://github.com/eps1lon"><code>@eps1lon</code></a>)</li> </ul> <h2>19.2.7 (June 1st, 2026)</h2> <h2>React Server Components</h2> <ul> <li>Fixed missing <code>FormData</code> entries in Server Actions which regressed in 19.2.6 (<a href="https://redirect.github.com/facebook/react/pull/36566">#36566</a> by <a href="https://github.com/unstubbable"><code>@unstubbable</code></a>)</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/react/react/blob/main/CHANGELOG.md">react's changelog</a>.</em></p> <blockquote> <h2>19.2.7 (June 1, 2026)</h2> <h3>React Server Components</h3> <ul> <li>Fixed missing <code>FormData</code> entries in Server Actions which regressed in 19.2.6 (<a href="https://github.com/unstubbable"><code>@unstubbable</code></a> <a href="https://redirect.github.com/facebook/react/pull/36566">#36566</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/react/react/commit/1dd4ecbdabf826f527fc9a58c05ea70375b7d170"><code>1dd4ecb</code></a> [FlightReply] Performance improvements when decoding (<a href="https://github.com/react/react/tree/HEAD/packages/react/issues/37087">#37087</a>)</li> <li><a href="https://github.com/react/react/commit/b0d2fdb78bdfae075a7fa02ddcebbf25f90952c2"><code>b0d2fdb</code></a> [19.2.x] Update required references to GitHub repo (<a href="https://github.com/react/react/tree/HEAD/packages/react/issues/36753">#36753</a>)</li> <li><a href="https://github.com/react/react/commit/6117d7cca4906492c51fe6a03381e35adfd86e7d"><code>6117d7c</code></a> Version 19.2.7 (<a href="https://github.com/react/react/tree/HEAD/packages/react/issues/36591">#36591</a>)</li> <li>See full diff in <a href="https://github.com/react/react/commits/v19.2.8/packages/react">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for react since your current version.</p> </details> <br /> Updates `@types/react` from 19.2.15 to 19.2.17 <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/DefinitelyTyped/DefinitelyTyped/commits/HEAD/types/react">compare view</a></li> </ul> </details> <br /> Updates `react-dom` from 19.2.6 to 19.2.8 <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/react/react/releases">react-dom's releases</a>.</em></p> <blockquote> <h2>19.2.8 (July 21st, 2026)</h2> <h2>React Server Components</h2> <ul> <li>Performance improvements when decoding (<a href="https://redirect.github.com/facebook/react/pull/37087">#37087</a> by <a href="https://github.com/eps1lon"><code>@eps1lon</code></a>)</li> </ul> <h2>19.2.7 (June 1st, 2026)</h2> <h2>React Server Components</h2> <ul> <li>Fixed missing <code>FormData</code> entries in Server Actions which regressed in 19.2.6 (<a href="https://redirect.github.com/facebook/react/pull/36566">#36566</a> by <a href="https://github.com/unstubbable"><code>@unstubbable</code></a>)</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/react/react/blob/main/CHANGELOG.md">react-dom's changelog</a>.</em></p> <blockquote> <h2>19.2.7 (June 1, 2026)</h2> <h3>React Server Components</h3> <ul> <li>Fixed missing <code>FormData</code> entries in Server Actions which regressed in 19.2.6 (<a href="https://github.com/unstubbable"><code>@unstubbable</code></a> <a href="https://redirect.github.com/facebook/react/pull/36566">#36566</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/react/react/commit/1dd4ecbdabf826f527fc9a58c05ea70375b7d170"><code>1dd4ecb</code></a> [FlightReply] Performance improvements when decoding (<a href="https://github.com/react/react/tree/HEAD/packages/react-dom/issues/37087">#37087</a>)</li> <li><a href="https://github.com/react/react/commit/b0d2fdb78bdfae075a7fa02ddcebbf25f90952c2"><code>b0d2fdb</code></a> [19.2.x] Update required references to GitHub repo (<a href="https://github.com/react/react/tree/HEAD/packages/react-dom/issues/36753">#36753</a>)</li> <li><a href="https://github.com/react/react/commit/6117d7cca4906492c51fe6a03381e35adfd86e7d"><code>6117d7c</code></a> Version 19.2.7 (<a href="https://github.com/react/react/tree/HEAD/packages/react-dom/issues/36591">#36591</a>)</li> <li>See full diff in <a href="https://github.com/react/react/commits/v19.2.8/packages/react-dom">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for react-dom since your current version.</p> </details> <br /> Updates `@types/react` from 19.2.15 to 19.2.17 <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/DefinitelyTyped/DefinitelyTyped/commits/HEAD/types/react">compare view</a></li> </ul> </details> <br /> Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore <dependency name> major version` will close this group update PR and stop Dependabot creating any more for the specific dependency's major version (unless you unignore this specific dependency's major version or upgrade to it yourself) - `@dependabot ignore <dependency name> minor version` will close this group update PR and stop Dependabot creating any more for the specific dependency's minor version (unless you unignore this specific dependency's minor version or upgrade to it yourself) - `@dependabot ignore <dependency name>` will close this group update PR and stop Dependabot creating any more for the specific dependency (unless you unignore this specific dependency or upgrade to it yourself) - `@dependabot unignore <dependency name>` will remove all of the ignore conditions of the specified dependency - `@dependabot unignore <dependency name> <ignore condition>` will remove the ignore condition of the specified dependency and ignore conditions </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
8342acee99 |
chore: bump @types/node from 22.20.0 to 22.20.1 in /offlinedocs (#27740)
Bumps [@types/node](https://github.com/DefinitelyTyped/DefinitelyTyped/tree/HEAD/types/node) from 22.20.0 to 22.20.1. <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/DefinitelyTyped/DefinitelyTyped/commits/HEAD/types/node">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
599e0ba98e |
chore: bump @chakra-ui/react from 2.10.9 to 2.10.10 in /offlinedocs (#27739)
Bumps [@chakra-ui/react](https://github.com/chakra-ui/chakra-ui/tree/HEAD/packages/react) from 2.10.9 to 2.10.10. <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/chakra-ui/chakra-ui/commits/@chakra-ui/react@2.10.10/packages/react">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
b518713ab7 |
chore: bump sanitize-html from 2.17.5 to 2.17.6 in /offlinedocs (#27738)
Bumps [sanitize-html](https://github.com/apostrophecms/apostrophe/tree/HEAD/packages/sanitize-html) from 2.17.5 to 2.17.6. <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/apostrophecms/apostrophe/blob/main/packages/sanitize-html/CHANGELOG.md">sanitize-html's changelog</a>.</em></p> <blockquote> <h2>2.17.6 (2026-07-10)</h2> <h3>Fixes</h3> <ul> <li>Allow transformTags to emit text when textFilter is set, even if the tag is initially empty. This is consistent with the documentation. Thanks to <a href="https://github.com/spokodev">spokodev</a> for the fix.</li> </ul> <h3>Security</h3> <ul> <li>Fixed an XSS/allowlist bypass in which the contents of a raw-text element (<code>textarea</code> or <code>xmp</code>) nested inside an <code>svg</code> or <code>math</code> root were re-emitted without HTML-escaping. <code>sanitize-html</code> treated that content as inert raw text because <code>htmlparser2</code> 10.x classified raw-text elements by tag name and ignored the namespace, but a real HTML5 parser treats <code>textarea</code>/<code>xmp</code> as ordinary foreign elements inside SVG/MathML and re-parses their contents as live markup. As a result, markup and event-handler attributes that the allowlist never permitted (for example <code><svg><textarea><img src=x onerror=alert(1)></code>) could survive sanitization and execute in the browser. This is now fixed on two fronts: <code>htmlparser2</code> was upgraded to 12.x, which is namespace-aware and parses <code>textarea</code>/<code>xmp</code> inside SVG/MathML as ordinary elements, so their non-allowlisted children (such as the injected <code>img</code>) are dropped by the allowlist instead of being preserved as raw text; and any raw-text content <code>sanitize-html</code> still emits for these tags (at HTML integration points such as <code>foreignObject</code>/<code>mtext</code>, or outside foreign content) is always HTML-escaped. The default configuration is not affected; the precondition is an <code>allowedTags</code> that includes <code>svg</code> or <code>math</code> together with <code>textarea</code> or <code>xmp</code>. Thanks to <a href="https://github.com/khoadb175">khoadb175</a> for responsibly disclosing the vulnerability.</li> <li>Fixed a mutation-XSS / <code>allowedTags</code> bypass affecting configurations that allow the <code>textarea</code> or <code>xmp</code> raw-text tags. <code>htmlparser2</code> 10.x did not recognize an end tag with a trailing solidus (e.g. <code></textarea/></code>) as closing the element, so it kept the following markup as raw text, but a spec-compliant browser treats <code></textarea/></code> as a valid close and parses that markup as a live element. Because raw-text content was re-emitted without escaping, a payload such as <code><textarea></textarea/><img src=x onerror=...></code> could smuggle non-allowlisted, executable markup through the sanitizer. The default configuration was not affected. This is now defended at two layers: <code>htmlparser2</code> was upgraded to 12.x, whose tokenizer closes these end tags correctly, and the raw text sanitize-html emits for these tags is always escaped so no <code><</code> can reopen a tag when the output is re-parsed (<code>textarea</code>, an RCDATA element whose entities <code>htmlparser2</code> decodes, is escaped like normal text, while <code>xmp</code>, a raw-text element, has only its angle brackets escaped to avoid double-encoding already-encoded entities). Because <code>htmlparser2</code> is ESM-only from version 11 onward, <code>sanitize-html</code> now requires Node.js <code>>=22.12.0</code> (the first 22.x release in which <code>require()</code> of an ES module is available unflagged). Thanks to <a href="https://github.com/bibu123456">bibu123456</a> for reporting the vulnerability and <a href="https://github.com/Kayiz-PT">Kayiz-PT</a> for coordinating the disclosure (GHSA-jxwj-j7wr-gfrw).</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/apostrophecms/apostrophe/commits/HEAD/packages/sanitize-html">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
e0fc756a75 |
chore: bump prettier from 3.9.4 to 3.9.6 in /offlinedocs (#27737)
Bumps [prettier](https://github.com/prettier/prettier) from 3.9.4 to 3.9.6. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/prettier/prettier/releases">prettier's releases</a>.</em></p> <blockquote> <h2>3.9.6</h2> <h2>What's Changed</h2> <ul> <li>Preserve quotes for methods named <code>new</code> (<a href="https://redirect.github.com/prettier/prettier/pull/19621">prettier/prettier#19621</a> by <a href="https://github.com/kovsu"><code>@kovsu</code></a>)</li> <li>Support <code>import defer</code> in <code>typescript</code> parser (<a href="https://redirect.github.com/prettier/prettier/pull/19624">prettier/prettier#19624</a>, <a href="https://redirect.github.com/prettier/prettier/pull/19675">prettier/prettier#19675</a> by <a href="https://github.com/fisker"><code>@fisker</code></a>)</li> <li>Added a new official plugin <a href="https://github.com/prettier/prettier/tree/3.9.6/packages/plugin-yuku"><code>@prettier/plugin-yuku</code> 🚀</a> (<a href="https://redirect.github.com/prettier/prettier/pull/19628">prettier/prettier#19628</a>, <a href="https://redirect.github.com/prettier/prettier/pull/19629">prettier/prettier#19629</a> by <a href="https://github.com/fisker"><code>@fisker</code></a>)</li> </ul> <p>🔗 <a href="https://github.com/prettier/prettier/blob/3.9.6/CHANGELOG.md#396">Changelog</a></p> <h2>3.9.5</h2> <p>🔗 <a href="https://github.com/prettier/prettier/blob/3.9.5/CHANGELOG.md#395">Changelog</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/prettier/prettier/blob/main/CHANGELOG.md">prettier's changelog</a>.</em></p> <blockquote> <h1>3.9.6</h1> <p><a href="https://github.com/prettier/prettier/compare/3.9.5...3.9.6">diff</a></p> <h4>TypeScript: Preserve quotes for methods named <code>new</code> (<a href="https://redirect.github.com/prettier/prettier/pull/19621">#19621</a> by <a href="https://github.com/kovsu"><code>@kovsu</code></a>)</h4> <!-- raw HTML omitted --> <pre lang="tsx"><code>// Input interface Container { "new"(id: string): number; } <p>// Prettier 3.9.5<br /> interface Container {<br /> new(id: string): number;<br /> }</p> <p>// Prettier 3.9.6<br /> interface Container {<br /> "new"(id: string): number;<br /> }<br /> </code></pre></p> <h4>TypeScript: Support <code>import defer</code> (<a href="https://redirect.github.com/prettier/prettier/pull/19624">#19624</a>, <a href="https://redirect.github.com/prettier/prettier/pull/19675">#19675</a> by <a href="https://github.com/fisker"><code>@fisker</code></a>)</h4> <!-- raw HTML omitted --> <pre lang="tsx"><code>// Input import defer * as foo from "foo"; <p>// Prettier 3.9.5<br /> import * as foo from "foo";</p> <p>// Prettier 3.9.6<br /> import defer * as foo from "foo";<br /> </code></pre></p> <h4>JavaScript: Added a new official plugin <code>@prettier/plugin-yuku</code> (<a href="https://redirect.github.com/prettier/prettier/pull/19628">#19628</a>, <a href="https://redirect.github.com/prettier/prettier/pull/19629">#19629</a> by <a href="https://github.com/fisker"><code>@fisker</code></a>)</h4> <p><code>@prettier/plugin-yuku</code> is powered by <a href="https://yuku.fyi/">Yuku</a> (A high-performance JavaScript/TypeScript compiler toolchain written in Zig).</p> <p>This plugin includes two new parsers: <code>yuku</code> (JavaScript syntax) and <code>yuku-ts</code> (TypeScript syntax).</p> <p><strong>To use this plugin:</strong></p> <ol> <li> <p>Install the plugin:</p> <pre lang="bash"><code>yarn add --dev prettier @prettier/plugin-yuku </code></pre> </li> </ol> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/prettier/prettier/commit/8f0c95057cc91d5836409466cd9d9af3bb901e84"><code>8f0c950</code></a> Release 3.9.6</li> <li><a href="https://github.com/prettier/prettier/commit/e9107647d0497d8ff1cacbb0f970d4543df77c1c"><code>e910764</code></a> Update changelog</li> <li><a href="https://github.com/prettier/prettier/commit/ec3f1c7bd74495992bc6954323a1a7fc8368808e"><code>ec3f1c7</code></a> Update typescript-eslint to v8.65.0 (<a href="https://redirect.github.com/prettier/prettier/issues/19675">#19675</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/73d2efc2c6cba6f579585c88ef171132d90834ec"><code>73d2efc</code></a> Update Yuku parser to v0.7.0 (<a href="https://redirect.github.com/prettier/prettier/issues/19664">#19664</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/dd5e24eabeab1f75ad573c79781e5fd408bcfad3"><code>dd5e24e</code></a> Preserve quotes for <code>TSMethodSignature</code> nodes named <code>new</code> (<a href="https://redirect.github.com/prettier/prettier/issues/19621">#19621</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/c03ab4e71c23154d6b11537eee3c938f0d0f67d3"><code>c03ab4e</code></a> Update dependency eslint-plugin-unicorn to v72 (<a href="https://redirect.github.com/prettier/prettier/issues/19633">#19633</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/b74dd53076c7208291a6b2e585c310844b41d35f"><code>b74dd53</code></a> Update Yuku parser to v0.6.5 (<a href="https://redirect.github.com/prettier/prettier/issues/19654">#19654</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/f1b594ea1db1520c383d0e281d623551f671f824"><code>f1b594e</code></a> Update dependency eslint-plugin-simple-import-sort to v14 (<a href="https://redirect.github.com/prettier/prettier/issues/19655">#19655</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/0d9dfb61530986373000dd107ea58ceebb79e233"><code>0d9dfb6</code></a> Update Yuku parser to v0.6.4 (<a href="https://redirect.github.com/prettier/prettier/issues/19650">#19650</a>)</li> <li><a href="https://github.com/prettier/prettier/commit/3bbb8159eb55575d4042653aa99f5f92a1416c19"><code>3bbb815</code></a> Remove <code>typescript-only</code> directory (<a href="https://redirect.github.com/prettier/prettier/issues/19636">#19636</a>)</li> <li>Additional commits viewable in <a href="https://github.com/prettier/prettier/compare/3.9.4...3.9.6">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
Jake Howell
|
79724ab0ba |
chore(site): migrate all <Dialog />s off MUI (#27506)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Removes Material UI from every dialog, moving them onto the internal shadcn/radix `Dialog` primitives. After this change there are **no** `@mui/material/Dialog` usages left in `site/src`. ## Changes - Consolidated `components/Dialogs/*` → `components/Dialog/*` and folded the old `ConfirmDeleteDialog` into `ConfirmDialog` (`type="delete"`). - Rewrote `ConfirmDialog`, `DeleteDialog`, `WorkspaceDeleteDialog`, `ScheduleDialog`, and `AnnouncementBannerDialog` onto the internal primitives (native `Input`/`Label`/`Checkbox`/`Link` instead of MUI). - Finished the migration for the last two MUI hold-outs: `UpdateBuildParametersDialog` and `MissingTemplateVariablesDialog`. - Dialog prop types now compose the rendered component's props (`ComponentProps<typeof Dialog>` / MUI `DialogProps`) instead of hand-rolled `{ open; onOpenChange }` shapes. ## Testing AI-Driven manual dogfood sweep in a live instance (premium license), driven in a browser. Each dialog checked for logical rendering (layout, variant styling, buttons, no overlap/blank/console error) and function (open, primary action, cancel/close, guard states): | Dialog / surface | How tested | Result | | --- | --- | --- | | `ConfirmDialog` (delete / info / success) | Token delete, update-confirm, change-version | ✅ | | `DeleteDialog` (type-to-confirm) | Delete user, group, license, provider, OAuth2 app | ✅ | | `WorkspaceDeleteDialog` | Workspace actions → Delete (+ orphan path via failed workspace) | ✅ | | `ScheduleDialog` | Template schedule → dormancy/deletion warning | ✅ | | `AnnouncementBannerDialog` | Deployment → Appearance → New banner (live preview + color) | ✅ | | `ChangeWorkspaceVersionDialog` | Workspace actions → Change version | ✅ | | `DownloadLogsDialog` | Workspace actions → Download logs | ✅ | | Batch delete (workspaces) | Workspaces list → multi-select → Delete | ✅ | | `TemplatePageHeader` delete | Template → Delete (cancelled) | ✅ | | `FileDialog` (create/rename/delete) | Template editor file tree | ✅ | | `MissingTemplateVariablesDialog` *(migrated)* | Editor → add variable → Build | ✅ | | `PublishTemplateVersionDialog` | Editor → Publish | ✅ | | `UpdateBuildParametersDialog` *(migrated)* | Classic flow + required param → workspace Update (renders + submits) | ✅ | | Update-confirmation (`WorkspaceUpdateDialogs`) | Workspace Update | ✅ | | Suspend/activate confirm | Users → member row | ✅ | | `ResetPasswordDialog` | Users → member → Reset password | ✅ | | Token delete confirm | Settings → Tokens | ✅ | | Create-token confirm | Token create flow | ✅ | | SSH key regenerate confirm | Settings → SSH Keys | ✅ | | Change-login-type confirm | Settings → Security | ✅ | | Secret delete | Settings → Secrets | ✅ | | Group delete | Admin → Groups | ✅ | | Org member remove | Admin → Organization → Members | ✅ | | License remove | Deployment → Licenses (cancelled) | ✅ | | Announcement banner delete | Deployment → Appearance | ✅ | | OAuth2 app delete | Deployment → OAuth2 apps | ✅ | | `ModelFormDialogs` (form + delete) | AI → Models | ✅ | | Provider delete | AI → Providers | ✅ | | Gateway key create/delete | AI → Gateway keys | ✅ | | `MCPServerFormDialogs` delete | AI → MCP servers | ✅ | | Personal skill (create form + delete) | Agents → Personal Skills | ✅ | | Spend user-override (add + delete) | AI → Spend | ✅ | Human tested: - [x] template version promote/archive - [x] external-auth/OAuth2-provider delete - [x] custom-role delete - [x] cancel-provisioner-job Things that have a chance to bleed: - tasks dialogs - dormant inline confirm Should be known that each of these renders through the already-verified `ConfirmDialog`/`DeleteDialog`, so the underlying component is covered even where the specific trigger wasn't reachable. <details> <summary>Plan & decision log</summary> **Goal:** finish the de-MUI migration everywhere and confirm every affected modal renders logically and functions. **Phase 1 - complete the migration** - Confirmed only two files still rendered MUI `Dialog` (`UpdateBuildParametersDialog`, `MissingTemplateVariablesDialog`); ported both to the internal primitives, preserving the `{ open, onClose, ... }` public API (mapped to `onOpenChange` internally) so call sites were unchanged. radix now wires `aria-labelledby`/`aria-describedby`, removing a duplicated element id. **Phase 2 - sighting sweep (live browser, premium license)** - Batch A (workspaces/tasks): 4 PASS, rest state-gated. - Batch B (templates): `MissingTemplateVariablesDialog`, `FileDialog`, `PublishTemplateVersionDialog`, template delete - all PASS. - `UpdateBuildParametersDialog`: reached by enabling classic parameter flow + pushing a version with a required parameter - PASS (renders + submits). - Batch C (users/org/settings): 10 PASS. - Batch D (deployment/AI): 10 PASS. **Decisions** - Kept `ConfirmDialog`-wrapper prop types explicit (composing `DialogProps` there reintroduced a MUI smell). - Dropped the unused `ConfirmDialogType` export (knip) and updated the `WorkspacePage` orphan-delete test: the radix `Checkbox` puts the test id on the `role=checkbox` button itself, so the previous `within(...).getByRole` no longer matched. </details> |
||
|
Michael Suchacz
|
bc9c7855d9 | fix: build actionlint from source to avoid the shellcheck deadlock (#27679) | ||
|
dylanhuff-at-coder
|
e30a7bcd0d | fix(site/src/pages/UserSettingsPage/SecretsPage): prevent Add secret dialog overflow (#27649) |

