mirror of
https://github.com/coder/coder.git
synced 2026-09-22 05:05:20 +08:00
a7377f761377a52d030d38393861de261e1ed011
14127
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Nick Vigilante |
a7377f7613 |
fix(Makefile): map arm64 to aarch64 for typos binary download (#24986)
macOS ARM reports arm64 via uname -m, but typos GitHub release assets use aarch64 in their filenames. The mismatch produces a 404, so the build/typos-$(VERSION) target fails silently and Apple Silicon users fall back to whatever typos binary their environment provides, such as the one from nix. That binary may be a different version than the one pinned in CI, creating a skew where local lint/typos rejects strings that CI accepts. <!-- If you have used AI to produce some or all of this PR, please ensure you have read our [AI Contribution guidelines](https://coder.com/docs/about/contributing/AI_CONTRIBUTING) before submitting. --> |
||
|
Michael Suchacz
|
2874d4b4cd |
feat: add chat debug retention purge (#24943)
> Mux is acting on Mike's behalf. Adds configurable retention for chat debug data, including the purge query, updated_at index, site config, experimental API, SDK types, frontend lifecycle setting, and docs. The purge deletes debug runs older than the configured retention window and relies on existing cascades to delete steps. The default retention is 30 days, and setting the value to 0 disables the purge. |
||
|
Kayla はな
|
57a6421670 | fix(site): ignore empty file path segments in template file tree (#24980) | ||
|
Kayla はな
|
21a877df84 |
feat: update OrganizationMembersPage role editing to match new designs (#24858)
|
||
|
Dean Sheather
|
e48d12160f |
fix(coderd): cut DB fan-out on agent instance-identity auth (#24973)
## Summary Restores `v2.33.0-rc.2`-equivalent query cost for agent instance-identity auth on `v2.33.0-rc.3`, which currently saturates the pgx pool when multiple agents share an instance ID. Customer report against rc.3 traced 233× `Internal error fetching provisioner job resource. fetch related workspace build: context canceled` 500s during a 50-minute incident window to this path. Backport to `release/2.33` will follow as a separate PR after this merges. ## Root cause [#24325](https://github.com/coder/coder/pull/24325) ("support multiple agents with shared instance-identity auth") rewrote `coderd/workspaceresourceauth.go::handleAuthInstanceID` to use the new `:many` agent lookup followed by a per-candidate filter loop. Each iteration synchronously calls `GetWorkspaceResourceByID` and `GetProvisionerJobByID`. Both go through `dbauthz`, and both fan out into the same `provisioner_job → workspace_build → workspace` cascade because `authorizeProvisionerJob` always re-authorizes the workspace via `GetWorkspaceBuildByJobID → GetWorkspaceByID`. The handler then re-fetches resource and job again for the surviving agent. Net effect on the agent-auth happy path: | | SQL | RBAC | |---|---|---| | rc.2 baseline | 13 | 5 | | rc.3 today, 1 agent | 19 | 7 | | rc.3 today, 2 agents | 26 | 9 | | **After this PR, 1 agent** | **6** | **3** | | **After this PR, 2 agents** | **7** | **3** | Under load, the rc.3 chain blocks on pool acquire and the request blows past the 30s HTTP write timeout. ## Changes ### 1. System fast-path on `authorizeProvisionerJob` (`coderd/database/dbauthz/dbauthz.go`) Add an `AsSystemRestricted` early-return at the top of `authorizeProvisionerJob`. Instance-identity auth has already proven cloud identity before reaching the DB layer, so re-authorizing the workspace on every provisioner-job lookup is pure overhead. Existing `GetWorkspaceAgentsByInstanceID` already uses the same fast-path pattern. ```go if err := q.authorizeContext(ctx, policy.ActionRead, rbac.ResourceSystem); err == nil { return nil } ``` ### 2. Drop survivor re-fetch in `handleAuthInstanceID` (`coderd/workspaceresourceauth.go`) Capture the provisioner job alongside each candidate during the filter loop so the survivor lookup does not re-fetch resource and job after selection. The previous code fired the resource→job→build→workspace cascade twice for the surviving agent. ## Tests Adds `TestAuthorizeProvisionerJob_SystemFastPath` in `coderd/database/dbauthz/dbauthz_test.go` with two sub-tests: - `AsSystemRestricted/SkipsCascade` — strict mock fails the test if `GetWorkspaceBuildByJobID` or `GetWorkspaceByID` is called. - `NonSystemActor/StillCascades` — auditor (no `ResourceSystem`) still pays the cascade and produces a `NotAuthorized` error, proving the fast-path is gated correctly. Updates 12 existing dbauthz suite cases to expect the new `ResourceSystem.Read` check ahead of the workspace/template-version check, with `FailSystemObjectChecks()` to force the slow path. Existing integration coverage in `TestPostWorkspaceAuthAWSInstanceIdentity/Ambiguous/{SingleAgent, MultipleAgentsWithSelector, MultipleAgentsNoSelector, SubAgentExcluded, ...}` exercises Part 2 end-to-end and continues to pass. ## Footprint - 3 files changed, +166/-48 - No SQL changes - No `make gen` - No migrations - No audit-table updates ## Validation - [x] `go test ./coderd/database/dbauthz/` — full suite, ~6s - [x] `go test -run TestPostWorkspaceAuth ./coderd/` — instance-identity handler tests - [x] `go test -run TestProvisionerJob ./coderd/` - [x] `go test -run TestWorkspaceAgent ./coderd/` - [x] `go test ./coderd/provisionerdserver/` - [x] `gofmt -l` clean ## Alternatives considered - **SQL-side filter:** rewrite `GetWorkspaceAgentsByInstanceID` to join `workspace_resources`/`provisioner_jobs` and filter `job.type = 'workspace_build'` server-side, eliminating the filter loop entirely. Cleaner long-term, but changes generated SQL and is too much surface for a release-branch hotfix. Worth doing as a follow-up. - **Full revert of #24325:** removes the multi-agent feature outright; conflicts with downstream commits ([#24441](https://github.com/coder/coder/pull/24441), [#24438](https://github.com/coder/coder/pull/24438), [#24313](https://github.com/coder/coder/pull/24313)). Reserved as fallback if the surgical fix doesn't hold under load testing. |
||
|
david-fraley
|
e7360da974 | docs: generate Chats API docs from swagger annotations (#24830) | ||
|
Ben Potter
|
cfce751b8a |
docs(docs): improve Docker daemon troubleshooting for all platforms (#24922)
Improves the Docker daemon troubleshooting in the quickstart and Docker install docs: - Renames the quickstart entry from "Cannot connect to the Docker daemon on Linux" to cover all platforms. - Adds a plain-English explanation of what the error means (Docker is not installed or not running). - Adds tabbed macOS/Linux/Windows instructions to the quickstart (macOS and Windows were missing). - Simplifies the Linux steps to match what Step 1 of the quickstart already teaches. - Adds a matching entry to `docs/install/docker.md` with a cross-link to the quickstart for platform-specific steps. Supersedes #24907 which was closed without merging. Fixes https://linear.app/codercom/issue/DEVREL-23 > Generated with [Coder Agents](https://coder.com/agents) |
||
|
Matt Vollmer
|
f6779af072 |
docs: swap Coder Agents and Coder Tasks order in manifest (#24974)
Swap the order of the `Coder Agents` and `Coder Tasks` entries inside the AI Coder section of `docs/manifest.json` so `Coder Agents` appears before `Coder Tasks` in the docs sidebar. No content changes; the two top-level child objects and their subtrees are swapped, with trailing-comma placement adjusted to keep the JSON valid. --- PR generated with Coder Agents |
||
|
Zach
|
1b2a1af097 |
feat: report user secrets adoption summary in telemetry (#24854)
Add a deployment-wide user secrets summary to the telemetry snapshot so we can track adoption of user secrets The summary reports: - A breakdown of secrets by which injection fields are populated: EnvNameOnly, FilePathOnly, Both, Neither - The distribution of secrets per user (max, p25, p50, p75, p90) All metrics are scoped to active non-system users. Soft-deleted users are excluded. The percentile distribution is computed across the entire active non-system user base, including users with zero secrets, so the percentiles reflect deployment-wide adoption. Assisted by Coder Agents. |
||
|
Matt Vollmer
|
e189f73cc0 |
docs: close Coder Agents coverage gaps and align nav references (#24971)
Closes coverage gaps in `docs/ai-coder/agents/` and aligns nav references with the current UI (post #24574 Behavior split, post #24644 Insights removal). **Content fixes:** - Replace site-wide `coder users edit-roles` flow with org-scoped `agents-access` role (per migration `000475`). CLI examples now preserve existing org roles since `edit-roles` overwrites the full set. - Correct computer-use claim: supports Anthropic *and* OpenAI providers, configured under the Virtual desktop experiment. - New `platform-controls/experiments.md` covering Virtual desktop, Advisor, and Chat debug logging (each as: what, how to enable, API). Includes the Debug tab in the chat right panel. - Trim `models.md` "Model overrides" to essentials: two layers (admin subagent, user personal), contexts table, resolution order, API pointer. - Remove retired `platform-controls/pr-insights.md` (page + manifest + cross-links). **Nav cleanup:** - Admin-only tabs use the full `Agents > Settings > Manage Agents > <Tab>` path; user-side tabs keep `Agents > Settings > <Tab>`. - Replace stale "Behavior" references with Instructions / Lifecycle / Experiments to match the current sidebar. - Replace references to the removed top-bar Admin dialog with the Settings sidebar. <details> <summary>Decision log</summary> - Experimental features were originally drafted as a standalone Advisor page plus inline sections in `platform-controls/index.md`. Consolidated into one `experiments.md` since no individual feature warrants a full page yet and parallel short sections are easier to scan. - Reviewer feedback on early drafts: drop the inline experiments list from `index.md` (avoid drift), drop the "users created before this role was introduced" note (handled transparently by migration `000475`), specify the full nav path for per-model pricing, link the `type=computer_use` row in `architecture.md` to the Experiments page. - CLI bulk-grant script previously called `edit-roles <user> agents-access`. That replaces the user's full org role set, so the script would silently strip `organization-admin`, `organization-template-admin`, etc. Rewrote to read each user's current roles, append `agents-access`, dedupe, and write the union back. </details> PR generated with Coder Agents. |
||
|
david-fraley
|
526059e254 | docs: add Coder Agents AI Gateway client page (#24829) | ||
|
Ben Potter
|
83f44dcaeb |
docs(docs/ai-coder/agents): note OpenAI as a supported computer-use provider (#24967)
PR #24772 (merged 2026-05-04) added OpenAI alongside Anthropic for computer use, plus an admin selector under the virtual desktop toggle. Three places in the agents docs still said "Anthropic only" — this updates them. No other content changes. Anthropic is still the default. Fixes [CODAGT-310](https://linear.app/codercom/issue/CODAGT-310/enable-openai-computer-use-in-codercoder) --- @nickvigilante — heads up, the kind of release-train drift we keep hitting: - Feature is on `main`, so docs on `main` need to describe it. - Feature is **not** in `release/2.33` and **not** in `v2.34.0-rc.0` (both cut before #24772 merged). It will ship in v2.34. - `coder.com/docs` follows `main`, so once this lands, v2.33 users see "OpenAI is supported" and find no toggle. Fwiw our [`doc-check` workflow](https://github.com/coder/coder/blob/main/.github/workflows/doc-check.yaml) would have caught this on #24772 — it's exactly what it's for. It [did trigger](https://github.com/coder/coder/actions/runs/25326759671) but the chat-create step errored out (curl exit 22) and nobody re-ran it, so the analysis never happened. Worth tightening that path so a transient API blip doesn't silently skip the check. > Generated with [Coder Agents](https://coder.com/agents) |
||
|
david-fraleyandMatt Vollmer
|
81109e17df |
docs(docs/ai-coder): add deprecation notice to Coder Tasks pages (#24831)
Adds a deprecation warning callout to the top of the main Coder Tasks docs page (`docs/ai-coder/tasks.md`). The message reads: > Beginning June 2026, Coder Tasks will be deprecated. Support for Tasks will be maintained on Coder's ESR release and through Coder v2.36. After v2.36, support for Tasks will only be on our 12-month ESR release for Coder Premium Customers. Uses the existing `> [!WARNING]` admonition pattern already used for deprecations elsewhere in the docs (e.g. `docs/ai-coder/ai-gateway/mcp.md`). Linear: [CODAGT-157](https://linear.app/codercom/issue/CODAGT-157/ensure-docs-are-updated-for-beta) --- _This PR was opened by Coder Agents on @davidfraley's behalf._ --------- Co-authored-by: Matt Vollmer <matthewjvollmer@outlook.com> |
||
|
Zach
|
e4622e79a5 |
refactor: use terraform provider methods for user secret env var names (#24946)
The original PR that plumbed secrets to the terraform provider landed before updating terraform-provider-coder to a version that codified the environment variable API contract. This change uses the exported functions from terraform-coder-provider to ensure the contract is defined in one place. |
||
|
Zach
|
f4197d676c |
refactor: remove unused tailnet connIO stats fields (#24911)
Drop start, lastWrite, and overwrites fields on connIO along with the
Stats() and Overwrites() methods. They have had no readers since
|
||
|
Steven Masley
|
9b4666020b |
fix(site): show cross-org workspaces as disabled in chat picker (#24944)
All user workspaces now appear in the picker. Workspaces from a different organization are rendered as disabled (greyed out, not selectable) with a tooltip on hover: "Chat and workspace must be in the same organization." |
||
|
Danielle Maywood
|
5322755691 | fix(site/src/pages/AgentsPage/components/ChatElements): align code block rendering (#24966) | ||
|
david-fraley
|
f585d3e9db | docs: add Tasks to Chats API migration guide (#24841) | ||
|
Jaayden Halko
|
dd2b121b20 |
feat(site/src/pages/AgentsPage): guide users when chat providers or models are missing (#24863)
<img width="674" height="508" alt="Screenshot 2026-05-04 at 20 43 11" src="https://github.com/user-attachments/assets/de33dba9-33f5-4dbe-a1af-9bff5f048b8f" /> When the agents chat page loads with no chat providers or no chat models configured, new users currently get no in-product guidance about the missing setup step. also adds a Add model button on the provider page after a provider is setup This adds a setup notice rendered as a no dismissable modalthat explains both a provider and a model must be configured before agents can be used. The notice conditionally links to `/agents/settings/providers` and/or `/agents/settings/models` depending on which is missing, and only renders after the relevant config queries succeed (no flash during loading). |
||
|
Jaayden Halko
|
a24ebb9d38 |
fix: keep agents desktop layout at 200% zoom (#24699)
Fixes layout issues on the agents empty state page. 1. At 200% zoom on a 1440 px desktop, the CSS viewport shrinks to 720 px, which was below the previous `md:` breakpoint (768 px) and collapsed the page into the mobile stack. Switching the page shell and shell-level controls to the `sm:` breakpoint (640 px) keeps the sidebar and chat area side-by-side at common zoom levels while preserving the mobile stack for real phone viewports. 2. The empty state stays bottom-aligned on mobile and centered on the desktop branch, with tighter spacing so the chat input sits closer to the bottom of the screen at 200% zoom. 3. The inner stack gap shrinks from `gap-4` (16 px) to `gap-2` (8 px) and the footer paragraph drops its `mt-1`, tightening the space around the organization selector, the chat input, and the "Introductory access to Coder Agents through September 2026" line. 4. Sidebar header/footer controls, the page header, the chat top bar, and the plan-mode badge now use the same `sm:` desktop breakpoint as the page shell. A collapsed sidebar can be expanded again at 640 to 767 px. Dropdown full-width CSS (`@media (max-width: 767px)`) and the `isBelowMdViewport` helper are intentionally left at 768 px. Those govern dropdown UX rather than page layout, and the chat pane is still narrow at 640 to 767 px after the sidebar is visible. The page is in desktop mode in that range while dropdowns stay full-width. <img width="1460" height="858" alt="Screenshot 2026-04-30 at 23 03 48" src="https://github.com/user-attachments/assets/62072432-6edf-4bf5-9a7f-88fd69f89602" /> <img width="1460" height="856" alt="Screenshot 2026-04-30 at 23 03 57" src="https://github.com/user-attachments/assets/76d94673-ac45-4a50-9c6b-3cfeffa1d6c7" /> Regression coverage in Storybook: - `AgentsPageView.stories.tsx > EmptyStateZoom200Desktop` pins a new 720 px Chromatic viewport and asserts the rendered layout is horizontal, the sidebar is left of the main panel, and the sidebar header/footer controls are visible. - `AgentsPageView.stories.tsx > CollapsedSidebarZoom200Desktop` pins the same 720 px viewport and asserts the expand-sidebar control is visible when the sidebar is collapsed. - `AgentCreateForm.stories.tsx > OrgPickerTightSpacing` measures the vertical gap between the org selector row and the chat-input composer and expects it to stay below 16 px. --- Generated by Coder Agents. |
||
|
Ben Potter
|
63db689ab7 |
fix(site/src/pages/AgentsPage): cap queued messages list height so chat scroll keeps working (#24950)
Linear: [CODAGT-313](https://linear.app/codercom/issue/CODAGT-313/unable-to-scroll-long-queued-messages-in-coder-agents) ## Summary When many messages are queued in the agent chat, the chat history becomes unscrollable: mouse wheel and scrollbar drag both stop responding. The input wrapper in `AgentChatPageView.tsx:496` is `shrink-0 overflow-y-auto` with **no `max-height`**, so `overflow-y-auto` is a no-op and the section grows unbounded as `QueuedMessagesList` adds rows. Its sibling `ChatScrollContainer` is `flex-1 min-h-0`, so it absorbs the shrinkage and `clientHeight` collapses to 0. The chat list is then a zero-height viewport with nothing to scroll. Measured against the actual `AgentChatPageView` rendered in Storybook with 20 queued messages (1280x800): | | scroll-container `clientHeight` | input wrapper height | scrollable? | |---|---:|---:|---| | 0 queued | 502 px | 270 px | yes | | 20 queued, `main` | **0 px** | 1182 px | **no** | | 20 queued, this PR | 258 px | 502 px | yes | ## Demo 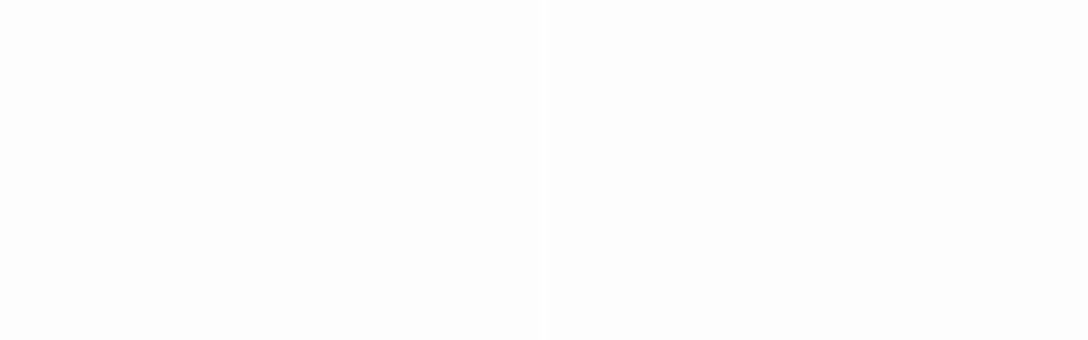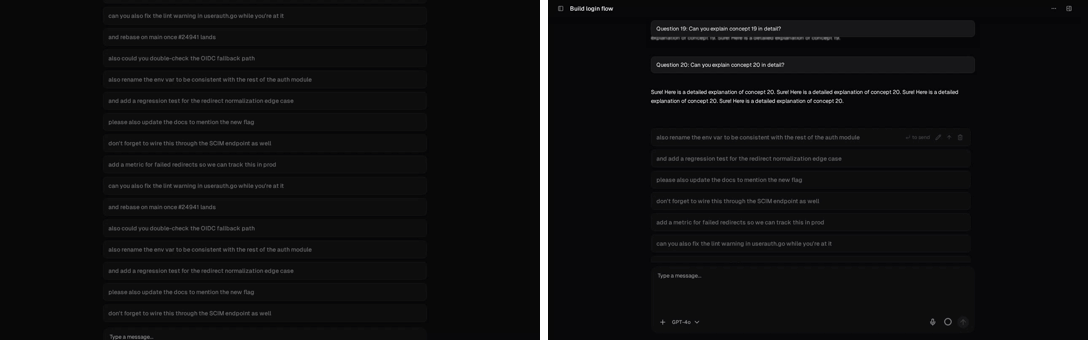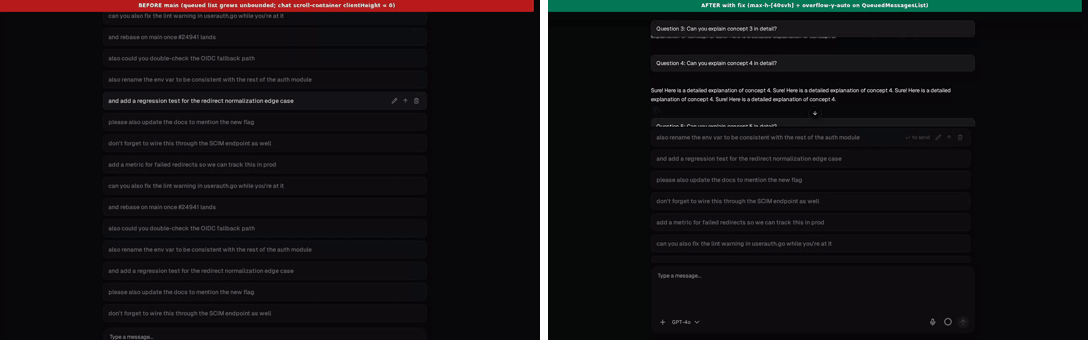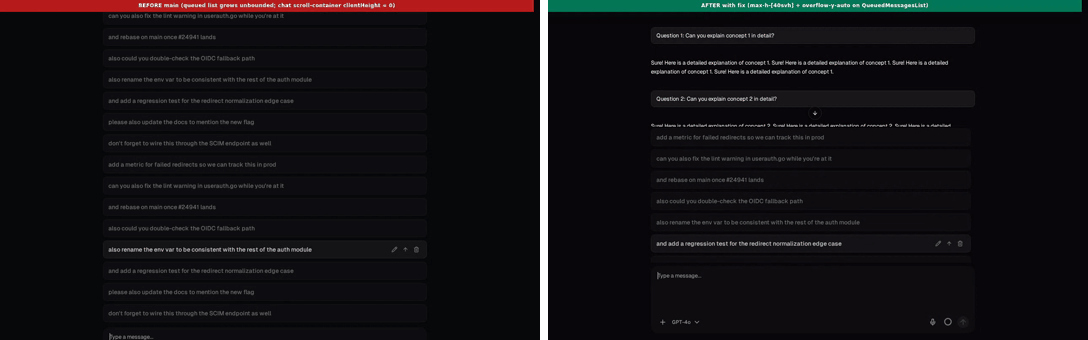 Left (`main`): wheel-up does nothing because the chat scroll container has been crushed to zero height. Right (this PR): the queued list scrolls inside its own pane and the chat history scrolls normally. Recording is `AgentChatPageView` rendered through Storybook with the production component source. The same gesture (wheel-up over the chat history, then wheel-down over the queued list) is applied to both sides. Source for the recording is in `bpmct/codagt-313-assets`. ## Change ```diff - <div className={cn("flex w-full flex-col", className)}> + // Cap the queue at ~40% of the small viewport so a long queue + // does not push the chat history's scroll container down to + // zero height (CODAGT-313). The list scrolls inside its own pane. + <div + className={cn( + "flex w-full flex-col max-h-[40svh] overflow-y-auto [scrollbar-gutter:stable] [scrollbar-width:thin] [scrollbar-color:hsl(var(--surface-quaternary))_transparent]", + className, + )} + > ``` ## Why this spot, not the outer wrapper The composer textarea already self-caps at `max-h-[50vh]` in `ChatMessageInput.tsx:688`, so the only unbounded growth source in the input section is the queued list. Capping the list keeps the constraint colocated with the component that owns it, and any future consumer of `QueuedMessagesList` is automatically safe. `40svh` (small viewport height) so the queue doesn't fight with the iOS keyboard once it appears, matching the `h-dvh` decision in #24848. --- *Generated by Coder Agents.* |
||
|
david-fraley
|
98ea5266c3 | docs: point to Coder Agents and drop Tasks walkthrough in quickstart (#24833) | ||
|
david-fraley
|
c0e72e272d | docs(docs/ai-coder/agents): correct chat statuses, watch events, auto-archive default, and add attach_file tool (#24828) | ||
|
david-fraley
|
1611862481 | docs: rename Early Access to Beta and remove early-access page (#24826) | ||
|
dependabot[bot]
|
b35a11cece |
chore: bump google.golang.org/grpc from 1.80.0 to 1.81.0 (#24959)
Bumps [google.golang.org/grpc](https://github.com/grpc/grpc-go) from 1.80.0 to 1.81.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/grpc/grpc-go/releases">google.golang.org/grpc's releases</a>.</em></p> <blockquote> <h2>Release 1.81.0</h2> <h1>Behavior Changes</h1> <ul> <li>balancer/rls: Switch gauge metrics to asynchronous emission (once per collection cycle) to reduce telemetry noise and align with other gRPC language implementations. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8808">#8808</a>)</li> </ul> <h1>Dependencies</h1> <ul> <li>Minimum supported Go version is now 1.25. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8969">#8969</a>)</li> </ul> <h1>Bug Fixes</h1> <ul> <li>xds: Use the leaf cluster's security config for the TLS handshake instead of the aggregate cluster's config. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8956">#8956</a>)</li> <li>transport: Send a <code>RST_STREAM</code> when receiving an <code>END_STREAM</code> when the stream is not already half-closed. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8832">#8832</a>)</li> <li>xds: Fix ADS resource name validation to prevent a panic. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8970">#8970</a>)</li> </ul> <h1>New Features</h1> <ul> <li>grpc/stats: Add support for custom labels in per-call metrics (<a href="https://github.com/grpc/proposal/blob/master/A108-otel-custom-per-call-label.md">gRFC A108</a>). (<a href="https://redirect.github.com/grpc/grpc-go/issues/9008">#9008</a>)</li> <li>xds: Add support for Server Name Indication (SNI) and SAN validation (<a href="https://github.com/grpc/proposal/blob/master/A101-SNI-setting-and-SNI-SAN-validation.md">gRFC A101</a>). Disabled by default. To enable, set <code>GRPC_EXPERIMENTAL_XDS_SNI=true</code> environment variable. (<a href="https://redirect.github.com/grpc/grpc-go/issues/9016">#9016</a>)</li> <li>xds: Add support to control which fields get propagated from ORCA backend metric reports to LRS load reports (<a href="https://github.com/grpc/proposal/blob/master/A85-lrs-custom-metrics-changes.md">gRFC A85</a>). Disabled by default. To enable, set <code>GRPC_EXPERIMENTAL_XDS_ORCA_LRS_PROPAGATION=true</code>. (<a href="https://redirect.github.com/grpc/grpc-go/issues/9005">#9005</a>)</li> <li>xds: Add metrics to track xDS client connectivity and cached resource state (<a href="https://github.com/grpc/proposal/blob/master/A78-grpc-metrics-wrr-pf-xds.md">gRFC A78</a>). (<a href="https://redirect.github.com/grpc/grpc-go/issues/8807">#8807</a>)</li> <li>stats/otel: Enhance <code>grpc.subchannel.disconnections</code> metric by adding disconnection reason to the <code>grpc.disconnect_error</code> label (<a href="https://github.com/grpc/proposal/blob/master/A94-subchannel-otel-metrics.md">gRFC A94</a>). This provides granular insights into why subchannels are closing. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8973">#8973</a>)</li> <li>mem: Add <code>mem.Buffer.Slice()</code> API to slice the buffer like a slice. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8977">#8977</a>) <ul> <li>Special Thanks: <a href="https://github.com/ash2k"><code>@ash2k</code></a></li> </ul> </li> </ul> <h1>Performance Improvements</h1> <ul> <li>alts: Pool read buffers to lower memory utilization when sockets are unreadable. (<a href="https://redirect.github.com/grpc/grpc-go/issues/8964">#8964</a>)</li> <li>transport: Pool HTTP/2 framer read buffers to reduce idle memory consumption. Currently limited to Linux for ALTS and non-encrypted transports (TCP, Unix). To disable, set <code>GRPC_GO_EXPERIMENTAL_HTTP_FRAMER_READ_BUFFER_POOLING=false</code> and report any issues. (<a href="https://redirect.github.com/grpc/grpc-go/issues/9032">#9032</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/grpc/grpc-go/commit/cb18228317ff523e63d931b4058b0329585b7dcd"><code>cb18228</code></a> Change version to 1.81.0 (<a href="https://redirect.github.com/grpc/grpc-go/issues/9062">#9062</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/96748f973e20bbfcafa19a8bdffc85ad5da138d1"><code>96748f9</code></a> Cherry-pick <a href="https://redirect.github.com/grpc/grpc-go/issues/9105">#9105</a> to 1.81.x (<a href="https://redirect.github.com/grpc/grpc-go/issues/9106">#9106</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/91832222f0144f76527b630ca55cfea6e1aa015a"><code>9183222</code></a> Cherry pick <a href="https://redirect.github.com/grpc/grpc-go/issues/9055">#9055</a>, <a href="https://redirect.github.com/grpc/grpc-go/issues/9032">#9032</a> to v1.81.x (<a href="https://redirect.github.com/grpc/grpc-go/issues/9095">#9095</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/5cba6da4211f3b130238c792937f5921741b616a"><code>5cba6da</code></a> Revert "deps: update dependencies for all modules (<a href="https://redirect.github.com/grpc/grpc-go/issues/9065">#9065</a>)" (<a href="https://redirect.github.com/grpc/grpc-go/issues/9067">#9067</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/af8a9364aa7523ab24d214e9ef13e6ad64d5c5f9"><code>af8a936</code></a> deps: update dependencies for all modules (<a href="https://redirect.github.com/grpc/grpc-go/issues/9065">#9065</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/cdc60dfaaadde45e16aa3c28237c0e655a722c1a"><code>cdc60df</code></a> transport: optimize heap allocations in ready reader and update syscall conne...</li> <li><a href="https://github.com/grpc/grpc-go/commit/208d053e3204c806ba9e6205c26aa064c8b42852"><code>208d053</code></a> xds/resolver: pass complete XDSConfig in RPC context for HTTP filters (gRFC A...</li> <li><a href="https://github.com/grpc/grpc-go/commit/50fe1cc7fd78b78ae638ed90ea78514c934167ac"><code>50fe1cc</code></a> test: Fix flaky test <code>TestServerStreaming_ClientCallRecvMsgTwice</code> in `end2end...</li> <li><a href="https://github.com/grpc/grpc-go/commit/d574bad188f25ba03d41a506e6f2ef93837ad10b"><code>d574bad</code></a> build(deps): bump go.opentelemetry.io/otel/sdk from 1.42.0 to 1.43.0 (<a href="https://redirect.github.com/grpc/grpc-go/issues/9050">#9050</a>)</li> <li><a href="https://github.com/grpc/grpc-go/commit/b8bf4d0488a351c563d63797ffba321585d6bb24"><code>b8bf4d0</code></a> build(deps): bump go.opentelemetry.io/otel/sdk from 1.42.0 to 1.43.0 in /inte...</li> <li>Additional commits viewable in <a href="https://github.com/grpc/grpc-go/compare/v1.80.0...v1.81.0">compare view</a></li> </ul> </details> <br /> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
f09c1bd695 |
chore: bump google.golang.org/api from 0.276.0 to 0.277.0 (#24961)
Bumps [google.golang.org/api](https://github.com/googleapis/google-api-go-client) from 0.276.0 to 0.277.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/googleapis/google-api-go-client/releases">google.golang.org/api's releases</a>.</em></p> <blockquote> <h2>v0.277.0</h2> <h2><a href="https://github.com/googleapis/google-api-go-client/compare/v0.276.0...v0.277.0">0.277.0</a> (2026-04-29)</h2> <h3>Features</h3> <ul> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3567">#3567</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/39582952e4eac1b744499f8a8063a4a5f1ce7d6b">3958295</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3571">#3571</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/ca9851efc573231ca1ed9c6fea4bc77d6052d0bb">ca9851e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3574">#3574</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/8efb1afa0e5d9cc454f721124bba3881f3935e3c">8efb1af</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3575">#3575</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/de49bb519cab881f74e5b9ba11e263a2b9a4ad2e">de49bb5</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3577">#3577</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/ce68c87d9dc6c144b6df578df725470b30cf83d6">ce68c87</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3578">#3578</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/8be033e24e0c6ddb08a3df72c0a8997d21623a22">8be033e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3579">#3579</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/bc6990e20803f2ff2fd1b77995f6e9180ab2302b">bc6990e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3580">#3580</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/2de1a5aff3f3b6e53dff00da297c5d249ac8d791">2de1a5a</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3581">#3581</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/0c219d90e90899c93215558f3ea309c9732bf7ea">0c219d9</a>)</li> </ul> <h3>Bug Fixes</h3> <ul> <li><strong>idtoken:</strong> Avoid double impersonation in tokenSourceFromBytes (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3576">#3576</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/75172cf5cb7bfc260c22e481323355306f684a09">75172cf</a>), refs <a href="https://redirect.github.com/googleapis/google-api-go-client/issues/2301">#2301</a></li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/googleapis/google-api-go-client/blob/main/CHANGES.md">google.golang.org/api's changelog</a>.</em></p> <blockquote> <h2><a href="https://github.com/googleapis/google-api-go-client/compare/v0.276.0...v0.277.0">0.277.0</a> (2026-04-29)</h2> <h3>Features</h3> <ul> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3567">#3567</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/39582952e4eac1b744499f8a8063a4a5f1ce7d6b">3958295</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3571">#3571</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/ca9851efc573231ca1ed9c6fea4bc77d6052d0bb">ca9851e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3574">#3574</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/8efb1afa0e5d9cc454f721124bba3881f3935e3c">8efb1af</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3575">#3575</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/de49bb519cab881f74e5b9ba11e263a2b9a4ad2e">de49bb5</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3577">#3577</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/ce68c87d9dc6c144b6df578df725470b30cf83d6">ce68c87</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3578">#3578</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/8be033e24e0c6ddb08a3df72c0a8997d21623a22">8be033e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3579">#3579</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/bc6990e20803f2ff2fd1b77995f6e9180ab2302b">bc6990e</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3580">#3580</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/2de1a5aff3f3b6e53dff00da297c5d249ac8d791">2de1a5a</a>)</li> <li><strong>all:</strong> Auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3581">#3581</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/0c219d90e90899c93215558f3ea309c9732bf7ea">0c219d9</a>)</li> </ul> <h3>Bug Fixes</h3> <ul> <li><strong>idtoken:</strong> Avoid double impersonation in tokenSourceFromBytes (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3576">#3576</a>) (<a href="https://github.com/googleapis/google-api-go-client/commit/75172cf5cb7bfc260c22e481323355306f684a09">75172cf</a>), refs <a href="https://redirect.github.com/googleapis/google-api-go-client/issues/2301">#2301</a></li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/googleapis/google-api-go-client/commit/dd598a60e19f836bb7ad709311b21d303bbab6c8"><code>dd598a6</code></a> chore(main): release 0.277.0 (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3568">#3568</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/b208a86db380e5e517451daa4e5f63fae1f723be"><code>b208a86</code></a> chore(all): update all (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3573">#3573</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/0c219d90e90899c93215558f3ea309c9732bf7ea"><code>0c219d9</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3581">#3581</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/75172cf5cb7bfc260c22e481323355306f684a09"><code>75172cf</code></a> fix(idtoken): avoid double impersonation in tokenSourceFromBytes (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3576">#3576</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/2de1a5aff3f3b6e53dff00da297c5d249ac8d791"><code>2de1a5a</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3580">#3580</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/60b078419409e11bc414c7ccbaf4d32ddfe2a5b0"><code>60b0784</code></a> chore(deps): bump github.com/go-git/go-git/v5 from 5.17.1 to 5.18.0 in /inter...</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/bc6990e20803f2ff2fd1b77995f6e9180ab2302b"><code>bc6990e</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3579">#3579</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/8be033e24e0c6ddb08a3df72c0a8997d21623a22"><code>8be033e</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3578">#3578</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/ce68c87d9dc6c144b6df578df725470b30cf83d6"><code>ce68c87</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3577">#3577</a>)</li> <li><a href="https://github.com/googleapis/google-api-go-client/commit/de49bb519cab881f74e5b9ba11e263a2b9a4ad2e"><code>de49bb5</code></a> feat(all): auto-regenerate discovery clients (<a href="https://redirect.github.com/googleapis/google-api-go-client/issues/3575">#3575</a>)</li> <li>Additional commits viewable in <a href="https://github.com/googleapis/google-api-go-client/compare/v0.276.0...v0.277.0">compare view</a></li> </ul> </details> <br /> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
2505709475 |
chore: bump axios from 1.15.0 to 1.15.2 in /site (#24965)
Bumps [axios](https://github.com/axios/axios) from 1.15.0 to 1.15.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/axios/axios/releases">axios's releases</a>.</em></p> <blockquote> <h2>v1.15.2</h2> <p>This release delivers prototype-pollution hardening for the Node HTTP adapter, adds an opt-in <code>allowedSocketPaths</code> allowlist to mitigate SSRF via Unix domain sockets, fixes a keep-alive socket memory leak, and ships supply-chain hardening across CI and security docs.</p> <h2>🔒 Security Fixes</h2> <ul> <li><strong>Prototype Pollution Hardening (HTTP Adapter):</strong> Hardened the Node HTTP adapter and <code>resolveConfig</code>/<code>mergeConfig</code>/validator paths to read only own properties and use null-prototype config objects, preventing polluted <code>auth</code>, <code>baseURL</code>, <code>socketPath</code>, <code>beforeRedirect</code>, and <code>insecureHTTPParser</code> from influencing requests. (<strong><a href="https://redirect.github.com/axios/axios/issues/10779">#10779</a></strong>)</li> <li><strong>SSRF via <code>socketPath</code>:</strong> Rejects non-string <code>socketPath</code> values and adds an opt-in <code>allowedSocketPaths</code> config option to restrict permitted Unix domain socket paths, returning <code>AxiosError</code> <code>ERR_BAD_OPTION_VALUE</code> on mismatch. (<strong><a href="https://redirect.github.com/axios/axios/issues/10777">#10777</a></strong>)</li> <li><strong>Supply-chain Hardening:</strong> Added <code>.npmrc</code> with <code>ignore-scripts=true</code>, lockfile lint CI, non-blocking reproducible build diff, scoped CODEOWNERS, expanded <code>SECURITY.md</code>/<code>THREATMODEL.md</code> with provenance verification (<code>npm audit signatures</code>), 60-day resolution policy, and maintainer incident-response runbook. (<strong><a href="https://redirect.github.com/axios/axios/issues/10776">#10776</a></strong>)</li> </ul> <h2>🚀 New Features</h2> <ul> <li><strong><code>allowedSocketPaths</code> Config Option:</strong> New request config option (and TypeScript types) to allowlist Unix domain socket paths used by the Node http adapter; backwards compatible when unset. (<strong><a href="https://redirect.github.com/axios/axios/issues/10777">#10777</a></strong>)</li> </ul> <h2>🐛 Bug Fixes</h2> <ul> <li><strong>Keep-alive Socket Memory Leak:</strong> Installs a single per-socket <code>error</code> listener tracking the active request via <code>kAxiosSocketListener</code>/<code>kAxiosCurrentReq</code>, eliminating per-request listener accumulation, <code>MaxListenersExceededWarning</code>, and linear heap growth under concurrent or long-running keep-alive workloads (fixes <a href="https://redirect.github.com/axios/axios/issues/10780">#10780</a>). (<strong><a href="https://redirect.github.com/axios/axios/issues/10788">#10788</a></strong>)</li> </ul> <h2>🔧 Maintenance & Chores</h2> <ul> <li><strong>Changelog:</strong> Updated <code>CHANGELOG.md</code> with v1.15.1 release notes. (<strong><a href="https://redirect.github.com/axios/axios/issues/10781">#10781</a></strong>)</li> </ul> <p><a href="https://github.com/axios/axios/compare/v1.15.1...v1.15.2">Full Changelog</a></p> <h2>v1.15.1</h2> <p>This release ships a coordinated set of security hardening fixes across headers, body/redirect limits, multipart handling, and XSRF/prototype-pollution vectors, alongside a broad sweep of bug fixes, test migrations, and threat-model documentation updates.</p> <h2>🔒 Security Fixes</h2> <ul> <li><strong>Header Injection Hardening:</strong> Tightened validation and sanitisation across request header construction to close the header-injection attack surface. (<strong><a href="https://redirect.github.com/axios/axios/issues/10749">#10749</a></strong>)</li> <li><strong>CRLF Stripping in Multipart Headers:</strong> Correctly strips CR/LF from multipart header values to prevent injection via field names and filenames. (<strong><a href="https://redirect.github.com/axios/axios/issues/10758">#10758</a></strong>)</li> <li><strong>Prototype Pollution / Auth Bypass:</strong> Replaced unsafe <code>in</code> checks with <code>hasOwnProperty</code> to prevent authentication bypass via prototype pollution on config objects, with additional regression tests. (<strong><a href="https://redirect.github.com/axios/axios/issues/10761">#10761</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10760">#10760</a></strong>)</li> <li><strong><code>withXSRFToken</code> Truthy Bypass:</strong> Short-circuits on any truthy non-boolean value, so an ambiguous config no longer silently leaks the XSRF token cross-origin. (<strong><a href="https://redirect.github.com/axios/axios/issues/10762">#10762</a></strong>)</li> <li><strong><code>maxBodyLength</code> With Zero Redirects:</strong> Enforces <code>maxBodyLength</code> even when <code>maxRedirects</code> is set to <code>0</code>, closing a bypass path for oversized request bodies. (<strong><a href="https://redirect.github.com/axios/axios/issues/10753">#10753</a></strong>)</li> <li><strong>Streamed Response <code>maxContentLength</code> Bypass:</strong> Applies <code>maxContentLength</code> to streamed responses that previously bypassed the cap. (<strong><a href="https://redirect.github.com/axios/axios/issues/10754">#10754</a></strong>)</li> <li><strong>Follow-up CVE Completion:</strong> Completes an earlier incomplete CVE fix to fully close the regression window. (<strong><a href="https://redirect.github.com/axios/axios/issues/10755">#10755</a></strong>)</li> </ul> <h2>🚀 New Features</h2> <ul> <li><strong>AI-Based Docs Translations:</strong> Initial scaffold for AI-assisted translations of the documentation site. (<strong><a href="https://redirect.github.com/axios/axios/issues/10705">#10705</a></strong>)</li> <li><strong><code>Location</code> Request Header Type:</strong> Adds <code>Location</code> to <code>CommonRequestHeadersList</code> for accurate typing of redirect-aware requests. (<strong><a href="https://redirect.github.com/axios/axios/issues/7528">#7528</a></strong>)</li> </ul> <h2>🐛 Bug Fixes</h2> <ul> <li><strong>FormData Handling:</strong> Removes <code>Content-Type</code> when no boundary is present on <code>FormData</code> fetch requests, supports multi-select fields, cancels <code>request.body</code> instead of the source stream on fetch abort, and fixes a recursion bug in form-data serialisation. (<strong><a href="https://redirect.github.com/axios/axios/issues/7314">#7314</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10676">#10676</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10702">#10702</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10726">#10726</a></strong>)</li> <li><strong>HTTP Adapter:</strong> Handles socket-only request errors without leaking keep-alive listeners. (<strong><a href="https://redirect.github.com/axios/axios/issues/10576">#10576</a></strong>)</li> <li><strong>Progress Events:</strong> Clamps <code>loaded</code> to <code>total</code> for computable upload/download progress events. (<strong><a href="https://redirect.github.com/axios/axios/issues/7458">#7458</a></strong>)</li> <li><strong>Types:</strong> Aligns <code>runWhen</code> type with the runtime behaviour in <code>InterceptorManager</code> and makes response header keys case-insensitive. (<strong><a href="https://redirect.github.com/axios/axios/issues/7529">#7529</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10677">#10677</a></strong>)</li> <li><strong><code>buildFullPath</code>:</strong> Uses strict equality in the base/relative URL check. (<strong><a href="https://redirect.github.com/axios/axios/issues/7252">#7252</a></strong>)</li> <li><strong><code>AxiosURLSearchParams</code> Regex:</strong> Improves the regex used for param serialisation to avoid edge-case mismatches. (<strong><a href="https://redirect.github.com/axios/axios/issues/10736">#10736</a></strong>)</li> <li><strong>Resilient Value Parsing:</strong> Parses out header/config values instead of throwing on malformed input. (<strong><a href="https://redirect.github.com/axios/axios/issues/10687">#10687</a></strong>)</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/axios/axios/blob/v1.x/CHANGELOG.md">axios's changelog</a>.</em></p> <blockquote> <h2>v1.15.2 - April 21, 2026</h2> <p>This release delivers prototype-pollution hardening for the Node HTTP adapter, adds an opt-in <code>allowedSocketPaths</code> allowlist to mitigate SSRF via Unix domain sockets, fixes a keep-alive socket memory leak, and ships supply-chain hardening across CI and security docs.</p> <h2>🔒 Security Fixes</h2> <ul> <li><strong>Prototype Pollution Hardening (HTTP Adapter):</strong> Hardened the Node HTTP adapter and <code>resolveConfig</code>/<code>mergeConfig</code>/validator paths to read only own properties and use null-prototype config objects, preventing polluted <code>auth</code>, <code>baseURL</code>, <code>socketPath</code>, <code>beforeRedirect</code>, and <code>insecureHTTPParser</code> from influencing requests. (<strong><a href="https://redirect.github.com/axios/axios/issues/10779">#10779</a></strong>)</li> <li><strong>SSRF via <code>socketPath</code>:</strong> Rejects non-string <code>socketPath</code> values and adds an opt-in <code>allowedSocketPaths</code> config option to restrict permitted Unix domain socket paths, returning <code>AxiosError</code> <code>ERR_BAD_OPTION_VALUE</code> on mismatch. (<strong><a href="https://redirect.github.com/axios/axios/issues/10777">#10777</a></strong>)</li> <li><strong>Supply-chain Hardening:</strong> Added <code>.npmrc</code> with <code>ignore-scripts=true</code>, lockfile lint CI, non-blocking reproducible build diff, scoped CODEOWNERS, expanded <code>SECURITY.md</code>/<code>THREATMODEL.md</code> with provenance verification (<code>npm audit signatures</code>), 60-day resolution policy, and maintainer incident-response runbook. (<strong><a href="https://redirect.github.com/axios/axios/issues/10776">#10776</a></strong>)</li> </ul> <h2>🚀 New Features</h2> <ul> <li><strong><code>allowedSocketPaths</code> Config Option:</strong> New request config option (and TypeScript types) to allowlist Unix domain socket paths used by the Node http adapter; backwards compatible when unset. (<strong><a href="https://redirect.github.com/axios/axios/issues/10777">#10777</a></strong>)</li> </ul> <h2>🐛 Bug Fixes</h2> <ul> <li><strong>Keep-alive Socket Memory Leak:</strong> Installs a single per-socket <code>error</code> listener tracking the active request via <code>kAxiosSocketListener</code>/<code>kAxiosCurrentReq</code>, eliminating per-request listener accumulation, <code>MaxListenersExceededWarning</code>, and linear heap growth under concurrent or long-running keep-alive workloads (fixes <a href="https://redirect.github.com/axios/axios/issues/10780">#10780</a>). (<strong><a href="https://redirect.github.com/axios/axios/issues/10788">#10788</a></strong>)</li> </ul> <h2>🔧 Maintenance & Chores</h2> <ul> <li><strong>Changelog:</strong> Updated <code>CHANGELOG.md</code> with v1.15.1 release notes. (<strong><a href="https://redirect.github.com/axios/axios/issues/10781">#10781</a></strong>)</li> </ul> <p><a href="https://github.com/axios/axios/compare/v1.15.1...v1.15.2">Full Changelog</a></p> <hr /> <h2>v1.15.1 - April 19, 2026</h2> <p>This release ships a coordinated set of security hardening fixes across headers, body/redirect limits, multipart handling, and XSRF/prototype-pollution vectors, alongside a broad sweep of bug fixes, test migrations, and threat-model documentation updates.</p> <h2>🔒 Security Fixes</h2> <ul> <li> <p><strong>Header Injection Hardening:</strong> Tightened validation and sanitisation across request header construction to close the header-injection attack surface. (<strong><a href="https://redirect.github.com/axios/axios/issues/10749">#10749</a></strong>)</p> </li> <li> <p><strong>CRLF Stripping in Multipart Headers:</strong> Correctly strips CR/LF from multipart header values to prevent injection via field names and filenames. (<strong><a href="https://redirect.github.com/axios/axios/issues/10758">#10758</a></strong>)</p> </li> <li> <p><strong>Prototype Pollution / Auth Bypass:</strong> Replaced unsafe <code>in</code> checks with <code>hasOwnProperty</code> to prevent authentication bypass via prototype pollution on config objects, with additional regression tests. (<strong><a href="https://redirect.github.com/axios/axios/issues/10761">#10761</a></strong>, <strong><a href="https://redirect.github.com/axios/axios/issues/10760">#10760</a></strong>)</p> </li> <li> <p><strong><code>withXSRFToken</code> Truthy Bypass:</strong> Short-circuits on any truthy non-boolean value, so an ambiguous config no longer silently leaks the XSRF token cross-origin. (<strong><a href="https://redirect.github.com/axios/axios/issues/10762">#10762</a></strong>)</p> </li> <li> <p><strong><code>maxBodyLength</code> With Zero Redirects:</strong> Enforces <code>maxBodyLength</code> even when <code>maxRedirects</code> is set to <code>0</code>, closing a bypass path for oversized request bodies. (<strong><a href="https://redirect.github.com/axios/axios/issues/10753">#10753</a></strong>)</p> </li> <li> <p><strong>Streamed Response <code>maxContentLength</code> Bypass:</strong> Applies <code>maxContentLength</code> to streamed responses that previously bypassed the cap. (<strong><a href="https://redirect.github.com/axios/axios/issues/10754">#10754</a></strong>)</p> </li> <li> <p><strong>Follow-up CVE Completion:</strong> Completes an earlier incomplete CVE fix to fully close the regression window. (<strong><a href="https://redirect.github.com/axios/axios/issues/10755">#10755</a></strong>)</p> </li> </ul> <h2>🚀 New Features</h2> <ul> <li><strong>AI-Based Docs Translations:</strong> Initial scaffold for AI-assisted translations of the documentation site. (<strong><a href="https://redirect.github.com/axios/axios/issues/10705">#10705</a></strong>)</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/axios/axios/commit/582934382e4e0e0bcb679c628071a4203e93cf57"><code>5829343</code></a> chore(release): prepare release 1.15.2 (<a href="https://redirect.github.com/axios/axios/issues/10789">#10789</a>)</li> <li><a href="https://github.com/axios/axios/commit/4709a48fa2717ba97f43f5432d48ca4e26c2d326"><code>4709a48</code></a> fix: added fix for memory leak in sockets (<a href="https://redirect.github.com/axios/axios/issues/10788">#10788</a>)</li> <li><a href="https://github.com/axios/axios/commit/be3336014e01f9a4fc1f8aef15303cf7daaf58db"><code>be33360</code></a> chore: update changelog (<a href="https://redirect.github.com/axios/axios/issues/10781">#10781</a>)</li> <li><a href="https://github.com/axios/axios/commit/47915144662f2733e6c051bdcb895a8c8f0586aa"><code>4791514</code></a> fix: more header pollutions (<a href="https://redirect.github.com/axios/axios/issues/10779">#10779</a>)</li> <li><a href="https://github.com/axios/axios/commit/6feafcff6c2dbafe206161c5d09e38e1d36af66f"><code>6feafcf</code></a> fix: socket issue (<a href="https://redirect.github.com/axios/axios/issues/10777">#10777</a>)</li> <li><a href="https://github.com/axios/axios/commit/302e2739c602f00e323d4f3f5c79500647633a73"><code>302e273</code></a> docs: update docs, add a couple actions etc (<a href="https://redirect.github.com/axios/axios/issues/10776">#10776</a>)</li> <li><a href="https://github.com/axios/axios/commit/ac42446be51300fe214ba3c6e40cc95f34fd6871"><code>ac42446</code></a> chore(release): prepare release 1.15.1 (<a href="https://redirect.github.com/axios/axios/issues/10767">#10767</a>)</li> <li><a href="https://github.com/axios/axios/commit/908f2206b6bfeff67236784abce85935698ac1d9"><code>908f220</code></a> docs: update threatmodel (<a href="https://redirect.github.com/axios/axios/issues/10765">#10765</a>)</li> <li><a href="https://github.com/axios/axios/commit/f93f8155250c2e066205521eda05ae22983a1f6d"><code>f93f815</code></a> docs: added docs around potential decompressions bomb (<a href="https://redirect.github.com/axios/axios/issues/10763">#10763</a>)</li> <li><a href="https://github.com/axios/axios/commit/1728aa1b15b8857f970611fd8983c06b423fc486"><code>1728aa1</code></a> fix: short-circuits on any truthy non-boolean in withXSRFToken (<a href="https://redirect.github.com/axios/axios/issues/10762">#10762</a>)</li> <li>Additional commits viewable in <a href="https://github.com/axios/axios/compare/v1.15.0...v1.15.2">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) You can disable automated security fix PRs for this repo from the [Security Alerts page](https://github.com/coder/coder/network/alerts). </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
44b0fa4065 |
chore: bump github.com/valyala/fasthttp from 1.70.0 to 1.71.0 (#24958)
Bumps [github.com/valyala/fasthttp](https://github.com/valyala/fasthttp) from 1.70.0 to 1.71.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/valyala/fasthttp/releases">github.com/valyala/fasthttp's releases</a>.</em></p> <blockquote> <h2>v1.71.0</h2> <h2>What's Changed</h2> <ul> <li>feat(client): add RetryIfErrUpstream function to handle upstream information by <a href="https://github.com/mdenushev"><code>@mdenushev</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2176">valyala/fasthttp#2176</a></li> <li>Match net/http sensitive header redirect policy by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2181">valyala/fasthttp#2181</a></li> <li>Sanitize first-line header setters to prevent CRLF injection by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2182">valyala/fasthttp#2182</a></li> <li>server: apply ReadTimeout before first byte with ReduceMemoryUsage by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2183">valyala/fasthttp#2183</a></li> <li>header: reject invalid trailer names by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2188">valyala/fasthttp#2188</a></li> <li>header: reject pre-colon whitespace in request headers by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2187">valyala/fasthttp#2187</a></li> <li>Sanitize redirect Location header to prevent CRLF injection by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2186">valyala/fasthttp#2186</a></li> <li>server: keep hijacked reader out of pool by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2184">valyala/fasthttp#2184</a></li> <li>Sanitize cookie setters to prevent CRLF injection by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2185">valyala/fasthttp#2185</a></li> <li>feat: add ExpectHandler for richer Expect: 100-continue handling by <a href="https://github.com/miretskiy"><code>@miretskiy</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2175">valyala/fasthttp#2175</a></li> <li>http: reject whitespace before chunk extensions by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2193">valyala/fasthttp#2193</a></li> <li>header: reject unsupported response Transfer-Encoding by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2192">valyala/fasthttp#2192</a></li> <li>header: match net/http CL+TE handling by <a href="https://github.com/erikdubbelboer"><code>@erikdubbelboer</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2190">valyala/fasthttp#2190</a></li> <li>chore(deps): bump securego/gosec from 2.25.0 to 2.26.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a>[bot] in <a href="https://redirect.github.com/valyala/fasthttp/pull/2195">valyala/fasthttp#2195</a></li> <li>chore(deps): bump github.com/klauspost/compress from 1.18.5 to 1.18.6 by <a href="https://github.com/dependabot"><code>@dependabot</code></a>[bot] in <a href="https://redirect.github.com/valyala/fasthttp/pull/2196">valyala/fasthttp#2196</a></li> <li>feat(prefork): Enhance prefork management with WatchMaster, CommandProducer, and Windows support by <a href="https://github.com/ReneWerner87"><code>@ReneWerner87</code></a> in <a href="https://redirect.github.com/valyala/fasthttp/pull/2180">valyala/fasthttp#2180</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/miretskiy"><code>@miretskiy</code></a> made their first contribution in <a href="https://redirect.github.com/valyala/fasthttp/pull/2175">valyala/fasthttp#2175</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/valyala/fasthttp/compare/v1.70.0...v1.71.0">https://github.com/valyala/fasthttp/compare/v1.70.0...v1.71.0</a></p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/valyala/fasthttp/commit/e9208ecebf0c102176bb0635043c17333b10401d"><code>e9208ec</code></a> Revert "feat(prefork): graceful shutdown, leak fixes, hook robustness" commit</li> <li><a href="https://github.com/valyala/fasthttp/commit/481e579af9e7d79f9ce27909edd2c42ef9dce173"><code>481e579</code></a> feat(prefork): Enhance prefork management with WatchMaster, CommandProducer, ...</li> <li><a href="https://github.com/valyala/fasthttp/commit/805cd1046567aa8a8b97a8bfe9e7b411621f68b2"><code>805cd10</code></a> Add note on MaxResponseBodySize compatibility with StreamResponseBody</li> <li><a href="https://github.com/valyala/fasthttp/commit/5b5c1be52ca382dcea0ed86931b3f1d2aba9dce6"><code>5b5c1be</code></a> chore(deps): bump github.com/klauspost/compress from 1.18.5 to 1.18.6 (<a href="https://redirect.github.com/valyala/fasthttp/issues/2196">#2196</a>)</li> <li><a href="https://github.com/valyala/fasthttp/commit/d6a99db432025de9ae13051cb42b3e6c3d6568a3"><code>d6a99db</code></a> chore(deps): bump securego/gosec from 2.25.0 to 2.26.1 (<a href="https://redirect.github.com/valyala/fasthttp/issues/2195">#2195</a>)</li> <li><a href="https://github.com/valyala/fasthttp/commit/f36c9009027f81f4fbf304822f96752517b08949"><code>f36c900</code></a> header: match net/http CL+TE handling (<a href="https://redirect.github.com/valyala/fasthttp/issues/2190">#2190</a>)</li> <li><a href="https://github.com/valyala/fasthttp/commit/0b4cede30fa0eb22f9d10999e23ebaabba15e107"><code>0b4cede</code></a> header: reject unsupported response Transfer-Encoding (<a href="https://redirect.github.com/valyala/fasthttp/issues/2192">#2192</a>)</li> <li><a href="https://github.com/valyala/fasthttp/commit/c497746f7d52ab88597dc88310e7f797cc7755aa"><code>c497746</code></a> http: reject whitespace before chunk extensions (<a href="https://redirect.github.com/valyala/fasthttp/issues/2193">#2193</a>)</li> <li><a href="https://github.com/valyala/fasthttp/commit/97b38d3a4884b7c3d8891750a4c752073bc3c152"><code>97b38d3</code></a> server: document SaveMultipartFile path trust requirement</li> <li><a href="https://github.com/valyala/fasthttp/commit/19e4b24955fb0ef764229802378a5e36ae7a822b"><code>19e4b24</code></a> feat: add ExpectHandler for richer Expect: 100-continue handling (<a href="https://redirect.github.com/valyala/fasthttp/issues/2175">#2175</a>)</li> <li>Additional commits viewable in <a href="https://github.com/valyala/fasthttp/compare/v1.70.0...v1.71.0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
a970ffdac8 |
chore: bump github.com/gohugoio/hugo from 0.160.0 to 0.161.1 (#24957)
Bumps [github.com/gohugoio/hugo](https://github.com/gohugoio/hugo) from 0.160.0 to 0.161.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/gohugoio/hugo/releases">github.com/gohugoio/hugo's releases</a>.</em></p> <blockquote> <h2>v0.161.1</h2> <h2>What's Changed</h2> <ul> <li>resources: Honor Retry-After header in resources.GetRemote retries c4eba928 <a href="https://github.com/bep"><code>@bep</code></a> <a href="https://redirect.github.com/gohugoio/hugo/issues/14828">#14828</a></li> <li>warpc: Move to parson.c in <a href="https://github.com/kgabis/parson">https://github.com/kgabis/parson</a> 8b40a96b <a href="https://github.com/bep"><code>@bep</code></a> <a href="https://redirect.github.com/gohugoio/hugo/issues/14823">#14823</a></li> <li>config/security: Add AllowChildProcess to security.node.permissions d65af84d <a href="https://github.com/bep"><code>@bep</code></a> <a href="https://redirect.github.com/gohugoio/hugo/issues/14824">#14824</a></li> <li>config/security: Restrict default http.urls "@" deny to userinfo 454450a6 <a href="https://github.com/bep"><code>@bep</code></a> <a href="https://redirect.github.com/gohugoio/hugo/issues/14825">#14825</a></li> </ul> <h2>v0.161.0</h2> <p>This release contains two security hardening fixes:</p> <ul> <li>We now run the Node tools PostCSS, Babel and TailwindCSS, by default, with the <code>--permission</code> flag with the permissions defined in <a href="https://gohugo.io/configuration/security/">security.node.permissions</a>. This means that you need Node >= 22 installed and that <code>css.TailwindCSS</code> now requires that the Tailwind CSS CLI must be installed as a Node.js package. The <a href="https://github.com/tailwindlabs/tailwindcss/releases/latest">standalone executable</a> is no longer supported</li> <li>We have made the defaults in <a href="https://gohugo.io/configuration/security/#httpurls">security.http.urls</a> more restrictive.</li> </ul> <p>But there are some notable new features, as well:</p> <h2>Nested vars support in css.Build and css.Sass</h2> <p>A practical example in <code>css.Build</code> would be to have something like this in <code>hugo.toml</code>:</p> <pre lang="toml"><code>[params.style] primary = "[#000000](https://github.com/gohugoio/hugo/issues/000000)" background = "#ffffff" [params.style.dark] primary = "#ffffff" background = "[#000000](https://github.com/gohugoio/hugo/issues/000000)" </code></pre> <p>And in the stylesheet:</p> <pre lang="css"><code>@import "hugo:vars"; @import "hugo:vars/dark" (prefers-color-scheme: dark); <p>:root { color-scheme: light dark; } </code></pre></p> <h2>Slice-based permalinks config</h2> <p>The <code>permalinks</code> configuration is now much more flexible (the old setup still works). It uses the same <a href="https://gohugo.io/configuration/cascade/#target">target</a> matchers as in the <code>cascade</code> config, meaning you can now do:</p> <pre lang="yaml"><code>permalinks: - target: kind: page path: "/books/**" </tr></table> </code></pre> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/gohugoio/hugo/commit/ea8f66a7ce988664dcc84c052fc96757042e2e4a"><code>ea8f66a</code></a> releaser: Bump versions for release of 0.161.1</li> <li><a href="https://github.com/gohugoio/hugo/commit/c4eba92863bbb988b23e63af40a22d6661b0ced6"><code>c4eba92</code></a> resources: Honor Retry-After header in resources.GetRemote retries</li> <li><a href="https://github.com/gohugoio/hugo/commit/8b40a96b6e992fbacd8626c24168889f50152808"><code>8b40a96</code></a> warpc: Move to parson.c in <a href="https://github.com/kgabis/parson">https://github.com/kgabis/parson</a></li> <li><a href="https://github.com/gohugoio/hugo/commit/d65af84d1572326057a9a55e26beb0cee784698a"><code>d65af84</code></a> config/security: Add AllowChildProcess to security.node.permissions</li> <li><a href="https://github.com/gohugoio/hugo/commit/454450a647111e5e0b41af595b310f3062c5630e"><code>454450a</code></a> config/security: Restrict default http.urls "@" deny to userinfo</li> <li><a href="https://github.com/gohugoio/hugo/commit/2bfcc6b9941724cd1d0b490583e89413d7a66979"><code>2bfcc6b</code></a> releaser: Prepare repository for 0.162.0-DEV</li> <li><a href="https://github.com/gohugoio/hugo/commit/98d396c16a07b51df06e7673d817a3880da6218d"><code>98d396c</code></a> releaser: Bump versions for release of 0.161.0</li> <li><a href="https://github.com/gohugoio/hugo/commit/d4ae662d598db81d239a291bc26336be5fec6893"><code>d4ae662</code></a> build(deps): bump github.com/getkin/kin-openapi from 0.135.0 to 0.137.0</li> <li><a href="https://github.com/gohugoio/hugo/commit/9ede5fb9e0304d3eb193b3c1a9214c735f05db21"><code>9ede5fb</code></a> build(deps): bump github.com/mattn/go-isatty from 0.0.21 to 0.0.22</li> <li><a href="https://github.com/gohugoio/hugo/commit/833a878eef4fce2bbabb05dcbb8a7e31f93aadda"><code>833a878</code></a> build(deps): bump github.com/tdewolff/minify/v2 from 2.24.12 to 2.24.13</li> <li>Additional commits viewable in <a href="https://github.com/gohugoio/hugo/compare/v0.160.0...v0.161.1">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
fc04f0d71e |
chore: bump github.com/fsnotify/fsnotify from 1.9.0 to 1.10.1 (#24962)
Bumps [github.com/fsnotify/fsnotify](https://github.com/fsnotify/fsnotify) from 1.9.0 to 1.10.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/fsnotify/fsnotify/releases">github.com/fsnotify/fsnotify's releases</a>.</em></p> <blockquote> <h2>v1.10.1</h2> <h3>Changes and fixes</h3> <ul> <li> <p>inotify: don't remove sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/754">#754</a>)</p> </li> <li> <p>inotify, windows: don't rename sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/755">#755</a>)</p> </li> </ul> <p><a href="https://redirect.github.com/fsnotify/fsnotify/issues/754">#754</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/754">fsnotify/fsnotify#754</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/755">#755</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/755">fsnotify/fsnotify#755</a></p> <h2>v1.10.0</h2> <p>This version of fsnotify needs Go 1.23.</p> <h3>Changes and fixes</h3> <ul> <li> <p>inotify: improve initialization error message (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/731">#731</a>)</p> </li> <li> <p>inotify: send Rename event if recursive watch is renamed (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/696">#696</a>)</p> </li> <li> <p>inotify: avoid copying event buffers when reading names (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/741">#741</a>)</p> </li> <li> <p>kqueue: skip dangling symlinks (ENOENT) in watchDirectoryFiles, so a bad entry no longer aborts Watcher.Add for the whole directory (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/748">#748</a>)</p> </li> <li> <p>kqueue: drop watches directly in Close() to fix a file descriptor leak when recycling watchers (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/740">#740</a>)</p> </li> <li> <p>windows: fix nil pointer dereference in remWatch (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/736">#736</a>)</p> </li> <li> <p>windows: lock watch field updates against concurrent WatchList to fix a race introduced in v1.9.0 (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/709">#709</a>, <a href="https://redirect.github.com/fsnotify/fsnotify/issues/749">#749</a>)</p> </li> </ul> <p><a href="https://redirect.github.com/fsnotify/fsnotify/issues/696">#696</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/696">fsnotify/fsnotify#696</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/709">#709</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/709">fsnotify/fsnotify#709</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/731">#731</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/731">fsnotify/fsnotify#731</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/736">#736</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/736">fsnotify/fsnotify#736</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/740">#740</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/740">fsnotify/fsnotify#740</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/741">#741</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/741">fsnotify/fsnotify#741</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/748">#748</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/748">fsnotify/fsnotify#748</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/749">#749</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/749">fsnotify/fsnotify#749</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/fsnotify/fsnotify/blob/main/CHANGELOG.md">github.com/fsnotify/fsnotify's changelog</a>.</em></p> <blockquote> <h2>1.10.1 2026-05-04</h2> <h3>Changes and fixes</h3> <ul> <li> <p>inotify: don't remove sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/754">#754</a>)</p> </li> <li> <p>inotify, windows: don't rename sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/755">#755</a>)</p> </li> </ul> <p><a href="https://redirect.github.com/fsnotify/fsnotify/issues/754">#754</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/754">fsnotify/fsnotify#754</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/755">#755</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/755">fsnotify/fsnotify#755</a></p> <h2>1.10.0 2026-04-30</h2> <p>This version of fsnotify needs Go 1.23.</p> <h3>Changes and fixes</h3> <ul> <li> <p>inotify: improve initialization error message (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/731">#731</a>)</p> </li> <li> <p>inotify: send Rename event if recursive watch is renamed (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/696">#696</a>)</p> </li> <li> <p>inotify: avoid copying event buffers when reading names (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/741">#741</a>)</p> </li> <li> <p>kqueue: skip dangling symlinks (ENOENT) in watchDirectoryFiles, so a bad entry no longer aborts Watcher.Add for the whole directory (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/748">#748</a>)</p> </li> <li> <p>kqueue: drop watches directly in Close() to fix a file descriptor leak when recycling watchers (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/740">#740</a>)</p> </li> <li> <p>windows: fix nil pointer dereference in remWatch (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/736">#736</a>)</p> </li> <li> <p>windows: lock watch field updates against concurrent WatchList to fix a race introduced in v1.9.0 (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/709">#709</a>, <a href="https://redirect.github.com/fsnotify/fsnotify/issues/749">#749</a>)</p> </li> </ul> <p><a href="https://redirect.github.com/fsnotify/fsnotify/issues/696">#696</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/696">fsnotify/fsnotify#696</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/709">#709</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/709">fsnotify/fsnotify#709</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/731">#731</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/731">fsnotify/fsnotify#731</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/736">#736</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/736">fsnotify/fsnotify#736</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/740">#740</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/740">fsnotify/fsnotify#740</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/741">#741</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/741">fsnotify/fsnotify#741</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/748">#748</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/748">fsnotify/fsnotify#748</a> <a href="https://redirect.github.com/fsnotify/fsnotify/issues/749">#749</a>: <a href="https://redirect.github.com/fsnotify/fsnotify/pull/749">fsnotify/fsnotify#749</a></p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/fsnotify/fsnotify/commit/76b01a6e8f502187fecedea8b025e79e5a86085c"><code>76b01a6</code></a> Release 1.10.1</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/fec150b807510e54e5b25def4b6e5fb001b4898c"><code>fec150b</code></a> Update changelog</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/162b4216ab8f92ecd26425530bee198972c9b3cb"><code>162b421</code></a> inotify, windows: don't rename sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/755">#755</a>)</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/224257f23b2f3a96509b316c5cead71dd4a9099a"><code>224257f</code></a> inotify: don't remove sibling watches sharing a path prefix (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/754">#754</a>)</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/e0c956c0ccaf51562fee30ef5c055c74e6ae2104"><code>e0c956c</code></a> windows: document directory Write events and stabilize tests (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/745">#745</a>)</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/8d01d7b9cbe0199e4a1e60fbd965fb05dbb42123"><code>8d01d7b</code></a> Release 1.10.0</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/602284e4a8cadd488d7a5fa07c48462dfac25108"><code>602284e</code></a> Update changelog</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/7f03e59f9659552d8a084e03024cb9b983748ed7"><code>7f03e59</code></a> kqueue: skip ENOENT entries in watchDirectoryFiles (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/748">#748</a>)</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/dab9dde2fc9ba4d0c1076318f81cabcc8fdb2ec9"><code>dab9dde</code></a> windows: lock watch field updates against concurrent WatchList (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/709">#709</a>) (<a href="https://redirect.github.com/fsnotify/fsnotify/issues/749">#749</a>)</li> <li><a href="https://github.com/fsnotify/fsnotify/commit/eadf267ce152b5e62d48cc2c13bb08bd4062b6c7"><code>eadf267</code></a> kqueue: drop watches directly in Close() instead of going through remove() (#...</li> <li>Additional commits viewable in <a href="https://github.com/fsnotify/fsnotify/compare/v1.9.0...v1.10.1">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
Michael Suchacz
|
1e7874c2c1 |
feat(site): add personal model override settings UI (#24748)
Adds the UI for personal chat model overrides for root chats, General subagents, and Explore subagents. Backend support landed in #24715, and this PR now targets `main`. ## Summary - Add the admin switch for enabling user personal model overrides. - Add the user `Agents` settings page at `/agents/settings/user-agents`. - Use one dropdown per context with pinned chat default and deployment default options. - Show the resolved deployment default model in personal settings when available. - Teach root chat creation to honor saved root preferences without replacing explicit user selections. - Add shared unavailable and malformed override alerts, select separator support, and Storybook coverage. ## Testing - `pnpm --dir site lint:types` - `pnpm --dir site check` - `pnpm --dir site test:storybook src/pages/AgentsPage/AgentSettingsUserAgentsPageView.stories.tsx src/pages/AgentsPage/components/AdminPersonalModelOverridesSettings.stories.tsx src/pages/AgentsPage/components/AgentCreateForm.stories.tsx src/pages/AgentsPage/components/Sidebar/AgentsSidebar.stories.tsx` > Mux is working on behalf of Mike. |
||
|
Mathias Fredriksson
|
0c5a25c018 |
fix(site): deduplicate expired-attachment probes for repeated file IDs (#24760)
When multiple RemoteImageBlock components share a file ID, Chromium fires native error events on all of them before the first probe's fetch resolves. Each handler independently checked hasExpired(), saw false, and started its own probe. FileProbeContext (renamed from ExpiredFileIdsContext) now coordinates probes across blocks for the same file ID: - A ref-based pending set (isPending/markPending/clearPending) gates duplicate probes. A ref is used so the second handler can read it synchronously before React re-renders. - Resolved outcomes are stored in context state (probeResults map) so sibling blocks re-render with the full result, including API error detail for tooltips. - Context writes (markExpired, setProbeResult) run above the per-instance abort-controller guard so siblings receive the result even if the probing block unmounts mid-flight. |
||
|
Sas Swart
|
1ba7139f21 |
feat: add session correlation fields to BoundaryLog proto (#24809)
1 of 9 [next >>](https://github.com/coder/coder/pull/24811) RFC: [Bridge ↔ Boundaries Correlation RFC](https://www.notion.so/Bridge-Boundaries-Correlation-313d579be59281f3b4efdbfd6896775a) Adds three new proto fields for boundary session correlation. **`ReportBoundaryLogsRequest`** - `session_id` (string, field 2) — UUID generated by boundary at startup, shared across all batches from a single run. - `confined_process` (string, field 3) — name of the confined process (e.g. `claude-code`, `codex`, `copilot`). **`BoundaryLog`** - `sequence_number` (uint64, field 4) — monotonically increasing counter per session, primary ordering key when boundary is in use. `BoundaryLog.time` already existed at field 2; no change needed there. API version bumped to v2.9. No behaviour change in coderd or the agent. This is a pure schema bump that the boundary repo will consume in its own stack. > Generated by Coder Agents |
||
|
dependabot[bot]
|
e8e9e51036 |
chore: bump the coder-modules group across 3 directories with 1 update (#24953)
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore <dependency name> major version` will close this group update PR and stop Dependabot creating any more for the specific dependency's major version (unless you unignore this specific dependency's major version or upgrade to it yourself) - `@dependabot ignore <dependency name> minor version` will close this group update PR and stop Dependabot creating any more for the specific dependency's minor version (unless you unignore this specific dependency's minor version or upgrade to it yourself) - `@dependabot ignore <dependency name>` will close this group update PR and stop Dependabot creating any more for the specific dependency (unless you unignore this specific dependency or upgrade to it yourself) - `@dependabot unignore <dependency name>` will remove all of the ignore conditions of the specified dependency - `@dependabot unignore <dependency name> <ignore condition>` will remove the ignore condition of the specified dependency and ignore conditions </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
Ethan
|
4751416b29 |
fix!: persist structured chat errors (#24919)
**Breaking change for changelog:**

> `codersdk.Chat.last_error` now returns a structured `ChatError` object
(`{message, kind, provider, retryable, status_code, detail}`) instead of
a plain string. The chats API is experimental
(`/api/experimental/chats`), so this ships without a deprecation cycle;
consumers reading `chat.last_error` as a string must update to read
`chat.last_error.message`. SDK/generated TypeScript terminal error
payloads now use the single `ChatError` type; the live stream error
payload type is renamed from `ChatStreamError` to `ChatError`.

Persisted chat errors now carry the same provider-specific detail (kind,
provider, retryable, HTTP status, optional detail) as the live stream,
so refreshing a failed chat rehydrates with the full structured error
instead of a one-line headline.

Existing rows are migrated in place: legacy text errors are wrapped into
`{message, kind: "generic"}` so already-errored chats still render, and
rows with `last_error IS NULL` stay NULL. Internally, persisted fallback
decoding now reuses the existing `chaterror.KindGeneric` constant, with
no JSON value change.

Closes CODAGT-239
|
||
|
Ethan
|
7e01edeb8e |
fix: align chat attachment picker with allowed file types (#24917)
The agent chat composer only advertised image uploads to the OS file picker and filtered drag-and-drop and paste events to `image/*`, even though the backend accepts text, CSV, JSON, PDF, and a narrower set of image types. Move the allowed chat attachment media types into `codersdk` so the frontend picker and backend enforcement share one source of truth. Use the generated TypeScript list to drive the file input `accept` attribute and the drag-and-drop and paste filters, while adding common text extensions so platforms without MIME registrations still surface those files in the picker. |
||
|
Michael Suchacz
|
632dcdb63a | feat: add personal chat model overrides (#24715) | ||
|
Michael Suchacz
|
43aa0498d6 | feat(site): warn when viewing another user's chat (#24941) | ||
|
Atif Ali
|
fad69df710 | fix: correct SCIM Swagger try it out URLs (#24779) | ||
|
Kyle Carberry
|
f0fd2111fd |
feat(site/src/pages/AgentsPage): render markdown attachments in preview popup (#24936)
Markdown attachments on `/agents` now render through the same `Response` component used for chat messages instead of falling back to a monospaced `<pre>` block. The popup detects markdown via an explicit `text/markdown` media type and falls back to the `.md`/`.markdown` filename extension when no media type is available. `PreviewTextAttachment` and `TextPreviewDialog` gain an optional `mediaType` so that callers (`AttachmentBlock` for already-sent messages and `AttachmentPreview` for live drafts) can plumb the upload metadata through. Plain `.txt` and unrecognized text attachments keep the existing monospaced rendering. ## Demo  ## Screenshots | Markdown rendering | Plain text rendering | | --- | --- | |  |  | Light theme also verified:  <details> <summary>Coverage details</summary> New stories in `TextPreviewDialog.stories.tsx` cover: - `MarkdownByExtension` — `.md` filename, headings/lists/tables/fenced code render natively. - `MarkdownByMediaType` — explicit `text/markdown` mediaType wins even without a `.md` suffix. - `MarkdownProseOnly` — inline `**bold**`, `_italic_`, and `` `code` `` render via streamdown. - `PlainTextStaysMonospaced` — `.txt` content stays inside `<pre>` so existing previews don't regress. Manual verification (desktop, Chromium, dark + light): all four stories above plus the existing `Default`, `LongContent`, and `NoFileName` stories pass. </details> _Coder Agents generated PR._ |
||
|
dependabot[bot]
|
63412012b6 |
chore: bump lodash from 4.17.21 to 4.18.1 in /site (#24940)
Bumps [lodash](https://github.com/lodash/lodash) from 4.17.21 to 4.18.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lodash/lodash/releases">lodash's releases</a>.</em></p> <blockquote> <h2>4.18.1</h2> <h2>Bugs</h2> <p>Fixes a <code>ReferenceError</code> issue in <code>lodash</code> <code>lodash-es</code> <code>lodash-amd</code> and <code>lodash.template</code> when using the <code>template</code> and <code>fromPairs</code> functions from the modular builds. See <a href="https://redirect.github.com/lodash/lodash/issues/6167#issuecomment-4165269769">lodash/lodash#6167</a></p> <p>These defects were related to how lodash distributions are built from the main branch using <a href="https://github.com/lodash-archive/lodash-cli">https://github.com/lodash-archive/lodash-cli</a>. When internal dependencies change inside lodash functions, equivalent updates need to be made to a mapping in the lodash-cli. (hey, it was ahead of its time once upon a time!). We know this, but we missed it in the last release. It's the kind of thing that passes in CI, but fails bc the build is not the same thing you tested.</p> <p>There is no diff on main for this, but you can see the diffs for each of the npm packages on their respective branches:</p> <ul> <li><code>lodash</code>: <a href="https://github.com/lodash/lodash/compare/4.18.0-npm...4.18.1-npm">https://github.com/lodash/lodash/compare/4.18.0-npm...4.18.1-npm</a></li> <li><code>lodash-es</code>: <a href="https://github.com/lodash/lodash/compare/4.18.0-es...4.18.1-es">https://github.com/lodash/lodash/compare/4.18.0-es...4.18.1-es</a></li> <li><code>lodash-amd</code>: <a href="https://github.com/lodash/lodash/compare/4.18.0-amd...4.18.1-amd">https://github.com/lodash/lodash/compare/4.18.0-amd...4.18.1-amd</a></li> <li><code>lodash.template</code><a href="https://github.com/lodash/lodash/compare/4.18.0-npm-packages...4.18.1-npm-packages">https://github.com/lodash/lodash/compare/4.18.0-npm-packages...4.18.1-npm-packages</a></li> </ul> <h2>4.18.0</h2> <h2>v4.18.0</h2> <p><strong>Full Changelog</strong>: <a href="https://github.com/lodash/lodash/compare/4.17.23...4.18.0">https://github.com/lodash/lodash/compare/4.17.23...4.18.0</a></p> <h3>Security</h3> <p><strong><code>_.unset</code> / <code>_.omit</code></strong>: Fixed prototype pollution via <code>constructor</code>/<code>prototype</code> path traversal (<a href="https://github.com/lodash/lodash/security/advisories/GHSA-f23m-r3pf-42rh">GHSA-f23m-r3pf-42rh</a>, <a href="https://github.com/lodash/lodash/commit/fe8d32eda854377349a4f922ab7655c8e5df9a0b">fe8d32e</a>). Previously, array-wrapped path segments and primitive roots could bypass the existing guards, allowing deletion of properties from built-in prototypes. Now <code>constructor</code> and <code>prototype</code> are blocked unconditionally as non-terminal path keys, matching <code>baseSet</code>. Calls that previously returned <code>true</code> and deleted the property now return <code>false</code> and leave the target untouched.</p> <p><strong><code>_.template</code></strong>: Fixed code injection via <code>imports</code> keys (<a href="https://github.com/lodash/lodash/security/advisories/GHSA-r5fr-rjxr-66jc">GHSA-r5fr-rjxr-66jc</a>, CVE-2026-4800, <a href="https://github.com/lodash/lodash/commit/879aaa93132d78c2f8d20c60279da9f8b21576d6">879aaa9</a>). Fixes an incomplete patch for CVE-2021-23337. The <code>variable</code> option was validated against <code>reForbiddenIdentifierChars</code> but <code>importsKeys</code> was left unguarded, allowing code injection via the same <code>Function()</code> constructor sink. <code>imports</code> keys containing forbidden identifier characters now throw <code>"Invalid imports option passed into _.template"</code>.</p> <h3>Docs</h3> <ul> <li>Add security notice for <code>_.template</code> in threat model and API docs (<a href="https://redirect.github.com/lodash/lodash/pull/6099">#6099</a>)</li> <li>Document <code>lower > upper</code> behavior in <code>_.random</code> (<a href="https://redirect.github.com/lodash/lodash/pull/6115">#6115</a>)</li> <li>Fix quotes in <code>_.compact</code> jsdoc (<a href="https://redirect.github.com/lodash/lodash/pull/6090">#6090</a>)</li> </ul> <h3><code>lodash.*</code> modular packages</h3> <p><a href="https://redirect.github.com/lodash/lodash/pull/6157">Diff</a></p> <p>We have also regenerated and published a select number of the <code>lodash.*</code> modular packages.</p> <p>These modular packages had fallen out of sync significantly from the minor/patch updates to lodash. Specifically, we have brought the following packages up to parity w/ the latest lodash release because they have had CVEs on them in the past:</p> <ul> <li><a href="https://www.npmjs.com/package/lodash.orderby">lodash.orderby</a></li> <li><a href="https://www.npmjs.com/package/lodash.tonumber">lodash.tonumber</a></li> <li><a href="https://www.npmjs.com/package/lodash.trim">lodash.trim</a></li> <li><a href="https://www.npmjs.com/package/lodash.trimend">lodash.trimend</a></li> <li><a href="https://www.npmjs.com/package/lodash.sortedindexby">lodash.sortedindexby</a></li> <li><a href="https://www.npmjs.com/package/lodash.zipobjectdeep">lodash.zipobjectdeep</a></li> <li><a href="https://www.npmjs.com/package/lodash.unset">lodash.unset</a></li> <li><a href="https://www.npmjs.com/package/lodash.omit">lodash.omit</a></li> <li><a href="https://www.npmjs.com/package/lodash.template">lodash.template</a></li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lodash/lodash/commit/cb0b9b9212521c08e3eafe7c8cb0af1b42b6649e"><code>cb0b9b9</code></a> release(patch): bump main to 4.18.1 (<a href="https://redirect.github.com/lodash/lodash/issues/6177">#6177</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/75535f57883b7225adb96de1cfc1cd4169cfcb51"><code>75535f5</code></a> chore: prune stale advisory refs (<a href="https://redirect.github.com/lodash/lodash/issues/6170">#6170</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/62e91bc6a39c98d85b9ada8c44d40593deaf82a4"><code>62e91bc</code></a> docs: remove n_ Node.js < 6 REPL note from README (<a href="https://redirect.github.com/lodash/lodash/issues/6165">#6165</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/59be2de61f8aa9461c7856533b51d31b7d8babc4"><code>59be2de</code></a> release(minor): bump to 4.18.0 (<a href="https://redirect.github.com/lodash/lodash/issues/6161">#6161</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/af634573030f979194871da7c68f79420992f53d"><code>af63457</code></a> fix: broken tests for _.template 879aaa9</li> <li><a href="https://github.com/lodash/lodash/commit/1073a7693e1727e0cf3641e5f71f75ddcf8de7c0"><code>1073a76</code></a> fix: linting issues</li> <li><a href="https://github.com/lodash/lodash/commit/879aaa93132d78c2f8d20c60279da9f8b21576d6"><code>879aaa9</code></a> fix: validate imports keys in _.template</li> <li><a href="https://github.com/lodash/lodash/commit/fe8d32eda854377349a4f922ab7655c8e5df9a0b"><code>fe8d32e</code></a> fix: block prototype pollution in baseUnset via constructor/prototype traversal</li> <li><a href="https://github.com/lodash/lodash/commit/18ba0a32f42fd02117f096b032f89c984173462d"><code>18ba0a3</code></a> refactor(fromPairs): use baseAssignValue for consistent assignment (<a href="https://redirect.github.com/lodash/lodash/issues/6153">#6153</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/b8190803d48d60b8c80ad45d39125f32fa618cb2"><code>b819080</code></a> ci: add dist sync validation workflow (<a href="https://redirect.github.com/lodash/lodash/issues/6137">#6137</a>)</li> <li>Additional commits viewable in <a href="https://github.com/lodash/lodash/compare/4.17.21...4.18.1">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) You can disable automated security fix PRs for this repo from the [Security Alerts page](https://github.com/coder/coder/network/alerts). </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
Steven Masley
|
d4f913a4cf |
chore: bump coder/serpent to accept empty env vars (#24926)
Non-zero default values can now be set to `""` with env vars. Eg: `--log-human="" --log-json="/dev/stderr"` |
||
|
Michael Suchacz
|
0bb09935bc |
feat: add computer-use provider selection for AI agents (#24772)
Adds a deployment-wide setting to select the computer-use provider (Anthropic or OpenAI) for AI agents, plus the OpenAI computer-use runner needed to honor that selection. The setting is stored in `site_configs` under `agents_computer_use_provider`, defaults to Anthropic when unset, and is exposed via experimental GET/PUT endpoints under `/api/experimental/chats/config/computer-use-provider`. The chatd computer-use tool now dispatches to either `runAnthropicComputerUse` or `runOpenAIComputerUse` based on the resolved provider, with provider-specific result metadata for OpenAI screenshots. Frontend adds a provider dropdown to the Agents Experiments settings page nested under the virtual desktop toggle, with disabled state handling while virtual desktop is off and skeleton loaders while config queries are in flight. Hugo and Codex review follow-up: - Uses shared provider validation and clearer computer-use constant names. - Removes stale OpenAI pending-safety-checks commentary. - Documents why provider result metadata is needed for OpenAI screenshots. - Keeps the computer-use subagent visible when provider credentials are missing, then returns a clear spawn-time configuration error. - Uses OpenAI's recommended 1600x900 screenshot geometry to preserve the native 16:9 aspect ratio. - Moves OpenAI-specific computer-use helpers into `coderd/x/chatd/chatopenai/computeruse` after rebasing onto the provider package refactor in `main`. - Converts OpenAI pixel scroll deltas to Coder desktop wheel-click amounts. - Preserves OpenAI pointer modifiers with key down/up desktop actions and rejects unsupported non-left double-click buttons explicitly. - Maps OpenAI back/forward side-button clicks to browser navigation key actions. - Defaults omitted OpenAI click buttons to left-click. - Retries mouse release cleanup if the final OpenAI drag release fails. - Keeps computer-use subagent availability messages stable when provider config cannot be loaded, while logging the backend error. - Releases remaining OpenAI modifier keys if a synthetic key-up cleanup action fails. - Updates Storybook interaction stories so provider snapshots show the selected final provider. > Mux updated this PR description on behalf of Mike. |
||
|
|
da6e708bd2 |
fix(coderd/externalauth): detect concurrent refresh race to prevent cache poisoning (#24228)
<!-- If you have used AI to produce some or all of this PR, please ensure you have read our [AI Contribution guidelines](https://coder.com/docs/about/contributing/AI_CONTRIBUTING) before submitting. --> Fixes https://github.com/coder/coder/issues/17069 Builds on #24332 and #24334 which addressed token persistence and rate limit handling. ## Problem When multiple concurrent requests race to refresh an expiring external auth token, providers with single-use refresh tokens (e.g., GitHub Apps) reject all but the first refresh attempt with `bad_refresh_token`. The losing request caches this transient error in the `oauth_refresh_failure_reason` database column and clears the refresh token, blocking all subsequent refresh attempts until the user manually re-authenticates. This is common for users with multiple terminals, IDE connections, or workspaces open, all of which poll the external auth endpoint and trigger concurrent refreshes when the token nears expiry. Database analysis showed 5 of 7 affected users failed within 5-10 seconds of token expiry, matching the Go oauth2 library's `expiryDelta` window. ## Fix Before caching a `bad_refresh_token` failure, re-read the external auth link from the database. If the refresh token has changed (indicating a concurrent caller already refreshed successfully), return the winner's updated link instead of writing a failure. An empty-string guard ensures a token cleared by another loser isn't mistaken for a winner's successful refresh. Co-authored-by: Claude Opus 4.6 (1M context) <noreply@anthropic.com> Co-authored-by: Garrett Delfosse <garrett@coder.com> |
||
|
Kyle Carberry
|
1ecdad689b |
fix(site/src/pages/AgentsPage): restore sticky user message pinning after react-infinite-scroll-component refactor (#24937)
Restores the sticky user message pinning behavior in the Agents chat that regressed after #24687 swapped the chat scroll container for `react-infinite-scroll-component`. ## Root cause `react-infinite-scroll-component` renders two wrapper divs between the `.overflow-y-auto` scroller and the rendered messages, and its inner wrapper hard-codes `overflow: auto` in its inline style. With the new layout, `position: sticky` on a user message resolved against that inner wrapper rather than the real scroller, so the message scrolled out with its sentinel and the existing fade/clip overlay never engaged. ## Fix Force both InfiniteScroll wrappers to `display: contents` so they no longer participate in layout. The user message's nearest scrolling ancestor is once again the `.overflow-y-auto` element, and `position: sticky` anchors to the scroll container as it did before #24687. The outer wrapper is reached via the Tailwind arbitrary selector `[&>[class$=outerdiv]]:contents` because the library only exposes `style` for the inner wrapper. The inverse infinite-scroll behavior is preserved: the scroller itself stays `flex-col-reverse`, so it remains bottom-anchored and the library's load-more sentinel still lands at the visual top of the content stack. Also drops the dead `overflow-y-auto` class on the floating scroll-to-bottom button wrapper noted in the bug report. ## Test coverage Adds `StickyUserMessagePinsOnScroll` to `AgentChatPageView.stories.tsx`. With a 40-message conversation it walks the user-message sentinels in reverse DOM order to find the one currently pinned (the latest sentinel above the scroller's top edge) and asserts the matching sticky container is anchored within a few pixels of that edge. Without the fix the container ends up hundreds of pixels above the scroller because `position: sticky` silently no-ops. The existing structural `StickyUserMessageStructure` story in `ConversationTimeline.stories.tsx` continues to pass unchanged. <details> <summary>Verification</summary> ```sh pnpm exec tsc -p . # 0 errors pnpm run lint:check # passes pnpm exec vitest run --project=unit # 2303 passed pnpm exec vitest run --project=storybook \ src/pages/AgentsPage/AgentChatPage.stories.tsx \ src/pages/AgentsPage/AgentChatPageView.stories.tsx \ src/pages/AgentsPage/components/ChatConversation/ConversationTimeline.stories.tsx # 90 passed ``` Confirmed the new story fails on `main` (sticky container at the sentinel's position instead of the scroller top) and passes with the fix applied. </details> --- Generated by Coder Agents. |
||
|
Kayla はな
|
162acaf8bf |
feat: update UsersPage role editing to match new designs (#24857)
|
||
|
Matt Vollmer
|
5612bb81cb |
docs(docs/ai-coder): replace Coder Tasks references with Coder Agents (#24929)
Updates `docs/ai-coder/index.md`, `docs/ai-coder/best-practices.md`, and `docs/ai-coder/ai-governance.md` to point readers at Coder Agents and the AI Governance Add-On instead of Coder Tasks and Agent Firewall (CODAGT-157). ## Changes - `docs/ai-coder/index.md`: - Rename `## Agents with Coder Tasks` to `## Coder Agents`. Drop the Devin / ChatGPT Codex name-drops and the Tasks pitch. New copy points at `./agents/index.md`, names the agent loop in the control plane, and notes that workspaces can be completely network isolated. Image swapped from `tasks-ui.png` to `agents-hero-image.png` (the hero shot added in #24915). - Replace the `## Secure Your Workflows with Agent Firewall` section with `## Govern AI activity with the AI Governance Add-On`. The new section opens with adoption-first framing (visibility, guardrails, cost) and links to `./ai-governance.md`, with bulleted callouts for AI Gateway, Agent Firewall, and the expanded Agent Workspace Build allowance the add-on bundles. - `docs/ai-coder/best-practices.md`: - In the use-case table, swap `[Tasks](./tasks.md)` to `[Coder Agents](./agents/index.md)` for the developer-led-investigation and prototyping rows, and swap the "Tasks API *(in development)*" cell to `[Coder Agents API](./agents/chats-api.md)` for the background-jobs row. Retitle the Security section link from "securing agents with Coder Tasks" to "securing AI agents" since `security.md` does not actually mention Tasks. Re-ran `markdown-table-formatter` to repad column widths. - In `## Provide Agents with Proper Context`, add a paragraph describing how context is provided in Coder Agents (admin-configured system prompts, centrally registered MCP servers, and skills shipped from repos or templates under `.agents/skills/`), with a transition line clarifying that the existing Memory and Tools subsections cover BYO-agent patterns. - `docs/ai-coder/ai-governance.md`: drop the "Additional Tasks Use (via Agent Workspace Builds)" bullet from the intro feature list and the "Expanding the use of Coder Tasks for AI-driven background work" bullet from the audience list. The `## How Coder Tasks usage is measured` section and the rest of the Tasks-related prose on this page are intentionally left for a follow-up PR. ## Notes for the reviewer - The `[Coder Agents API](./agents/chats-api.md)` link in `best-practices.md` will need to be retargeted if #24830 (which replaces `agents/chats-api.md` with auto-generated `reference/api/chats.md`) lands first. - This is the first slice of the Tasks-references audit. Remaining files (`tasks-core-principles.md`, `tasks-lifecycle.md`, `tasks-migration.md`, `cli.md`, `github-to-tasks.md`, `agent-compatibility.md`, the rest of `ai-governance.md`, `custom-agents.md`, `ai-gateway/clients/claude-code.md`, `manifest.json`, `reference/api/tasks.md`, the `task*` CLI references, the ESR upgrade guide, `feature-stages.md`, `workspace-scheduling.md`, `shared-workspaces.md`) will land in follow-up PRs against the same Linear ticket. Open PRs #24831, #24833, and #24841 cover separate slices and do not touch any file in this PR. - Validation: `markdownlint-cli2`, `markdown-table-formatter`, `scripts/check_emdash.sh`, and `make pre-commit-light` all pass. PR generated with Coder Agents. |
||
|
Ben Potter
|
f6eccbab23 |
feat(site/src): add ports submenu to WorkspacePill in agents chat (#24887)
Adds a **Ports (n) >** submenu item to the `WorkspacePill` dropdown shown in the `/agents` chat UI when a workspace is attached, sitting alongside VS Code, Terminal, and other app items. The submenu shows a **Listening Ports** section with clickable port links that open in a new tab, a **Shared Ports** section with sharing-level icons when any ports are shared, and a **Manage sharing** footer link to the workspace detail page. Port data is fetched on a 5s polling interval while the dropdown is open and only when the agent is connected. The trigger is disabled when the workspace is not running. Also adds `DropdownMenuSub`, `DropdownMenuSubTrigger`, and `DropdownMenuSubContent` to the shared `DropdownMenu` component for use here and future consumers.  <details> <summary>Implementation notes</summary> - `host` for port-forward URL construction comes from `useProxy().proxy.preferredWildcardHostname`, the same source used by `PortForwardButton` on the workspace detail page. - Port queries are gated on `isOpen && agent.status === "connected"` so no requests fire when the dropdown is closed or the agent is disconnected. - Shared ports that overlap with listening ports are deduplicated: they only appear in the Shared section. - Port sharing controls (create/update/delete) are intentionally excluded to keep the agents toolbar lightweight; the "Manage sharing" link surfaces the workspace page for that. - The port count badge on the trigger (`Ports (n)`) uses the raw listening-port count, matching the existing `PortForwardButton` behavior on the workspace detail page. </details> > Generated by [Coder Agent](https://coder.com) |
||
|
Kyle Carberry
|
c16034d127 |
fix(site/src/pages/AgentsPage/components): match chat input font size to message bubbles (#24928)
The `/agents` chat composer rendered user input at 15px, but once a message was sent the user message bubble displays content at 13px (via `MessageContent` in `ChatElements/Message.tsx`). The size jump made what you typed not match what got displayed. Sets the `ChatMessageInput` className inside `AgentChatInput` to `text-[13px] leading-relaxed` so the composer matches the rendered user message. <sub>This PR was opened by a Coder agent on behalf of @kylecarbs.</sub> |
||
|
Thomas Kosiewski
|
69610cca75 |
feat(site/src): add Known Model autocomplete and frontend defaults (#24842)
Replaces the blank Model Identifier free-text input on the **Add Model** page with provider-scoped Known Model autocomplete and frontend-only metadata defaults for native OpenAI and Anthropic providers. Selecting a Known Model, or typing an exact canonical identifier and blurring the field, prefills `contextLimit`, the appropriate max-output-tokens field, and flat base pricing in the existing form. Edit mode, duplicate mode, and unsupported providers preserve the existing plain `Input` behavior and submit payload byte-for-byte. The catalog is curated TypeScript records sourced from `models.dev`, scoped initially to 6 OpenAI and 5 Anthropic models in declared display order. The pure `applyKnownModelDefaults` helper only writes a field when its current value still equals the form's initial value (or was last applied by Known Model defaulting in this form session, tracked cumulatively across selections). It never sets `compressionThreshold` or any reasoning/thinking fields, ignores tiered pricing, and never writes to the `model` field (canonicalization is the caller's responsibility). This PR also makes two narrow, additive changes outside the panel directory: - `site/src/components/Autocomplete/Autocomplete.tsx` gains optional `triggerAriaInvalid`, `triggerAriaDescribedBy`, and `onEscapeKeyDown` props so the new catalog branch can preserve `aria-invalid` / `aria-describedby` parity with the plain input and observe Escape close intent reliably across the Radix portal. Existing `Autocomplete` consumers are unaffected; `stopPropagation` is gated on `onEscapeKeyDown` being provided. - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/modelConfigFormLogic.ts` exports `deepGet` / `deepSet` so the defaulting helper can reuse them instead of re-implementing the same path traversal. No backend, API, SDK, or DB changes. No edits to `ModelsSection.tsx`, `ModelConfigFields.tsx`, `pricingFields.ts`, or `providerPolicyDefaults.ts`. ## Validation - 37 colocated unit tests across `knownModels/` (catalog, search, exact-canonical lookup, exact-alias lookup, badge, defaulting helper). - 134 unit tests across the full ChatModelAdminPanel directory pass. - 50 Storybook play tests on `ChatModelAdminPanel.stories.tsx` pass, including 17 DEREM-traceable interaction tests covering each plan-listed and review-driven scenario (open-no-error, Escape cancellation, sequential selection, double-apply guard, blur-canonical, alias cancellation, provider-change reset, ARIA parity, no-options copy, off-catalog substring commit, stale-cost-field, off-catalog interleaving, chain tracking, keyboard selection, clearable-disabled, off-catalog punctuation variant). - `tsc -p .` passes. ## Dogfooding Storybook was run locally and the user-facing flows were exercised end-to-end via `agent-browser`, capturing screenshots for: 1. OpenAI happy path (selection → defaults applied note → populated fields). 2. Anthropic happy path (selection → populated fields, reasoning/thinking blank). 3. Unsupported provider fallback (Google plain input, no popover). 4. OpenAI suggestion popover at empty focus (declared catalog order, context badges). 5. OpenAI search filter (typing `5.4` filters to GPT-5.4 / 5.4 mini / 5.4 nano). 6. Edit mode plain input (autocomplete correctly gated to add mode only). 7. DEREM-3: empty popover open on Add Model — no premature `Model ID is required.` error. 8. DEREM-1: autocomplete trigger `aria-invalid="true"` and `aria-describedby` matching the rendered error element. 9. DEREM-6: exact `No matching known models. You can still use this identifier.` copy. --- <details> <summary>📋 Implementation Plan</summary> # Plan: Known Model autocomplete and frontend-only defaults for Chat Model Admin ## Goal Improve the admin Add Model onboarding flow by replacing the blank Model Identifier experience with provider-scoped Known Model discovery suggestions for native OpenAI and Anthropic providers. Selecting a Known Model, or typing an exact canonical Known Model identifier and blurring the field, should prefill safe objective model metadata in the existing form without changing backend APIs, database schema, or runtime behavior. The primary UX goal is discovery for admins who do not know exact provider model identifiers or metadata. Typing convenience is a secondary benefit. ## Evidence and current code facts - The current Model Identifier field is a plain free-text `Input` in `site/src/pages/AgentsPage/components/ChatModelAdminPanel/ModelForm.tsx`. It submits as `model` and is only validated as a non-empty string. - The provider selector is disabled in edit and duplicate modes. In add mode, `ModelsSection.tsx` keys the form by provider, so provider changes remount `ModelForm`. - The shared `site/src/components/Autocomplete/Autocomplete.tsx` primitive already supports free-text input with suggestions and is the right UI primitive for this feature. - `modelConfigFormLogic.ts` owns form initialization via `buildInitialModelFormValues(...)`, and `modelConfigFormLogic.test.ts` already covers this pure logic area. - No frontend or backend Known Model catalog exists today. - The database has a non-unique `(provider, model)` index, not a uniqueness constraint. Multiple Model Configs can share the same Provider and Model Identifier, so suggestions must not hide already-configured models. - `models.dev/api.json` has provider-keyed model metadata with canonical IDs, names, limits, pricing, release dates, and `last_updated` values. The Phase 1 catalog should copy a curated subset into TypeScript records, not fetch at runtime. ## Domain language Use these terms consistently in code, tests, docs, and review discussion: - **Provider**: configured external AI service such as native `openai` or `anthropic`. - **Model Config**: persisted admin-defined config row used by Coder chat runtime. - **Model Identifier**: exact provider API string submitted as `model`, such as `gpt-5.5`. - **Known Model**: curated frontend catalog entry with advisory metadata for one canonical Model Identifier. - **Model Catalog**: checked-in frontend-only list of Known Models. - **Off-catalog Model Identifier**: user-entered Model Identifier that does not match any Known Model and remains valid. - **Default application**: copying advisory Known Model metadata into a draft add-mode Model Config form. ## Resolved design decisions ### UX scope - Implement this on the Add Model page/form only. - Do not add provider success popups, provider-side calls to action, or new deep-link behavior in this pass. - Use `Autocomplete` only when all are true: - form mode is add; - selected Provider is native `openai` or native `anthropic`; - that Provider has Known Models. - Edit mode, duplicate mode, and unsupported providers keep the existing free-text input behavior. ### Suggestion behavior - Suggestions open on focus only when the Model Identifier field is empty. - Once the field has text, suggestions open while typing or interacting with the autocomplete. - Empty unsupported-provider catalogs degrade silently to the existing plain input behavior. - When a supported provider has zero matches for a non-empty query, show a non-blocking empty state such as: `No matching known models. You can still use this identifier.` - Suggestion rows show: - display name; - canonical Model Identifier; - context-window badge, for example `1.05M context`. - Format context badges with a deterministic helper covered by tests, for example `200K context`, `400K context`, and `1.05M context`. - Do not show pricing, recommendations, capability tags, or large-context caveats in suggestion rows. - Keep catalog display order as product ordering. Do not show a visible `Recommended` badge. ### Canonical IDs and aliases - Selecting a Known Model always writes its canonical Model Identifier into the form. - Use non-date latest aliases as canonical onboarding IDs when the provider exposes them, such as `gpt-5.5` or `claude-sonnet-4-6`. - Date-pinned IDs may be aliases for search, but selecting a Known Model writes the non-date canonical ID. - Typing aliases filters suggestions but does not rewrite the field and does not apply defaults by itself. - Search over canonical ID, display name, and explicit aliases. - Search is case-insensitive and normalizes spaces, hyphens, underscores, and dots before substring matching. - Aliases are objective name or identifier variants only. Do not include editorial intent tags such as `best`, `cheap`, `fast`, `coding`, or `reasoning`. - Do not implement typo-tolerant fuzzy search in Phase 1. ### Default application rules - Default application only runs in add mode. - Explicit Known Model selection applies defaults immediately. - Exact typed or pasted canonical Model Identifier applies defaults on blur, not on every keystroke. This avoids prematurely applying `gpt-5.5` while the admin is typing `gpt-5.5-pro`. - Defaults fill only target fields whose current values still equal this form session's initial values. - Do not use Formik touched state as the source of truth for safety. - Do not implement field-level provenance tracking in Phase 1. - Capture an immutable `initialValuesRef` at `ModelForm` mount/remount and compare against that snapshot for safe default application. Do not compare against a live Formik reference that can drift. - Do not reapply repeatedly for the same provider/model pair in a single form session. - The defaulting helper must return both the next values and the list of applied form paths: ```ts interface ApplyKnownModelDefaultsResult { values: ModelFormValues; appliedFields: readonly string[]; } ``` - Treat Model Identifier canonicalization separately from metadata default application. `appliedFields` tracks populated metadata/form paths only, not the `model` field change caused by selecting a Known Model. - Show an inline note near Model Identifier only when `appliedFields.length > 0`, such as: `Defaults applied from GPT-5.5. Review and adjust before saving.` - Do not show a note for off-catalog identifiers, no-op Known Model selections, or selections that only canonicalize the Model Identifier. ### Initial Model Catalog Use curated TypeScript records with source metadata copied from models.dev. Do not check in the full `models.dev/api.json` snapshot and do not add a generator in Phase 1. Add a file-level comment that array order controls suggestion order so future cleanup does not accidentally change onboarding UX. Initial native OpenAI entries, in display order: 1. `gpt-5.5` 2. `gpt-5.5-pro` 3. `gpt-5.4` 4. `gpt-5.4-mini` 5. `gpt-5.4-nano` 6. `gpt-5.3-codex` Initial native Anthropic entries, in display order: 1. `claude-opus-4-7` 2. `claude-opus-4-6` 3. `claude-sonnet-4-6` 4. `claude-haiku-4-5` 5. `claude-sonnet-4-5` Do not include GPT-4.x, pre-5.3 GPT models, or Claude models older than 4.5 in this onboarding catalog unless product intentionally expands scope. Each Known Model record should include: - provider; - canonical Model Identifier; - display name; - aliases; - source metadata, including `sourceName: "models.dev"`, `sourceRetrievedAt`, and the model record's `last_updated` value; - `contextLimit` from `limit.context`; - `maxOutputTokens` from `limit.output`; - flat base pricing from supported `cost.*` fields. ### Field mapping - `models.dev.limit.context` maps to `contextLimit`. - `models.dev.limit.output` maps to the selected provider's exact max-output-tokens field when one exists, otherwise to generic `config.maxOutputTokens`. - Never fill both generic and provider-specific output-token fields for the same Known Model. - Ignore `models.dev.limit.input` unless the current form schema already exposes an exact matching field. - Map only flat base pricing fields that the existing form can persist: - `cost.input`; - `cost.output`; - `cost.cache_read`; - `cost.cache_write`. - Reuse `pricingFields.ts` or the existing pricing field descriptors instead of hard-coding cost form paths. - If `cache_read` or `cache_write` is absent from a models.dev entry, leave the corresponding field at its initial value and do not include it in `appliedFields`. - Ignore tiered pricing such as `context_over_200k` in Phase 1. Add a code comment in the adapter explaining that Coder currently persists flat pricing only. - Do not show a UI caveat for tiered pricing in Phase 1. - Do not set `compressionThreshold` from Known Models. - Do not prefill provider-specific reasoning or thinking fields in Phase 1, including: - OpenAI `reasoningEffort` and `reasoningSummary`; - Anthropic `sendReasoning`, `effort`, and `thinking.budgetTokens`. ## Proposed file structure Use `knownModels/` rather than `modelDefaults/` because the data powers both discovery and default application. New files: - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/knownModels/types.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/knownModels/openai.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/knownModels/anthropic.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/knownModels/index.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/knownModels/applyKnownModelDefaults.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/ModelIdentifierField.tsx` Existing files to modify: - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/ModelForm.tsx` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/modelConfigFormLogic.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/modelConfigFormLogic.test.ts` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/ChatModelAdminPanel.stories.tsx` Documentation artifacts to keep in sync if implementing from a clean workspace: - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/CONTEXT.md` - `site/src/pages/AgentsPage/components/ChatModelAdminPanel/docs/adr/0001-frontend-known-model-catalog.md` ## Implementation plan ### Phase 1: Red, define pure behavior first 1. Add tests in `modelConfigFormLogic.test.ts` or a colocated `knownModels` test file for: - provider-scoped lookup; - normalized alias search; - canonicalization on selection; - unknown model leaves values unchanged; - exact canonical ID lookup; - safe initial-value patching; - `appliedFields` output that excludes Model Identifier canonicalization; - tiered pricing ignored; - missing cache pricing fields left at initial values; - compression threshold not populated; - reasoning/thinking fields not populated; - output-token mapping prefers provider-specific exact field and never fills both; - context badge formatting. 2. Add lifecycle tests where feasible: - provider change in add mode remounts the form and resets `initialValuesRef`, `lastAppliedProviderModelRef`, and inline default-feedback state. 3. Add edge-case tests for event and reapplication semantics: - selecting `gpt-5.5` then blurring does not apply defaults a second time; - typing `gpt-5.5-pro` then blurring applies only pro defaults, never prefix `gpt-5.5` defaults; - selecting one Known Model, then another, does not overwrite fields already populated by the first selection because they no longer match initial values; - typing an alias then blurring does not canonicalize or apply defaults; - an Off-catalog value for a supported provider remains valid and preserves existing required-field validation behavior. 4. Add tests for the initial OpenAI and Anthropic catalog entries to ensure IDs, source metadata, and display order remain intentional. Quality gate: targeted unit tests fail for missing implementation. ### Phase 2: Green, add Known Model catalog and pure helpers 1. Add `knownModels/types.ts` with readonly types for catalog records and source metadata. 2. Add `knownModels/openai.ts` and `knownModels/anthropic.ts` with the initial catalog entries and file-level refresh comments. 3. Add lookup and search helpers in `knownModels/index.ts`. 4. Add `applyKnownModelDefaults(...)` as a pure helper that accepts: - current form values; - initial form values; - selected provider; - Known Model; - provider field mapping helpers if needed. 5. Ensure assertions or explicit guards make impossible cases fail fast during tests, for example missing provider, missing canonical ID, or invalid source metadata. Quality gate: targeted unit tests pass. ### Phase 3: Wire Model Identifier autocomplete UX Autocomplete integration constraints: - Control the shared `Autocomplete` with `inputValue` for the free-text Model Identifier string and `value: KnownModel | null` for selected suggestions. - Pass pre-filtered Known Model options to `Autocomplete`; do not rely on `cmdk` internal filtering once `inputValue` is controlled. - Clear the selected `KnownModel | null` value whenever the admin types arbitrary text that no longer corresponds to the selected Known Model. - Guard selection and blur event ordering so selecting a row does not cause the input blur handler to apply defaults a second time. - Run exact-match blur behavior only when focus leaves the whole field/combobox, not when focus moves into the suggestion list. - Store the last-applied provider/model pair in form-local state or a ref so add-mode provider remounts reset it naturally. - Preserve the existing field contract: label, tooltip/help text, `name`, validation error rendering, `aria-invalid`, `aria-describedby`, disabled state, Formik blur/touched behavior, and submitted request shape. 1. Add `ModelIdentifierField.tsx`. 2. Preserve existing plain `Input` markup for edit mode, duplicate mode, and unsupported providers. 3. For add-mode supported providers, render `Autocomplete` with: - controlled free-text value tied to Formik's `model` field; - custom row rendering with display name, canonical ID, and context badge; - open-on-empty-focus behavior; - non-blocking no-match copy for non-empty supported-provider queries; - keyboard support inherited from `Autocomplete`. 4. On Known Model selection: - set the form's `model` field to the canonical ID; - apply defaults immediately; - show inline feedback only if fields changed. 5. On blur: - if the final field value exactly equals a Known Model canonical ID, apply defaults safely; - do not auto-apply aliases on blur. 6. Track the last applied provider/model pair in the form session to avoid repeated reapplication. Quality gate: Storybook stories compile and the main interaction paths work locally. ### Phase 4: Storybook and UX coverage Add or extend `ChatModelAdminPanel.stories.tsx` with three user-visible flows: 1. OpenAI happy path: - open Add Model for OpenAI; - focus empty Model Identifier; - suggestions appear; - select `GPT-5.5`; - assert `gpt-5.5` is in the input; - assert inline defaults note appears; - assert visible context limit and max output fields populate; - expand the pricing section before asserting pricing fields, or keep detailed pricing assertions in unit tests if the Storybook UI would become brittle. 2. Anthropic happy path: - open Add Model for Anthropic; - select `Claude Opus 4.7`; - assert canonical ID, visible context limit, and output field populate; - expand the pricing section before asserting pricing fields, or keep detailed pricing assertions in unit tests if the Storybook UI would become brittle; - assert Anthropic reasoning/thinking fields remain blank. 3. Unsupported provider fallback: - open Add Model for Azure or openai-compat; - assert Model Identifier behaves as plain free text and no suggestion popover appears. If practical, include one keyboard selection path in Storybook or manual dogfooding: - tab/focus Model Identifier; - arrow to a suggestion; - press Enter; - verify canonicalization and defaults. Quality gate: Storybook interaction tests pass for touched stories. ### Phase 5: Refactor and documentation pass 1. Keep catalog data isolated from UI rendering code. 2. Keep provider field mapping in one helper so future Google, Bedrock, OpenRouter, or Azure support does not require editing defaulting logic everywhere. 3. Ensure comments explain why tiered pricing and reasoning defaults are excluded. 4. Update `CONTEXT.md` and ADR if implementation changes any design decision captured there. 5. Run formatting and linting for touched frontend files. Quality gate: no broad refactors beyond this feature's files. ## Validation commands Use the repo's existing frontend validation commands, scoped where possible: - `pnpm -C site test <targeted ChatModelAdminPanel pattern>` - `pnpm -C site test <targeted modelConfigFormLogic pattern>` - `pnpm -C site test:storybook` - `pnpm -C site lint:types` - `pnpm -C site check` If command names differ in this workspace, inspect `site/package.json` and use the closest existing targeted commands. Do not claim success until the actual commands run and pass. ## Dogfooding plan Primary dogfood path is Storybook because this is a form-level UI improvement using mocked admin data. 1. Run Storybook for the Chat Model Admin Panel. 2. Record a short video showing: - OpenAI Add Model, focus empty Model Identifier, suggestions appear, select `GPT-5.5`, defaults note appears, fields populate; - Anthropic Add Model, select `Claude Opus 4.7`, fields populate, reasoning/thinking fields remain blank; - unsupported provider Add Model, Model Identifier stays free text with no suggestions. 3. Capture screenshots for the final state of each flow and attach them for review. 4. If implementation touches routing, `ModelsSection` URL state, or provider pages, also run the local UI and record `/agents/settings/models?newModel=openai` exercising the same OpenAI flow. ## Acceptance criteria - Add-mode native OpenAI and Anthropic Model Identifier fields provide discovery suggestions from the curated Known Model catalog. - Suggestions appear on empty focus and filter as the admin types. - Unsupported providers, edit mode, and duplicate mode preserve the current plain input behavior. - Selecting a Known Model canonicalizes the field and safely applies objective defaults. - Exact typed/pasted canonical IDs apply defaults on blur. - Off-catalog Model Identifiers remain valid and non-blocking. - Display name, context limit, output-token field, and flat pricing fill only when target fields still match initial values. - Compression threshold, tiered pricing, and provider-specific reasoning/thinking fields are not populated by Phase 1 defaults. - Inline feedback appears only when default application changed at least one field. - Unit tests, Storybook coverage, typecheck, formatting, and lint/check commands pass. - Dogfooding includes screenshots and video recordings. ## Risks and mitigations - **Catalog staleness**: models change frequently. Mitigate with source metadata and clear file-level refresh comments. - **Provider namespace mistakes**: Azure, Bedrock, OpenRouter, and openai-compat use different identifier semantics. Mitigate by supporting only native OpenAI and Anthropic in Phase 1. - **Auto-fill surprise**: defaults can feel magical. Mitigate with selection-first UX, blur-only exact-match behavior, initial-value safety checks, and inline feedback. - **Pricing inaccuracy for tiered models**: current form persists flat prices only. Mitigate by mapping base flat prices only and documenting tiered pricing as out of scope. - **Reasoning option overreach**: generic source metadata does not map cleanly to provider-specific controls. Mitigate by leaving reasoning/thinking fields blank in Phase 1. - **Overbroad UI changes**: replacing an input can affect accessibility and keyboard users. Mitigate by using the shared Autocomplete primitive, preserving plain Input fallback, and dogfooding keyboard selection. </details> --- _Generated with [`mux`](https://github.com/coder/mux) • Model: `anthropic:claude-opus-4-7` • Thinking: `max`_ |





