---
title: Database Access with PostgreSQL on GCP Cloud SQL
description: How to configure Teleport Database Access with GCP Cloud SQL PostgreSQL.
videoBanner: br9LZ3ZXqCk
---
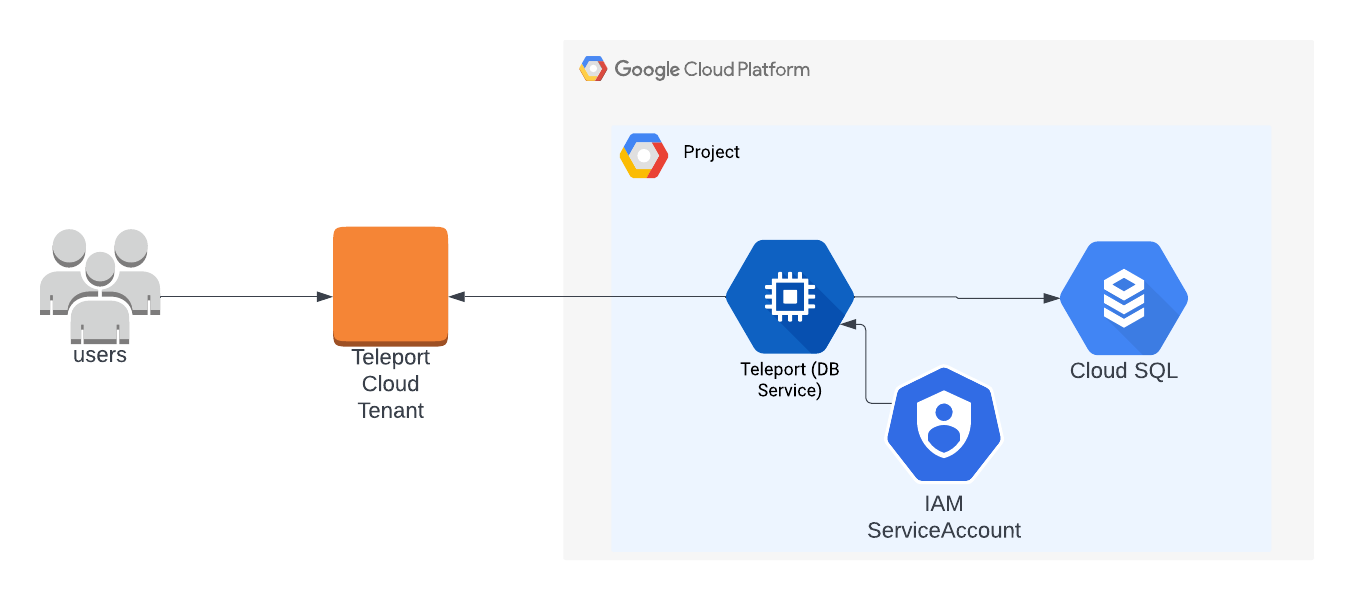
This guide will help you to:
- Install Teleport `(=teleport.version=)`.
- Set up Teleport to access your PostgreSQL on Google Cloud SQL.
- Connect to your databases through Teleport.

## Prerequisites
(!docs/pages/includes/edition-prereqs-tabs.mdx!)
- Google Cloud account
- Command-line client `psql` installed and added to your system's `PATH` environment variable.
- A host, e.g., a Compute Engine instance, where you will run the Teleport Database
Service
(!docs/pages/includes/tctl.mdx!)
## Step 1/7. Enable Cloud SQL IAM authentication
Teleport uses [IAM database authentication](https://cloud.google.com/sql/docs/postgres/authentication)
with Cloud SQL PostgreSQL instances.
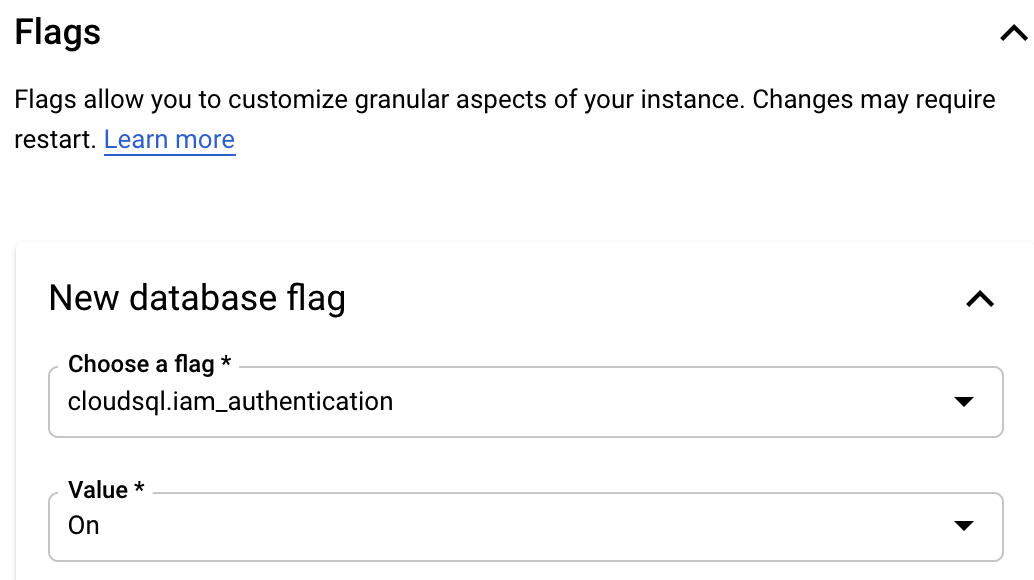
If you're [creating](https://console.cloud.google.com/sql/choose-instance-engine)
a new PostgreSQL instance, make sure to add the `cloudsql.iam_authentication`
database flag under "Customize your instance / Flags" section:
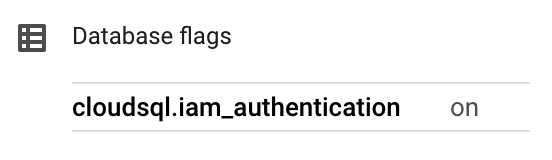
To check whether IAM authentication is enabled for an existing Cloud SQL instance,
look for the flag on the Configuration panel on the instance's Overview page:
If it isn't enabled, you can add this flag using the "Edit configuration" dialog
at the bottom of the Configuration panel. Note, changing this setting may
require a database instance reboot.
## Step 2/7. Create a service account for the database
Teleport uses service accounts to connect to Cloud SQL databases.
### Create a service account
Go to the IAM & Admin [Service Accounts](https://console.cloud.google.com/iam-admin/serviceaccounts)
page and create a new service account:

Press "Create".
### Grant permissions
On the second step grant this service account the "Cloud SQL Instance User" role
which will allow it to connect to Cloud SQL instances using IAM token for
authentication:

Press "Done".
### Configure authentication for your service account
Now go back to the Users page of your Cloud SQL instance and add a new user
account. In the sidebar, choose "Cloud IAM" authentication type and add the
service account you've just created:

Press "Add" and your Users table should look similar to this:

See [Creating and managing IAM users](https://cloud.google.com/sql/docs/postgres/create-manage-iam-users)
in Google Cloud documentation for more info.
## Step 3/7. Create a service account for Teleport Database Service
The final part of GCP configuration is to create a service account for the
Teleport Database Service.
### Create a service account
Go to the [Service Accounts](https://console.cloud.google.com/iam-admin/serviceaccounts)
page and create a service account:

### Grant permissions
Assign the Service Account the following IAM roles:
- "Service Account Token Creator" will allow the Database Service to generate
IAM authentication tokens when connecting to the database as the service account user
we created above.
- Either "Cloud SQL Viewer" or "Cloud SQL Admin":
- "Cloud SQL Viewer" will allow the Database Service to automatically download
your Cloud SQL instance's root CA certificate, but does not support client
certificate authentication.
- "Cloud SQL Admin" will allow the Database Service to automatically download
your Cloud SQL instance's root CA certificate and generate an
ephemeral client certificate when the GCP instance is configured to
"Allow only SSL connections."
Assign it the "Service Account Token Creator" role:

"Service Account Token Creator", "Cloud SQL Viewer", and "Cloud SQL Admin"
IAM roles include more permissions than the Database Service needs. To further
restrict the service account, you can create a role that includes only the
following permissions:
```ini
# Used to generate IAM auth tokens when connecting to a database instance.
iam.serviceAccounts.getAccessToken
# Used to auto-download the instance's root CA certificate.
cloudsql.instances.get
# Used to generate an ephemeral client certificate when the GCP instance
# is configured to "Allow only SSL connections." (optional)
cloudsql.sslCerts.createEphemeral
```
### Create a key for the service account
Once created, go to that service account's Keys tab and create a new key:

Make sure to choose JSON format:

Save the file. The Teleport Database Service will need it to be able to generate
IAM auth tokens.
## Step 4/7. Gather Cloud SQL instance information
To connect a Cloud SQL database to Teleport, you'll need to gather a few pieces
of information about the instance.
- GCP Project ID.
You can normally see it in the organization view at the top of the GCP dashboard.
- Cloud SQL instance ID.
The instance ID is the name of your Cloud SQL instance shown at the top of the
Overview page:
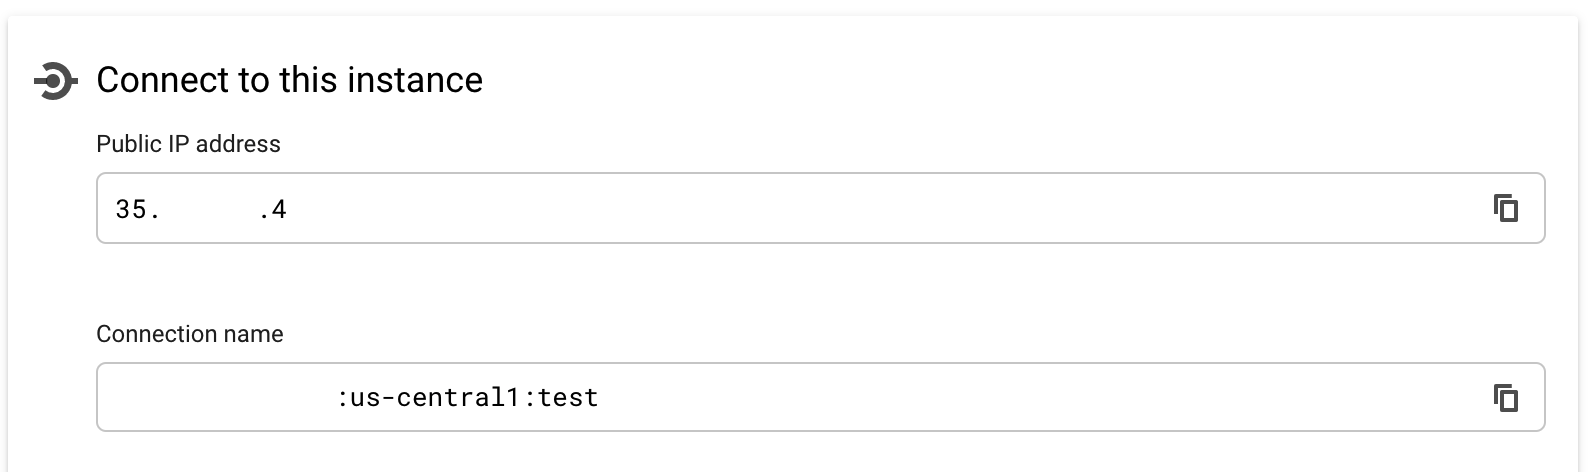
- Cloud SQL instance endpoint.
You will use the instance's public IP address to connect to it. It can be viewed
on the "Connect to this instance" panel on the Overview page:
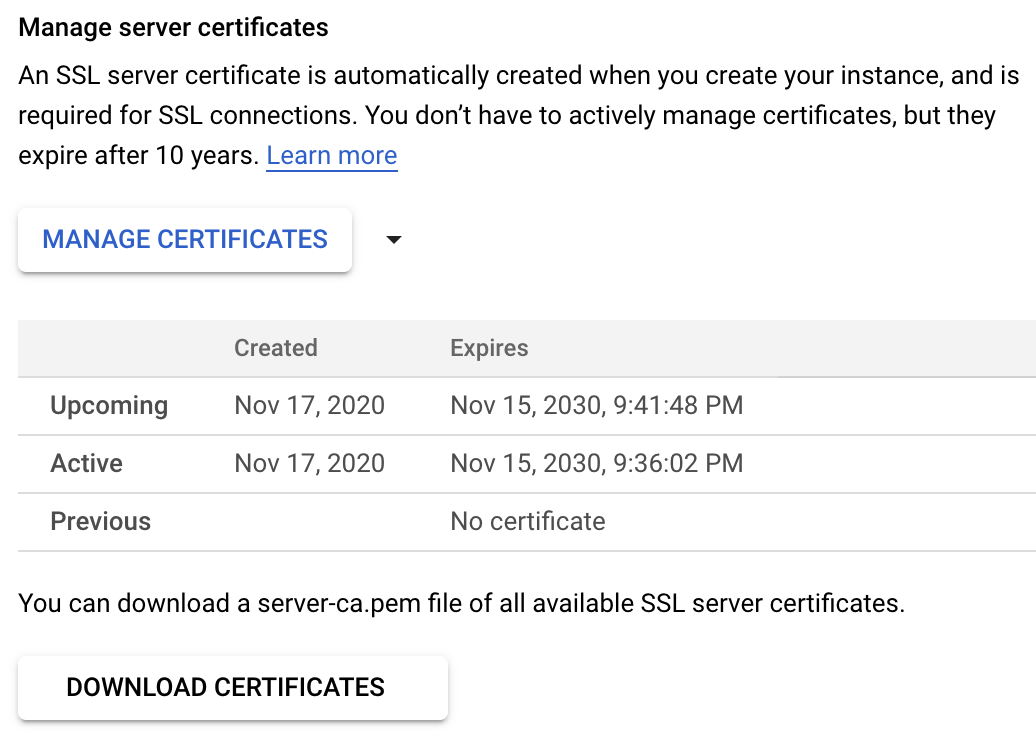
- Cloud SQL instance root certificate.
The instance's root certificate is required so Teleport can validate the
certificate presented by the database instance. You can download `server-ca.pem`
file from the Connections tab under Security section:
## Step 5/7. Set up the Teleport Database Service
(!docs/pages/includes/database-access/token.mdx!)
Install Teleport on the host where you will run the Teleport Database Service:
(!docs/pages/includes/install-linux.mdx!)
### Create a user
(!docs/pages/includes/database-access/create-user.mdx!)
## Step 6/7. Set up the Teleport Database service
Below is an example of a Database Service configuration file that proxies
a single Cloud SQL PostgreSQL database:
```yaml
version: v3
teleport:
data_dir: /var/lib/teleport-db
nodename: test
# Proxy address to connect to. Note that it has to be the proxy address
# because the Database Service always connects to the cluster over a reverse
# tunnel.
proxy_server: teleport.example.com:3080
db_service:
enabled: "yes"
# This section contains definitions of all databases proxied by this
# service, can contain multiple items.
databases:
# Name of the database proxy instance, used to reference in CLI.
- name: "cloudsql"
# Free-form description of the database proxy instance.
description: "GCP Cloud SQL PostgreSQL"
# Database protocol.
protocol: "postgres"
# Database endpoint. For Cloud SQL use instance's public IP address.
uri: "35.1.2.3:5432"
# Path to Cloud SQL instance root certificate you downloaded above.
ca_cert_file: /path/to/cloudsql/instance/root.pem
# GCP specific configuration when connecting Cloud SQL instance.
gcp:
# GCP project ID.
project_id: ""
# Cloud SQL instance ID.
instance_id: "test"
# Labels to assign to the database, used in RBAC.
static_labels:
env: dev
auth_service:
enabled: "no"
ssh_service:
enabled: "no"
proxy_service:
enabled: "no"
```
```yaml
version: v3
teleport:
data_dir: /var/lib/teleport-db
nodename: test
# Proxy address to connect to. Use your Teleport Cloud tenant address here.
proxy_server: mytenant.teleport.sh:443
db_service:
enabled: "yes"
# This section contains definitions of all databases proxied by this
# service, can contain multiple items.
databases:
# Name of the database proxy instance, used to reference in CLI.
- name: "cloudsql"
# Free-form description of the database proxy instance.
description: "GCP Cloud SQL PostgreSQL"
# Database protocol.
protocol: "postgres"
# Database endpoint. For Cloud SQL use instance's public IP address.
uri: "35.1.2.3:5432"
# Path to Cloud SQL instance root certificate you downloaded above.
ca_cert_file: /path/to/cloudsql/instance/root.pem
# GCP specific configuration when connecting Cloud SQL instance.
gcp:
# GCP project ID.
project_id: ""
# Cloud SQL instance ID.
instance_id: "test"
# Labels to assign to the database, used in RBAC.
static_labels:
env: dev
auth_service:
enabled: "no"
ssh_service:
enabled: "no"
proxy_service:
enabled: "no"
```
A single Teleport process can run multiple different services, for example
multiple Database Access instances as well as other services such the SSH
Service or Application Service.
Start the Database Service:
```code
$ teleport start --config=/path/to/teleport-db.yaml --token=/tmp/token
```
### GCP credentials
The Teleport Database Service must have credentials of `teleport-db-service` GCP
service account we created
[above](#step-37-create-a-service-account-for-teleport-database-service) in order to be
able to generate IAM auth tokens.
The easiest way to ensure that is to set the `GOOGLE_APPLICATION_CREDENTIALS`
environment variable to point to the JSON credentials file you downloaded
earlier.
See [Authenticating as a service account](https://cloud.google.com/docs/authentication/production)
in the Google Cloud documentation for more details.
## Step 7/7. Connect
Once the Database Service has joined the cluster, log in to see the available
databases:
```code
$ tsh login --proxy=teleport.example.com --user=alice
$ tsh db ls
# Name Description Labels
# -------- ------------------------ --------
# cloudsql GCP Cloud SQL PostgreSQL env=dev
```
```code
$ tsh login --proxy=mytenant.teleport.sh --user=alice
$ tsh db ls
# Name Description Labels
# -------- ------------------------ --------
# cloudsql GCP Cloud SQL PostgreSQL env=dev
```
Note that you will only be able to see databases your role has access to. See
our [RBAC](../rbac.mdx) guide for more details.
To retrieve credentials for a database and connect to it:
```sh
$ tsh db connect cloudsql
```
You can optionally specify the database name and the user to use by default
when connecting to the database instance:
```code
$ tsh db connect --db-user=teleport@.iam --db-name=postgres cloudsql
```
When connecting to the database, use the name of the database service account
that you added as an IAM database user
[above](#step-27-create-a-service-account-for-the-database), minus the
`.gserviceaccount.com` suffix. The database user name is shown on the Users
page of your Cloud SQL instance.
To log out of the database and remove credentials:
```code
# Remove credentials for a particular database instance.
$ tsh db logout cloudsql
# Remove credentials for all database instances.
$ tsh db logout
```