Application sessions were previously only logged when launching an application
session via the UI, and not from the `tsh app login` command. This has been
corrected. The AppName and AppURI are now passed in as part of the gRPC
request to the auth server, which is then used to emit the audit event.
* Introduce proto types for ProvisionTokenV3

* Add methods to ProvisionTokenV3 to support ProvisionToken iface

* Start building v3 support into the client

* add support for mashalling and unmarshalling ProvisionTokenV3

* Start unit testing ProvisionTokenV3

* Remove oneof to support yaml marshal/unmarshal

* Client should try V3 methods and fallback to v2

* More tests

* Fix join tests

* Fix integration tests

* Switch integration tests to use v3 spec

* Switch iam tests to use ProvisionTokenV3

* Change ec2 join tests to use V3 tokens

* Fix events tests for V3 token

* support ProvisionTokenV3 within API client events handler

* Explicitly specify JoinMethod

* Tidy up final usage of NewProvisionTokenV2FromSpec in tests

* Improve proto docs on ProvisionTokenV3

* Fix bot join tests

* Clarify error message for invalid join method

* Adjust resource version comment

* Fix comments and return error rather than bool in V2() method

* Catch incompatible conversions case

* Include V2 ProvisionToken in tests and add appropriate DELETE IN notes

* Fix linter warnings/unit test failures

* Use nolint rather than lint:ignore

* Add more DELETE IN notes

* Run goimports on join_ec2_test.go

* Address PR comments from tim.

* Add more deprecation/delete in notices

* Improve godoc comments on checkAndSetDEfaults for provider config

* Simplify implementation by dropping client-ahead compatability

* Add some support for client-ahead but with conversion to v3

* Update code comments to include responsible party

* Rename `Role` to `RoleARN` in EC2 configuration for clarity

* Fix tests for Role -> RoleARN rename

* Move MustCreateProvisionToken out of API and into test packages

* Properly go imports files
Replace role/authPref RequireSessionMFA (bool) with RequireMFAType
(string).

  - Add new RequireMFAType constant values with custom boolean marshalling.

  - Add RequireMFAType to role and auth preference and deprecate
RequireSessionMFA.

  - Add session-mfa override login when hardware_key_touch is enforced.

  - Add protobuf enum for RequireMFAType.

  - Add support for proto enums in protoc-gen-crd and update Kubernetes
Operator manifests.
This test takes between 10-20 seconds to run, because it waits for
a websocket ping message and pings run on a 10s timer by default.

It turns out, we allow specifying the keepalive interval in the
terminal request, but due to a bug we would always overwrite that
value with what's in the cluster networking config.

Fix the bug and speed up the test by overriding the keepalive interval
to something shorter for this test.

Before:

    ➜ go test -run TestTerminalPing -race ./lib/web -count=1
    ok      github.com/gravitational/teleport/lib/web       13.122s

After:

    ➜ go test -run TestTerminalPing -race ./lib/web -count=1
    ok      github.com/gravitational/teleport/lib/web       3.394s
While looking up github.com/gokyle/hotp I found some old deprecation warnings
and decided to address them.

* Remove HOTP support
* Update comment on checkOTP
* Remove OTPType
* Remove a few more HOTP references
Update metalinter, fix a few lint warnings and replace deprecated linters.

`deadcode`, `structcheck` and `varcheck` are abandoned and now replaced by [`unused`][1].

Since 1.19, `go fmt` reformats godocs according to https://go.dev/doc/comment. I've done a bulk-reformatting of the codebase to keep the linter happy. Backporting is mostly harmless (the exception being `lib/services/role_test.go`, that for some reason breaks the _old_ linter using the new format).

[1]: https://golangci-lint.run/usage/linters/

* Bump golangci-lint version
* Replace abandoned linters
* Fix bodyclose on lib/auth/github.com
* Fix bodyclose on lib/kube/proxy/streamproto/proto_test.go
* Fix bodyclose on lib/srv/alpnproxy/proxy_test.go
* Fix bodyclose on lib/web/conn_upgrade_test.go
* Silence staticcheck on lib/kube/proxy/forwarder_test.go
* Silence staticcheck on lib/utils/certs_test.go
* Address BuildNameToCertificate deprecation warnings
* Run `go fmt ./...`
* Run `go fmt ./...` on api/
* Ignore formatting in role_test.go
* Remove redundant initializers in lib/srv/uacc/
* Update e/
* Prevent ssh.Session SendRequest from wrapping payload twice

Payloads were inadvertently being wrapped twice by sessions making
the ssh server unable to parse the request payload. This is largely
only an issue for window-change requests, as they are the only request
being sent directly via a session that contains a payload. All window-change
requests now use ssh.Session WindowChange instead or sending the request
manually.
This PR implements the SSH Tester for ConnectionDiagnostic feature.
This feature is also known as Test Connection, part of Teleport
Discover.
The goal here is to provide immediante feedback about a newly added
resource. Can the user connect to it?
We are targetting SSH Nodes as a first ResourceKind.
To test the access to an SSH Node we require the ResourceName and a
login username (ssh principal).
Then a series of checks will occur in two places:
- SSH client in the Web server
- SSH server in the SSH agent
The ssh client creates a new Connection Diagnostic with some initial
state.
Then it tries to build up the necessary SSH config
This already gives us a couple of things to check for:
- does the node exist and does the current user (inherited from
websession) can access it?
- is the node accepting TCP connections (in the specific port)?
- is the node accepting SSH protocol on top of the TCP connection?
Then, the ConnectionDiagnosticID is inject into the certificate and the
SSH Server receives it and will also Append traces into it:
- is the requested principal allowed for the current user?
- does the requested principal exist in the target node?
This is not an exhaustive list of checks.
For a complete list of which checks are verified please see the
TestDiagnoseSSHConnection test.
After all those checks, it returns if the Connection was successful and
what all of the traces generated along the way.
Demo:


* Allow for multiple installer scripts instead of using a singleton

* Resolve comments

- require name be provided to installer
- MetaNameClusterInstallerScript -> defaults.InstallerScriptName
- Require VerbList for GetInstallers

* Resolve comments

- Include the default installer in GetInstallers output
- Update how the scripts are prefixed

* resolve conflicts

* make the linters happy
Similarly to #15856, moves lib/ protos (except for Connect) under the proto/ tree.

The intended layout is a mirror of api:

```
teleport-root
  proto/         <- root for protos and proto imports
    teleport/
      lib/...
  gen/proto/go/  <- ideal root for generated protos
```

#15187

* Move lib/ protos under the proto/ tree
* Reformat protos
* Update generated protos
Primary Changes:
 - Remove reliance on Private Key PEM:
 - Update native and keygen packages to return PrivateKey instead of PEM key
 - Add new PrivateKey interface which implements crypto.Signer
 - Replace PEM encoded private key usage where possible
 - Replace calls to tls.(Load)X509KeyPair with keys.(Load)X509KeyPair in
client packages

Minor Changes:
 - Remove unused agent.AddedKey return from LoadKey
 - Simplify sshutils and removed unused code paths
 - Add ecdsa and ed25519 key support
* Add connection diagnostic access to UI user context
* Implement resource checker in the web api layer
* Remove setting NeedTotalCount flag for web api list resources
Recently we added a way to add labels on newly added nodes based on the
token.
https://github.com/gravitational/teleport/pull/15114
Each token now has a list of SuggestedLabels, which are used to feed
that list.

However, if that list is empty, the generated script would trigger the
following error when running the `teleport node configure ...` command:
`teleport: error: unexpected`

This happens because the command is generating an empty argument `""`
when running the `teleport node configure ...` command.
So it looks like this:
```bash
${TELEPORT_BINARY_DIR}/teleport node configure \
      --token token \
      joinmethod \
      --ca-pin pin \
      --auth-server host:port \
      "" \
      --output someport
```
That empty argument breaks things.

So, in order to fix it, we are going to change the default value when no
labels are provided.
Instead of an empty string, we'll use an empty array.

Demo (teleport node configure message removed for brev
No label
```bash
$ LABELS_FLAG=(); f=$(mktemp -d)/node.yaml; teleport node configure --auth-server w:1 "${LABELS_FLAG[@]}" --output $f && yq .s
sh_service.labels $f

enabled: "yes"
commands:
  - name: hostname
    command: [hostname]
    period: 1m0s

```

Single label
```bash
$ LABELS_FLAG=(--labels x=y); f=$(mktemp -d)/node.yaml; teleport node configure --auth-server w:1 "${LABELS_FLAG[@]}" --output $f && yq .ssh_service $f

enabled: "yes"
labels:
  x: "y"
commands:
  - name: hostname
    command: [hostname]
    period: 1m0s

```

Multiple labels
```bash
$ LABELS_FLAG=(--labels x=y,dev=prod); f=$(mktemp -d)/node.yaml; teleport node configure --auth-server w:1 "${LABELS_FLAG[@]}" --output $f && yq .ssh_service $f

enabled: "yes"
labels:
  dev: prod
  x: "y"
commands:
  - name: hostname
    command: [hostname]
    period: 1m0s
```
This PR adds the concept of ConnectionTester

ConnectionTester will generate ConnectionDiagnostics by connecting to
the actual resource using a user and some Resource Specific parameters
(principal for SSH access, Database User and Name for Database access,
and so on) and storing the result of multiple checkpoints.

Each resource will have a ConnectionTester (we'll start by SSH access
and then Databases).

It also improves Connection Diagnostics by adding
- update operation (similar to the create one)
- a list of traces, which contain the result of checkpoints in multiple
  steps of the connection flow

As an example, for SSH, we'll have at least the following checks:
- Node is reachable
- User has the right permissions
- Node has the expected Principal

The trigger to test a connection will be an endpoint, because our
primary goal is to let the user test the access right after adding the
resource.

This PR does not implement the actual SSHConnectionTester but creates
most of the boilerplate to do so.

The next PR will focus in adding the actual traces.
* Add an installer script resource type and HTTP endpoint

* Add default installer scripts

* Resolve comments

- run `shfmt` over the installer script
- add MustNewInstaller
- move default installer logic to GetInstaller
- only include PublicProxyAddr in server.Config

* Resolve comments

- move from auth_with_roles -> auth/grpcserver
- document `MustNewInstallerV1`
Websockets are a message-based protocol, but our combination of
an io.Writer wrapper and io.Copy means some TDP messages may
get broken up and emitted as separate message events in the browser.

Our UI assumes that each 'message' event is a single TDP message,
so we make sure that each TDP message we send corresponds to a
single WriteMessage call.
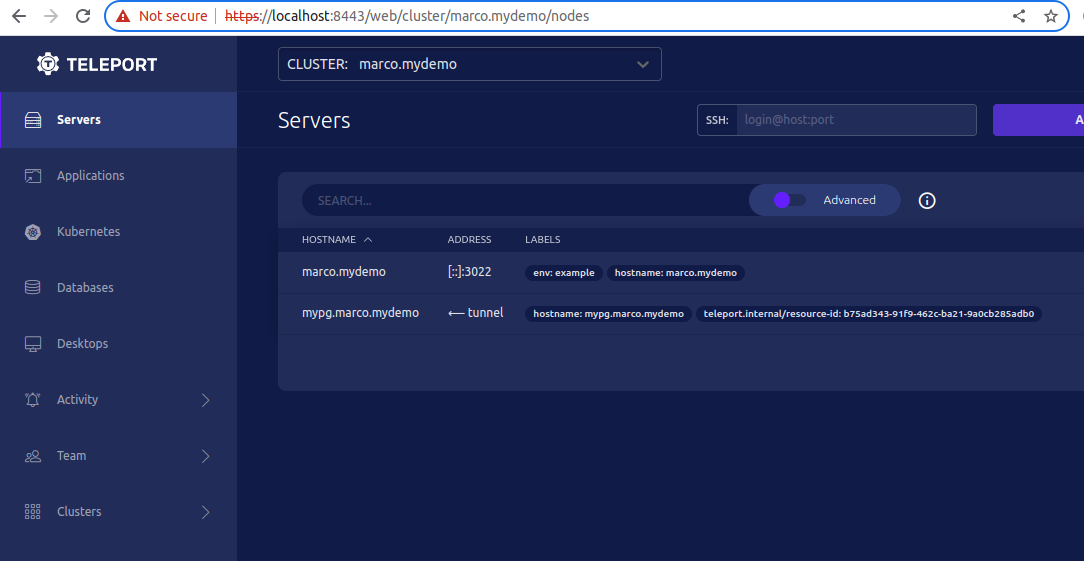
For Teleport Discover, the user will be able to test connecting to a
resource right after adding it.
The flow should look like this:
- User selects the resource type - in this case Server/Nodes
- WebUI generates a new Token
- WebUI shows the `sudo bash .../<token>/install.sh` to the user
- When the user runs this command, and assuming everything works out,
the WebUI should be able to receive the Server/Node that was
generated from that specific Token.
To achieve this, here's a more detailed flow, which this PR implements
- User selects the resource type - in this case Server/Nodes
- WebUI generates a new Token
This generates a Provision Token which contains a RefResourceID
WebUI receives back that ID
- WebUI shows the `sudo bash .../<token>/install.sh` to the user
This generates a script which includes setting the labels as part of
the `teleport configure` command:
`$ teleport configure ... --labels teleport.internal/resource-id=<refResourceID> ...`
- User runs the provided command on the target host
- WebUI should be able to query the Servers/Nodes which contain that
specific `<resource-id>` and allow the user to connect to it.
Demo:
Adds a wrapper around `ssh.Session` which injects tracing context
in a similar manner to the `ssh.Client` wrapper. All usages of
`ssh.Session` have now been replaced and have the appropriate
`context.Context` passed along

Part of #12241
## What

First part of the Kubernetes [Discovery RFD](https://github.com/gravitational/teleport/pull/13376/) to introduce a Kubernetes server per cluster.

This PR introduces a separate Kubernetes server that uses the already introduced `KubernetesClusterV3`.

## Compatibility

In previous versions, Kubernetes Clusters were part of regular `ServerV2` resource and this refactoring deprecates the `ServerV2` usage but keeps them for compatibility with previous version.

Everything is backward compatible, so v10 kubernetes agents and trusted clusters can connect fine.

## Next steps

Once this is merged, a new PR will introduce dynamic registration for Kubernetes Clusters discovered through EKS Discovery.
In the context of Teleport Discover we are trying to ease the usage of Teleport for the user's first interaction.
When adding a new database resource the user must, among other things, generate the mTLS files
Examples:
https://goteleport.com/docs/database-access/guides/postgres-self-hosted/#step-25-create-a-certificatekey-pairhttps://goteleport.com/docs/database-access/guides/mysql-self-hosted/#step-24-create-a-certificatekey-pair
This PR aims to reduce this friction: the user should be able to setup the resource without prior setup of local tools (`tsh login`)
We're doing this by providing an endpoint that will return those exact files
Demo
```shell
marco@lenix ~/p/downloadmtls> curl --silent --insecure 'https://127.0.0.1.nip.io:3080/v1/webapi/sites/lenix/sign' --dat
a '{"hostname":"discover.example.com", "ttl":"9999h", "format": "db"}' --header 'Authorization: Bearer 308bf3dd3019ddc4
2cff44a48e028480' --header 'Content-Type: application/json' -OJ
marco@lenix ~/p/downloadmtls> tar -xvf teleport_mTLS_discover.example.com.tar.gz
server.key
server.crt
server.cas
marco@lenix ~/p/downloadmtls> head -1 server.*
==> server.cas <==
-----BEGIN CERTIFICATE-----
==> server.crt <==
-----BEGIN CERTIFICATE-----
==> server.key <==
-----BEGIN RSA PRIVATE KEY-----
```
Fixes https://github.com/gravitational/teleport/issues/14049
In Teleport Discover, we want to improve the UX of adding a resource.
We'll suggest users to test accessing a resource, and give them immediate feedback using the UI.

Note: we'll add this feature to Server Access, later one we'll add other resources.

After adding a server resource, the user will be presented with a command to test the connection:
`tsh ssh --test-id=123 user@host`

Running that command will provide the user feedback right in the UI of whether or not it worked.
If not, a short message will be displayed describing why it didn't work and how the user can solve the problem.

---

To achieve this we'll need a couple of changes:
1. new resource that stores the result of trying to connect to a given resource, so that the UI can ask for it
2. change `tsh ssh` to receive the `--test-id` flag and write the result to a record of this new resource

This PR addresses 1 - new resource.

A new resource is created:
```
Connection Diagnostics
- success (bool)
- message (string)
```

Two new rpc methods:
- create connection diagnostics
- read connection diagnostics

One new HTTP Endpoint:
- read connection diagnostics

Related to
https://github.com/gravitational/teleport/issues/13957
When we download, we write the file contents with the
`http.ResponseWriter` which is also used to write our
replies, so it was also writing our success replies.

fixes https://github.com/gravitational/teleport/issues/14557
 Mike Wilson


