mirror of
https://github.com/coder/coder.git
synced 2026-09-24 15:04:27 +08:00
chore: adopt markdownlint and markdown-table-formatter for *.md (#15831)
Co-authored-by: Edward Angert <EdwardAngert@users.noreply.github.com>
This commit is contained in:
 Muhammad Atif Ali
co-authored by
Edward Angert
Edward Angert
parent
08463c27d8
commit
94f5d52fdc
@@ -3,7 +3,7 @@
|
||||
<div>
|
||||
<a href="https://github.com/ericpaulsen" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Eric Paulsen</span>
|
||||
<img src="https://github.com/ericpaulsen.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/ericpaulsen.png" alt="ericpaulsen" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
January 26, 2024
|
||||
|
||||
@@ -47,8 +47,8 @@ deployed with Coder and has 1000 users in production. Today, MegaCo has a single
|
||||
(default) organization and a central platform team but is evaluating whether to
|
||||
use organizations for several use cases.
|
||||
|
||||
| **Use Case** | **Description** | **Good fit for organizations?** |
|
||||
| ------------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------- |
|
||||
| **Use Case** | **Description** | **Good fit for organizations?** |
|
||||
|--------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------|
|
||||
| Mergers and acquisitions | Raptix, a 180-person startup recently acquired by MegaCo, has an independent cloud account, platform team, and Terraform modules and pipelines for deploying their code. They want to use Coder. | ✅ Organizations |
|
||||
| Independent cloud-native teams that manage their namespaces, images, and/or clusters | MegaCo has six teams responsible for their own dev, staging, and production Kubernetes clusters and frequently deploy & test their work with `kubectl` and `helm`.</br></br>They wish to hook up Coder to their cluster so they can write and manage IDE templates for connecting to the cluster with their IDE | ✅ Organizations |
|
||||
| Java monolith | MegaCo has identified that anyone developing the Java monolith is best served with a VM instead of a container/cloud-native environment.</br></br>However, the Java team is supported by MegaCo's central platform team. | ❌ Use instead:</br>A separate template and/or groups |
|
||||
@@ -115,18 +115,18 @@ within an organization. Custom roles can be applied to the default organization.
|
||||
|
||||
Some examples of custom roles that can be created:
|
||||
|
||||
**Provisioner Admin**
|
||||
### Provisioner Admin
|
||||
|
||||
- The user can deploy provisioners but not manage templates. This may be useful
|
||||
if automation is used to create and update templates in the organization.
|
||||
|
||||
**Template Editor**
|
||||
### Template Editor
|
||||
|
||||
- Inverse of provisioner admin: User can manage templates but not deploy
|
||||
provisioners. This may be useful if the provisioner and template are deployed
|
||||
via automation and users are allowed to edit them.
|
||||
|
||||
**Template Pusher**
|
||||
### Template Pusher
|
||||
|
||||
- A system account that can push new templates from a git repo but cannot manage
|
||||
users or delete templates.
|
||||
|
||||
@@ -4,7 +4,7 @@
|
||||
<span style="vertical-align:middle;">Author: </span>
|
||||
<a href="https://github.com/BrunoQuaresma" style="text-decoration: none; color: inherit; margin-bottom: 0px;">
|
||||
<span style="vertical-align:middle;">Bruno Quaresma</span>
|
||||
<img src="https://avatars.githubusercontent.com/u/3165839?v=4" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://avatars.githubusercontent.com/u/3165839?v=4" alt="Bruno Quaresma" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
August 06, 2024
|
||||
|
||||
@@ -4,7 +4,7 @@
|
||||
<span style="vertical-align:middle;">Author: </span>
|
||||
<a href="https://github.com/Emyrk" style="text-decoration: none; color: inherit; margin-bottom: 0px;">
|
||||
<span style="vertical-align:middle;">Steven Masley</span>
|
||||
<img src="https://avatars.githubusercontent.com/u/5446298?v=4" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://avatars.githubusercontent.com/u/5446298?v=4" alt="Steven Masley" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
December 13, 2023
|
||||
@@ -22,7 +22,7 @@ roles.
|
||||
|
||||
You may use a hybrid of the following approaches.
|
||||
|
||||
# (Easiest) Sync using Okta Groups
|
||||
## (Easiest) Sync using Okta Groups
|
||||
|
||||
If the Coder roles & Coder groups can be inferred from
|
||||
[Okta groups](https://help.okta.com/en-us/content/topics/users-groups-profiles/usgp-about-groups.htm),
|
||||
@@ -67,7 +67,7 @@ CODER_OIDC_USER_ROLE_FIELD=groups
|
||||
CODER_OIDC_USER_ROLE_MAPPING='{"admin-group":["template-admin","user-admin"]}'
|
||||
```
|
||||
|
||||
# (Easy) Mapping Okta profile attributes
|
||||
## (Easy) Mapping Okta profile attributes
|
||||
|
||||
If roles or groups cannot be completely inferred from Okta group memberships,
|
||||
another option is to source them from a user’s attributes. The user attribute
|
||||
@@ -105,7 +105,7 @@ CODER_OIDC_USER_ROLE_MAPPING='{"admin-group":["template-admin","user-admin"]}'
|
||||
# CODER_OIDC_GROUP_FIELD=...
|
||||
```
|
||||
|
||||
# (Advanced) Custom scopes to retrieve custom claims
|
||||
## (Advanced) Custom scopes to retrieve custom claims
|
||||
|
||||
Okta does not support setting custom scopes and claims in the default
|
||||
authorization server used by your application. If you require this
|
||||
|
||||
@@ -3,7 +3,7 @@
|
||||
<div>
|
||||
<a href="https://github.com/coder" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Your Name</span>
|
||||
<img src="https://github.com/coder.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/coder.png" alt="Coder" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
December 13, 2023
|
||||
|
||||
@@ -44,9 +44,9 @@ CREATE SCHEMA myschema;
|
||||
|
||||
Once the schema is created, you can list all schemas with `\dn`:
|
||||
|
||||
```
|
||||
List of schemas
|
||||
Name | Owner
|
||||
```text
|
||||
List of schemas
|
||||
Name | Owner
|
||||
-----------+----------
|
||||
myschema | coder
|
||||
public | postgres
|
||||
|
||||
+64
-64
@@ -8,9 +8,9 @@ For other community resources, see our
|
||||
[GitHub discussions](https://github.com/coder/coder/discussions), or join our
|
||||
[Discord server](https://discord.gg/coder).
|
||||
|
||||
### How do I add a Premium trial license?
|
||||
## How do I add a Premium trial license?
|
||||
|
||||
Visit https://coder.com/trial or contact
|
||||
Visit <https://coder.com/trial> or contact
|
||||
|
||||
[sales@coder.com](mailto:sales@coder.com?subject=License) to get a trial key.
|
||||
|
||||
@@ -34,7 +34,7 @@ If the license is in a file:
|
||||
coder licenses add -f <path/filename>
|
||||
```
|
||||
|
||||
### I'm experiencing networking issues, so want to disable Tailscale, STUN, Direct connections and force use of websocket
|
||||
## I'm experiencing networking issues, so want to disable Tailscale, STUN, Direct connections and force use of websocket
|
||||
|
||||
The primary developer use case is a local IDE connecting over SSH to a Coder
|
||||
workspace.
|
||||
@@ -56,18 +56,18 @@ Setting the following flags as shown disables this logic to simplify
|
||||
troubleshooting.
|
||||
|
||||
| Flag | Value | Meaning |
|
||||
| --------------------------------------------------------------------------------------------- | ----------- | ------------------------------------- |
|
||||
|-----------------------------------------------------------------------------------------------|-------------|---------------------------------------|
|
||||
| [`CODER_BLOCK_DIRECT`](../reference/cli/server.md#--block-direct-connections) | `true` | Blocks direct connections |
|
||||
| [`CODER_DERP_SERVER_STUN_ADDRESSES`](../reference/cli/server.md#--derp-server-stun-addresses) | `"disable"` | Disables STUN |
|
||||
| [`CODER_DERP_FORCE_WEBSOCKETS`](../reference/cli/server.md#--derp-force-websockets) | `true` | Forces websockets over Tailscale DERP |
|
||||
|
||||
### How do I configure NGINX as the reverse proxy in front of Coder?
|
||||
## How do I configure NGINX as the reverse proxy in front of Coder?
|
||||
|
||||
[This tutorial](./reverse-proxy-nginx.md) in our docs explains in detail how to
|
||||
configure NGINX with Coder so that our Tailscale Wireguard networking functions
|
||||
properly.
|
||||
|
||||
### How do I hide some of the default icons in a workspace like VS Code Desktop, Terminal, SSH, Ports?
|
||||
## How do I hide some of the default icons in a workspace like VS Code Desktop, Terminal, SSH, Ports?
|
||||
|
||||
The visibility of Coder apps is configurable in the template. To change the
|
||||
default (shows all), add this block inside the
|
||||
@@ -88,7 +88,7 @@ This example will hide all built-in
|
||||
[`coder_app`](https://registry.terraform.io/providers/coder/coder/latest/docs/resources/app)
|
||||
icons except the web terminal.
|
||||
|
||||
### I want to allow code-server to be accessible by other users in my deployment.
|
||||
## I want to allow code-server to be accessible by other users in my deployment
|
||||
|
||||
> It is **not** recommended to share a web IDE, but if required, the following
|
||||
> deployment environment variable settings are required.
|
||||
@@ -118,7 +118,7 @@ resource "coder_app" "code-server" {
|
||||
}
|
||||
```
|
||||
|
||||
### I installed Coder and created a workspace but the icons do not load.
|
||||
## I installed Coder and created a workspace but the icons do not load
|
||||
|
||||
An important concept to understand is that Coder creates workspaces which have
|
||||
an agent that must be able to reach the `coder server`.
|
||||
@@ -139,9 +139,9 @@ coder server --access-url http://localhost:3000 --address 0.0.0.0:3000
|
||||
```
|
||||
|
||||
> Even `coder server` which creates a reverse proxy, will let you use
|
||||
> http://localhost to access Coder from a browser.
|
||||
> <http://localhost> to access Coder from a browser.
|
||||
|
||||
### I updated a template, and an existing workspace based on that template fails to start.
|
||||
## I updated a template, and an existing workspace based on that template fails to start
|
||||
|
||||
When updating a template, be aware of potential issues with input variables. For
|
||||
example, if a template prompts users to choose options like a
|
||||
@@ -161,7 +161,7 @@ workspace from a failed status.
|
||||
coder update --always-prompt <workspace name>
|
||||
```
|
||||
|
||||
### I'm running coder on a VM with systemd but latest release installed isn't showing up.
|
||||
## I'm running coder on a VM with systemd but latest release installed isn't showing up
|
||||
|
||||
Take, for example, a Coder deployment on a VM with a 2 shared vCPU systemd
|
||||
service. In this scenario, it's necessary to reload the daemon and then restart
|
||||
@@ -176,7 +176,7 @@ sudo systemctl daemon-reload
|
||||
sudo systemctl restart coder.service
|
||||
```
|
||||
|
||||
### I'm using the built-in Postgres database and forgot admin email I set up.
|
||||
## I'm using the built-in Postgres database and forgot admin email I set up
|
||||
|
||||
1. Run the `coder server` command below to retrieve the `psql` connection URL
|
||||
which includes the database user and password.
|
||||
@@ -189,7 +189,7 @@ coder server postgres-builtin-url
|
||||
psql "postgres://coder@localhost:53737/coder?sslmode=disable&password=I2S...pTk"
|
||||
```
|
||||
|
||||
### How to find out Coder's latest Terraform provider version?
|
||||
## How to find out Coder's latest Terraform provider version?
|
||||
|
||||
[Coder is on the HashiCorp's Terraform registry](https://registry.terraform.io/providers/coder/coder/latest).
|
||||
Check this frequently to make sure you are on the latest version.
|
||||
@@ -198,7 +198,7 @@ Sometimes, the version may change and `resource` configurations will either
|
||||
become deprecated or new ones will be added when you get warnings or errors
|
||||
creating and pushing templates.
|
||||
|
||||
### How can I set up TLS for my deployment and not create a signed certificate?
|
||||
## How can I set up TLS for my deployment and not create a signed certificate?
|
||||
|
||||
Caddy is an easy-to-configure reverse proxy that also automatically creates
|
||||
certificates from Let's Encrypt.
|
||||
@@ -223,7 +223,7 @@ coder.example.com {
|
||||
}
|
||||
```
|
||||
|
||||
### I'm using Caddy as my reverse proxy in front of Coder. How do I set up a wildcard domain for port forwarding?
|
||||
## I'm using Caddy as my reverse proxy in front of Coder. How do I set up a wildcard domain for port forwarding?
|
||||
|
||||
Caddy requires your DNS provider's credentials to create wildcard certificates.
|
||||
This involves building the Caddy binary
|
||||
@@ -253,7 +253,7 @@ The updated Caddyfile configuration will look like this:
|
||||
}
|
||||
```
|
||||
|
||||
### Can I use local or remote Terraform Modules in Coder templates?
|
||||
## Can I use local or remote Terraform Modules in Coder templates?
|
||||
|
||||
One way is to reference a Terraform module from a GitHub repo to avoid
|
||||
duplication and then just extend it or pass template-specific
|
||||
@@ -296,7 +296,7 @@ References:
|
||||
- [Public GitHub Issue 5677](https://github.com/coder/coder/issues/5677)
|
||||
- [Coder docs: Templates/Change Management](../admin/templates/managing-templates/change-management.md)
|
||||
|
||||
### Can I run Coder in an air-gapped or offline mode? (no Internet)?
|
||||
## Can I run Coder in an air-gapped or offline mode? (no Internet)?
|
||||
|
||||
Yes, Coder can be deployed in
|
||||
[air-gapped or offline mode](../install/offline.md).
|
||||
@@ -310,7 +310,7 @@ defaults to Google's STUN servers, so you can either create your STUN server in
|
||||
your network or disable and force all traffic through the control plane's DERP
|
||||
proxy.
|
||||
|
||||
### Create a randomized computer_name for an Azure VM
|
||||
## Create a randomized computer_name for an Azure VM
|
||||
|
||||
Azure VMs have a 15 character limit for the `computer_name` which can lead to
|
||||
duplicate name errors.
|
||||
@@ -325,7 +325,7 @@ locals {
|
||||
}
|
||||
```
|
||||
|
||||
### Do you have example JetBrains Gateway templates?
|
||||
## Do you have example JetBrains Gateway templates?
|
||||
|
||||
In August 2023, JetBrains certified the Coder plugin signifying enhanced
|
||||
stability and reliability.
|
||||
@@ -347,7 +347,7 @@ open the IDE.
|
||||
- [IntelliJ IDEA](https://github.com/sharkymark/v2-templates/tree/main/src/pod-idea)
|
||||
- [IntelliJ IDEA with Icon](https://github.com/sharkymark/v2-templates/tree/main/src/pod-idea-icon)
|
||||
|
||||
### What options do I have for adding VS Code extensions into code-server, VS Code Desktop or Microsoft's Code Server?
|
||||
## What options do I have for adding VS Code extensions into code-server, VS Code Desktop or Microsoft's Code Server?
|
||||
|
||||
Coder has an open-source project called
|
||||
[`code-marketplace`](https://github.com/coder/code-marketplace) which is a
|
||||
@@ -371,7 +371,7 @@ Microsoft's marketplace.
|
||||
> Note: these are example templates with no SLAs on them and are not guaranteed
|
||||
> for long-term support.
|
||||
|
||||
### I want to run Docker for my workspaces but not install Docker Desktop.
|
||||
## I want to run Docker for my workspaces but not install Docker Desktop
|
||||
|
||||
[Colima](https://github.com/abiosoft/colima) is a Docker Desktop alternative.
|
||||
|
||||
@@ -406,7 +406,7 @@ Colima will show the path to the docker socket so we have a
|
||||
[community template](https://github.com/sharkymark/v2-templates/tree/main/src/docker-code-server)
|
||||
that prompts the Coder admin to enter the docker socket as a Terraform variable.
|
||||
|
||||
### How to make a `coder_app` optional?
|
||||
## How to make a `coder_app` optional?
|
||||
|
||||
An example use case is the user should decide if they want a browser-based IDE
|
||||
like code-server when creating the workspace.
|
||||
@@ -414,57 +414,57 @@ like code-server when creating the workspace.
|
||||
1. Add a `coder_parameter` with type `bool` to ask the user if they want the
|
||||
code-server IDE
|
||||
|
||||
```tf
|
||||
data "coder_parameter" "code_server" {
|
||||
name = "Do you want code-server in your workspace?"
|
||||
description = "Use VS Code in a browser."
|
||||
type = "bool"
|
||||
default = false
|
||||
mutable = true
|
||||
icon = "/icon/code.svg"
|
||||
order = 6
|
||||
}
|
||||
```
|
||||
```tf
|
||||
data "coder_parameter" "code_server" {
|
||||
name = "Do you want code-server in your workspace?"
|
||||
description = "Use VS Code in a browser."
|
||||
type = "bool"
|
||||
default = false
|
||||
mutable = true
|
||||
icon = "/icon/code.svg"
|
||||
order = 6
|
||||
}
|
||||
```
|
||||
|
||||
2. Add conditional logic to the `startup_script` to install and start
|
||||
code-server depending on the value of the added `coder_parameter`
|
||||
|
||||
```sh
|
||||
# install and start code-server, VS Code in a browser
|
||||
```sh
|
||||
# install and start code-server, VS Code in a browser
|
||||
|
||||
if [ ${data.coder_parameter.code_server.value} = true ]; then
|
||||
echo "🧑🏼💻 Downloading and installing the latest code-server IDE..."
|
||||
curl -fsSL https://code-server.dev/install.sh | sh
|
||||
code-server --auth none --port 13337 >/dev/null 2>&1 &
|
||||
fi
|
||||
```
|
||||
if [ ${data.coder_parameter.code_server.value} = true ]; then
|
||||
echo "🧑🏼💻 Downloading and installing the latest code-server IDE..."
|
||||
curl -fsSL https://code-server.dev/install.sh | sh
|
||||
code-server --auth none --port 13337 >/dev/null 2>&1 &
|
||||
fi
|
||||
```
|
||||
|
||||
3. Add a Terraform meta-argument
|
||||
[`count`](https://developer.hashicorp.com/terraform/language/meta-arguments/count)
|
||||
in the `coder_app` resource so it will only create the resource if the
|
||||
`coder_parameter` is `true`
|
||||
|
||||
```tf
|
||||
# code-server
|
||||
resource "coder_app" "code-server" {
|
||||
count = data.coder_parameter.code_server.value ? 1 : 0
|
||||
agent_id = coder_agent.coder.id
|
||||
slug = "code-server"
|
||||
display_name = "code-server"
|
||||
icon = "/icon/code.svg"
|
||||
url = "http://localhost:13337?folder=/home/coder"
|
||||
subdomain = false
|
||||
share = "owner"
|
||||
```tf
|
||||
# code-server
|
||||
resource "coder_app" "code-server" {
|
||||
count = data.coder_parameter.code_server.value ? 1 : 0
|
||||
agent_id = coder_agent.coder.id
|
||||
slug = "code-server"
|
||||
display_name = "code-server"
|
||||
icon = "/icon/code.svg"
|
||||
url = "http://localhost:13337?folder=/home/coder"
|
||||
subdomain = false
|
||||
share = "owner"
|
||||
|
||||
healthcheck {
|
||||
url = "http://localhost:13337/healthz"
|
||||
interval = 3
|
||||
threshold = 10
|
||||
}
|
||||
}
|
||||
```
|
||||
healthcheck {
|
||||
url = "http://localhost:13337/healthz"
|
||||
interval = 3
|
||||
threshold = 10
|
||||
}
|
||||
}
|
||||
```
|
||||
|
||||
### Why am I getting this "remote host doesn't meet VS Code Server's prerequisites" error when opening up VSCode remote in a Linux environment?
|
||||
## Why am I getting this "remote host doesn't meet VS Code Server's prerequisites" error when opening up VSCode remote in a Linux environment?
|
||||
|
||||
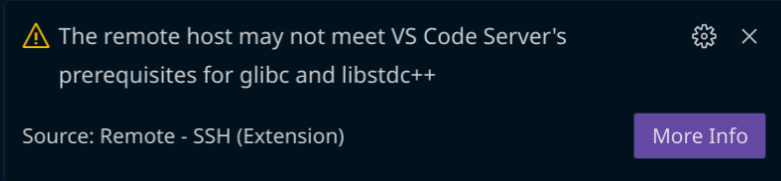
|
||||
|
||||
@@ -473,9 +473,9 @@ or VM/VPS doesn't have the proper C libraries to run the VS Code Server. For
|
||||
instance, Alpine is not supported at all. If so, you need to find a container
|
||||
image or supported OS for the VS Code Server. For more information on OS
|
||||
prerequisites for Linux, please look at the VSCode docs.
|
||||
https://code.visualstudio.com/docs/remote/linux#_local-linux-prerequisites
|
||||
<https://code.visualstudio.com/docs/remote/linux#_local-linux-prerequisites>
|
||||
|
||||
### How can I resolve disconnects when connected to Coder via JetBrains Gateway?
|
||||
## How can I resolve disconnects when connected to Coder via JetBrains Gateway?
|
||||
|
||||
If your JetBrains IDE is disconnected for a long period of time due to a network
|
||||
change (for example turning off a VPN), you may find that the IDE will not
|
||||
@@ -504,7 +504,7 @@ config file will be overwritten by the JetBrains Gateway client when it
|
||||
re-authenticates to your Coder deployment so you must add the above config as a
|
||||
separate block and not add it to any existing ones.
|
||||
|
||||
### How can I restrict inbound/outbound file transfers from Coder workspaces?
|
||||
## How can I restrict inbound/outbound file transfers from Coder workspaces?
|
||||
|
||||
In certain environments, it is essential to keep confidential files within
|
||||
workspaces and prevent users from uploading or downloading resources using tools
|
||||
@@ -526,7 +526,7 @@ resource "docker_container" "workspace" {
|
||||
}
|
||||
```
|
||||
|
||||
#### Important Notice
|
||||
### Important Notice
|
||||
|
||||
This control operates at the `ssh-exec` level or during `sftp` sessions. While
|
||||
it can help prevent automated file transfers using the specified tools, users
|
||||
|
||||
@@ -3,7 +3,7 @@
|
||||
<div>
|
||||
<a href="https://github.com/ericpaulsen" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Eric Paulsen</span>
|
||||
<img src="https://github.com/ericpaulsen.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/ericpaulsen.png" alt="ericpaulsen" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
January 4, 2024
|
||||
@@ -39,21 +39,21 @@ following:
|
||||
|
||||
```json
|
||||
{
|
||||
"Version": "2012-10-17",
|
||||
"Statement": [
|
||||
{
|
||||
"Effect": "Allow",
|
||||
"Principal": {
|
||||
"Federated": "accounts.google.com"
|
||||
},
|
||||
"Action": "sts:AssumeRoleWithWebIdentity",
|
||||
"Condition": {
|
||||
"StringEquals": {
|
||||
"accounts.google.com:aud": "<enter-OAuth-client-ID-here"
|
||||
}
|
||||
}
|
||||
}
|
||||
]
|
||||
"Version": "2012-10-17",
|
||||
"Statement": [
|
||||
{
|
||||
"Effect": "Allow",
|
||||
"Principal": {
|
||||
"Federated": "accounts.google.com"
|
||||
},
|
||||
"Action": "sts:AssumeRoleWithWebIdentity",
|
||||
"Condition": {
|
||||
"StringEquals": {
|
||||
"accounts.google.com:aud": "<enter-OAuth-client-ID-here"
|
||||
}
|
||||
}
|
||||
}
|
||||
]
|
||||
}
|
||||
```
|
||||
|
||||
@@ -64,50 +64,50 @@ following policy to the role:
|
||||
|
||||
```json
|
||||
{
|
||||
"Version": "2012-10-17",
|
||||
"Statement": [
|
||||
{
|
||||
"Sid": "VisualEditor0",
|
||||
"Effect": "Allow",
|
||||
"Action": [
|
||||
"ec2:GetDefaultCreditSpecification",
|
||||
"ec2:DescribeIamInstanceProfileAssociations",
|
||||
"ec2:DescribeTags",
|
||||
"ec2:DescribeInstances",
|
||||
"ec2:DescribeInstanceTypes",
|
||||
"ec2:CreateTags",
|
||||
"ec2:RunInstances",
|
||||
"ec2:DescribeInstanceCreditSpecifications",
|
||||
"ec2:DescribeImages",
|
||||
"ec2:ModifyDefaultCreditSpecification",
|
||||
"ec2:DescribeVolumes"
|
||||
],
|
||||
"Resource": "*"
|
||||
},
|
||||
{
|
||||
"Sid": "CoderResources",
|
||||
"Effect": "Allow",
|
||||
"Action": [
|
||||
"ec2:DescribeInstanceAttribute",
|
||||
"ec2:UnmonitorInstances",
|
||||
"ec2:TerminateInstances",
|
||||
"ec2:StartInstances",
|
||||
"ec2:StopInstances",
|
||||
"ec2:DeleteTags",
|
||||
"ec2:MonitorInstances",
|
||||
"ec2:CreateTags",
|
||||
"ec2:RunInstances",
|
||||
"ec2:ModifyInstanceAttribute",
|
||||
"ec2:ModifyInstanceCreditSpecification"
|
||||
],
|
||||
"Resource": "arn:aws:ec2:*:*:instance/*",
|
||||
"Condition": {
|
||||
"StringEquals": {
|
||||
"aws:ResourceTag/Coder_Provisioned": "true"
|
||||
}
|
||||
}
|
||||
}
|
||||
]
|
||||
"Version": "2012-10-17",
|
||||
"Statement": [
|
||||
{
|
||||
"Sid": "VisualEditor0",
|
||||
"Effect": "Allow",
|
||||
"Action": [
|
||||
"ec2:GetDefaultCreditSpecification",
|
||||
"ec2:DescribeIamInstanceProfileAssociations",
|
||||
"ec2:DescribeTags",
|
||||
"ec2:DescribeInstances",
|
||||
"ec2:DescribeInstanceTypes",
|
||||
"ec2:CreateTags",
|
||||
"ec2:RunInstances",
|
||||
"ec2:DescribeInstanceCreditSpecifications",
|
||||
"ec2:DescribeImages",
|
||||
"ec2:ModifyDefaultCreditSpecification",
|
||||
"ec2:DescribeVolumes"
|
||||
],
|
||||
"Resource": "*"
|
||||
},
|
||||
{
|
||||
"Sid": "CoderResources",
|
||||
"Effect": "Allow",
|
||||
"Action": [
|
||||
"ec2:DescribeInstanceAttribute",
|
||||
"ec2:UnmonitorInstances",
|
||||
"ec2:TerminateInstances",
|
||||
"ec2:StartInstances",
|
||||
"ec2:StopInstances",
|
||||
"ec2:DeleteTags",
|
||||
"ec2:MonitorInstances",
|
||||
"ec2:CreateTags",
|
||||
"ec2:RunInstances",
|
||||
"ec2:ModifyInstanceAttribute",
|
||||
"ec2:ModifyInstanceCreditSpecification"
|
||||
],
|
||||
"Resource": "arn:aws:ec2:*:*:instance/*",
|
||||
"Condition": {
|
||||
"StringEquals": {
|
||||
"aws:ResourceTag/Coder_Provisioned": "true"
|
||||
}
|
||||
}
|
||||
}
|
||||
]
|
||||
}
|
||||
```
|
||||
|
||||
|
||||
@@ -3,7 +3,7 @@
|
||||
<div>
|
||||
<a href="https://github.com/ericpaulsen" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Eric Paulsen</span>
|
||||
<img src="https://github.com/ericpaulsen.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/ericpaulsen.png" alt="ericpaulsen" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
January 12, 2024
|
||||
@@ -23,12 +23,12 @@ actual Docker registry URL, username, and password.
|
||||
|
||||
```json
|
||||
{
|
||||
"auths": {
|
||||
"<your-registry>": {
|
||||
"username": "<your-username>",
|
||||
"password": "<your-password>"
|
||||
}
|
||||
}
|
||||
"auths": {
|
||||
"<your-registry>": {
|
||||
"username": "<your-username>",
|
||||
"password": "<your-password>"
|
||||
}
|
||||
}
|
||||
}
|
||||
```
|
||||
|
||||
@@ -54,13 +54,13 @@ The output should look similar to this:
|
||||
|
||||
```json
|
||||
{
|
||||
"auths": {
|
||||
"your.private.registry.com": {
|
||||
"username": "ericpaulsen",
|
||||
"password": "xxxx",
|
||||
"auth": "c3R...zE2"
|
||||
}
|
||||
}
|
||||
"auths": {
|
||||
"your.private.registry.com": {
|
||||
"username": "ericpaulsen",
|
||||
"password": "xxxx",
|
||||
"auth": "c3R...zE2"
|
||||
}
|
||||
}
|
||||
}
|
||||
```
|
||||
|
||||
|
||||
@@ -3,7 +3,7 @@
|
||||
<div>
|
||||
<a href="https://github.com/ericpaulsen" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Eric Paulsen</span>
|
||||
<img src="https://github.com/ericpaulsen.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/ericpaulsen.png" alt="ericpaulsen" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
</a>
|
||||
</div>
|
||||
February 24, 2024
|
||||
|
||||
@@ -16,82 +16,82 @@ certificates, you'll need a domain name that resolves to your Caddy server.
|
||||
```yaml
|
||||
services:
|
||||
coder:
|
||||
image: ghcr.io/coder/coder:${CODER_VERSION:-latest}
|
||||
environment:
|
||||
CODER_PG_CONNECTION_URL: "postgresql://${POSTGRES_USER:-username}:${POSTGRES_PASSWORD:-password}@database/${POSTGRES_DB:-coder}?sslmode=disable"
|
||||
CODER_HTTP_ADDRESS: "0.0.0.0:7080"
|
||||
# You'll need to set CODER_ACCESS_URL to an IP or domain
|
||||
# that workspaces can reach. This cannot be localhost
|
||||
# or 127.0.0.1 for non-Docker templates!
|
||||
CODER_ACCESS_URL: "${CODER_ACCESS_URL}"
|
||||
# Optional) Enable wildcard apps/dashboard port forwarding
|
||||
CODER_WILDCARD_ACCESS_URL: "${CODER_WILDCARD_ACCESS_URL}"
|
||||
# If the coder user does not have write permissions on
|
||||
# the docker socket, you can uncomment the following
|
||||
# lines and set the group ID to one that has write
|
||||
# permissions on the docker socket.
|
||||
#group_add:
|
||||
# - "998" # docker group on host
|
||||
volumes:
|
||||
- /var/run/docker.sock:/var/run/docker.sock
|
||||
depends_on:
|
||||
database:
|
||||
condition: service_healthy
|
||||
image: ghcr.io/coder/coder:${CODER_VERSION:-latest}
|
||||
environment:
|
||||
CODER_PG_CONNECTION_URL: "postgresql://${POSTGRES_USER:-username}:${POSTGRES_PASSWORD:-password}@database/${POSTGRES_DB:-coder}?sslmode=disable"
|
||||
CODER_HTTP_ADDRESS: "0.0.0.0:7080"
|
||||
# You'll need to set CODER_ACCESS_URL to an IP or domain
|
||||
# that workspaces can reach. This cannot be localhost
|
||||
# or 127.0.0.1 for non-Docker templates!
|
||||
CODER_ACCESS_URL: "${CODER_ACCESS_URL}"
|
||||
# Optional) Enable wildcard apps/dashboard port forwarding
|
||||
CODER_WILDCARD_ACCESS_URL: "${CODER_WILDCARD_ACCESS_URL}"
|
||||
# If the coder user does not have write permissions on
|
||||
# the docker socket, you can uncomment the following
|
||||
# lines and set the group ID to one that has write
|
||||
# permissions on the docker socket.
|
||||
#group_add:
|
||||
# - "998" # docker group on host
|
||||
volumes:
|
||||
- /var/run/docker.sock:/var/run/docker.sock
|
||||
depends_on:
|
||||
database:
|
||||
condition: service_healthy
|
||||
|
||||
database:
|
||||
image: "postgres:16"
|
||||
ports:
|
||||
- "5432:5432"
|
||||
environment:
|
||||
POSTGRES_USER: ${POSTGRES_USER:-username} # The PostgreSQL user (useful to connect to the database)
|
||||
POSTGRES_PASSWORD: ${POSTGRES_PASSWORD:-password} # The PostgreSQL password (useful to connect to the database)
|
||||
POSTGRES_DB: ${POSTGRES_DB:-coder} # The PostgreSQL default database (automatically created at first launch)
|
||||
volumes:
|
||||
- coder_data:/var/lib/postgresql/data # Use "docker volume rm coder_coder_data" to reset Coder
|
||||
healthcheck:
|
||||
test:
|
||||
[
|
||||
"CMD-SHELL",
|
||||
"pg_isready -U ${POSTGRES_USER:-username} -d ${POSTGRES_DB:-coder}",
|
||||
]
|
||||
interval: 5s
|
||||
timeout: 5s
|
||||
retries: 5
|
||||
image: "postgres:16"
|
||||
ports:
|
||||
- "5432:5432"
|
||||
environment:
|
||||
POSTGRES_USER: ${POSTGRES_USER:-username} # The PostgreSQL user (useful to connect to the database)
|
||||
POSTGRES_PASSWORD: ${POSTGRES_PASSWORD:-password} # The PostgreSQL password (useful to connect to the database)
|
||||
POSTGRES_DB: ${POSTGRES_DB:-coder} # The PostgreSQL default database (automatically created at first launch)
|
||||
volumes:
|
||||
- coder_data:/var/lib/postgresql/data # Use "docker volume rm coder_coder_data" to reset Coder
|
||||
healthcheck:
|
||||
test:
|
||||
[
|
||||
"CMD-SHELL",
|
||||
"pg_isready -U ${POSTGRES_USER:-username} -d ${POSTGRES_DB:-coder}",
|
||||
]
|
||||
interval: 5s
|
||||
timeout: 5s
|
||||
retries: 5
|
||||
|
||||
caddy:
|
||||
image: caddy:2.6.2
|
||||
ports:
|
||||
- "80:80"
|
||||
- "443:443"
|
||||
- "443:443/udp"
|
||||
volumes:
|
||||
- $PWD/Caddyfile:/etc/caddy/Caddyfile
|
||||
- caddy_data:/data
|
||||
- caddy_config:/config
|
||||
image: caddy:2.6.2
|
||||
ports:
|
||||
- "80:80"
|
||||
- "443:443"
|
||||
- "443:443/udp"
|
||||
volumes:
|
||||
- $PWD/Caddyfile:/etc/caddy/Caddyfile
|
||||
- caddy_data:/data
|
||||
- caddy_config:/config
|
||||
|
||||
volumes:
|
||||
coder_data:
|
||||
caddy_data:
|
||||
caddy_config:
|
||||
coder_data:
|
||||
caddy_data:
|
||||
caddy_config:
|
||||
```
|
||||
|
||||
3. Create a `Caddyfile` and add the following:
|
||||
|
||||
```caddyfile
|
||||
{
|
||||
on_demand_tls {
|
||||
ask http://example.com
|
||||
}
|
||||
on_demand_tls {
|
||||
ask http://example.com
|
||||
}
|
||||
}
|
||||
|
||||
coder.example.com, *.coder.example.com {
|
||||
reverse_proxy coder:7080
|
||||
tls {
|
||||
on_demand
|
||||
on_demand
|
||||
issuer acme {
|
||||
email email@example.com
|
||||
}
|
||||
}
|
||||
}
|
||||
}
|
||||
```
|
||||
|
||||
@@ -124,9 +124,9 @@ certificates, you'll need a domain name that resolves to your Caddy server.
|
||||
|
||||
```caddyfile
|
||||
{
|
||||
on_demand_tls {
|
||||
ask http://example.com
|
||||
}
|
||||
on_demand_tls {
|
||||
ask http://example.com
|
||||
}
|
||||
}
|
||||
|
||||
coder.example.com, *.coder.example.com {
|
||||
|
||||
@@ -27,7 +27,7 @@ A brief overview of all files contained in the bundle is provided below:
|
||||
> out of scope, as support bundles are primarily intended for internal use.
|
||||
|
||||
| Filename | Description |
|
||||
| --------------------------------- | ---------------------------------------------------------------------------------------------------------- |
|
||||
|-----------------------------------|------------------------------------------------------------------------------------------------------------|
|
||||
| `agent/agent.json` | The agent used to connect to the workspace with environment variables stripped. |
|
||||
| `agent/agent_magicsock.html` | The contents of the HTTP debug endpoint of the agent's Tailscale Wireguard connection. |
|
||||
| `agent/client_magicsock.html` | The contents of the HTTP debug endpoint of the client's Tailscale Wireguard connection. |
|
||||
|
||||
@@ -46,15 +46,15 @@ and save the following text in `Dockerfile` then exit the editor:
|
||||
FROM ubuntu
|
||||
|
||||
RUN apt-get update \
|
||||
&& apt-get install -y \
|
||||
sudo \
|
||||
curl \
|
||||
&& rm -rf /var/lib/apt/lists/*
|
||||
&& apt-get install -y \
|
||||
sudo \
|
||||
curl \
|
||||
&& rm -rf /var/lib/apt/lists/*
|
||||
|
||||
ARG USER=coder
|
||||
RUN useradd --groups sudo --no-create-home --shell /bin/bash ${USER} \
|
||||
&& echo "${USER} ALL=(ALL) NOPASSWD:ALL" >/etc/sudoers.d/${USER} \
|
||||
&& chmod 0440 /etc/sudoers.d/${USER}
|
||||
&& echo "${USER} ALL=(ALL) NOPASSWD:ALL" >/etc/sudoers.d/${USER} \
|
||||
&& chmod 0440 /etc/sudoers.d/${USER}
|
||||
USER ${USER}
|
||||
WORKDIR /home/${USER}
|
||||
```
|
||||
@@ -340,7 +340,7 @@ use the Coder CLI.
|
||||
Attempting to authenticate with config URL: 'https://coder.example.com'
|
||||
Open the following in your browser:
|
||||
|
||||
https://coder.example.com/cli-auth
|
||||
https://coder.example.com/cli-auth
|
||||
|
||||
> Paste your token here:
|
||||
```
|
||||
|
||||
@@ -3,7 +3,8 @@
|
||||
<div>
|
||||
<a href="https://github.com/matifali" style="text-decoration: none; color: inherit;">
|
||||
<span style="vertical-align:middle;">Muhammad Atif Ali</span>
|
||||
<img src="https://github.com/matifali.png" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
<img src="https://github.com/matifali.png" alt="matifali" width="24px" height="24px" style="vertical-align:middle; margin: 0px;"/>
|
||||
|
||||
</a>
|
||||
</div>
|
||||
November 15, 2024
|
||||
|
||||
Reference in New Issue
Block a user